


$1 Billion Institution Precisely Targeted, Recapping the Lighter "Hack" Saga


- Key Takeaways:Lighter experienced an anomalous outflow of approximately $15 million, but the protocol itself was not breached. The attacker is suspected of exploiting leaked trading API keys from Abraxas Capital, arbitraging withdrawals through a design flaw in which internal transfers within the public pool do not increase shares.
- Key Elements:
- The attacking wallet started with only about $10,000, first validating the path with a small amount before scaling up operations, withdrawing approximately $10.39 million and $5.097 million USDC from two victim accounts respectively.
- Core vulnerability: When victim accounts made internal transfers to the public pool via API, shares were not increased, allowing the attacker holding 99.99% of shares to redeem assets in excess.
- The compromised accounts have on-chain connections to Abraxas Capital, and the attacker is suspected of obtaining its trading API keys; the institution has consistently managed over $1 billion in assets.
- LIT perpetual contracts retraced approximately 14.8% within minutes, and Lighter preventively suspended all withdrawals and public pool creation at 19:02.
- Funds were bridged via Arbitrum to Hyperliquid, used to purchase approximately 552 XMR1, and split into transfers of 160 ETH each.
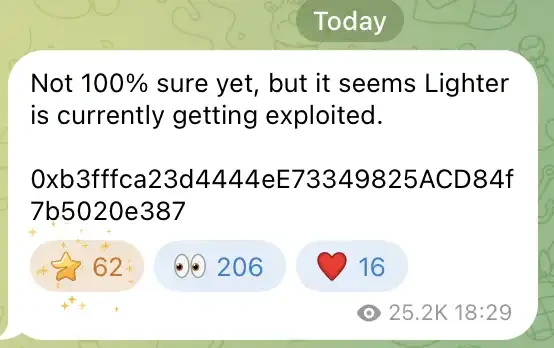
On the evening of November 16, on-chain detective MLM detected an anomalous withdrawal of 10.39 million USDC on Lighter, pushing Lighter into the spotlight of a security incident. A wallet that started with only about $10,000 withdrew a large sum from the platform, quickly swapped it into ETH, and then split it across different addresses. Meanwhile, the price of LIT briefly dropped about 8%.
News that "Lighter was hacked" spread quickly. But as the fund path gradually became clear, subsequent analysis pointed the attack target at institutional accounts, with the clues leading to Abraxas Capital. The attacker is suspected of obtaining its trading API keys and then exploiting the permission design of public pools to move the funds in the account into their own hands. The Lighter protocol itself was not hacked.
The Attack Began with a Small Test
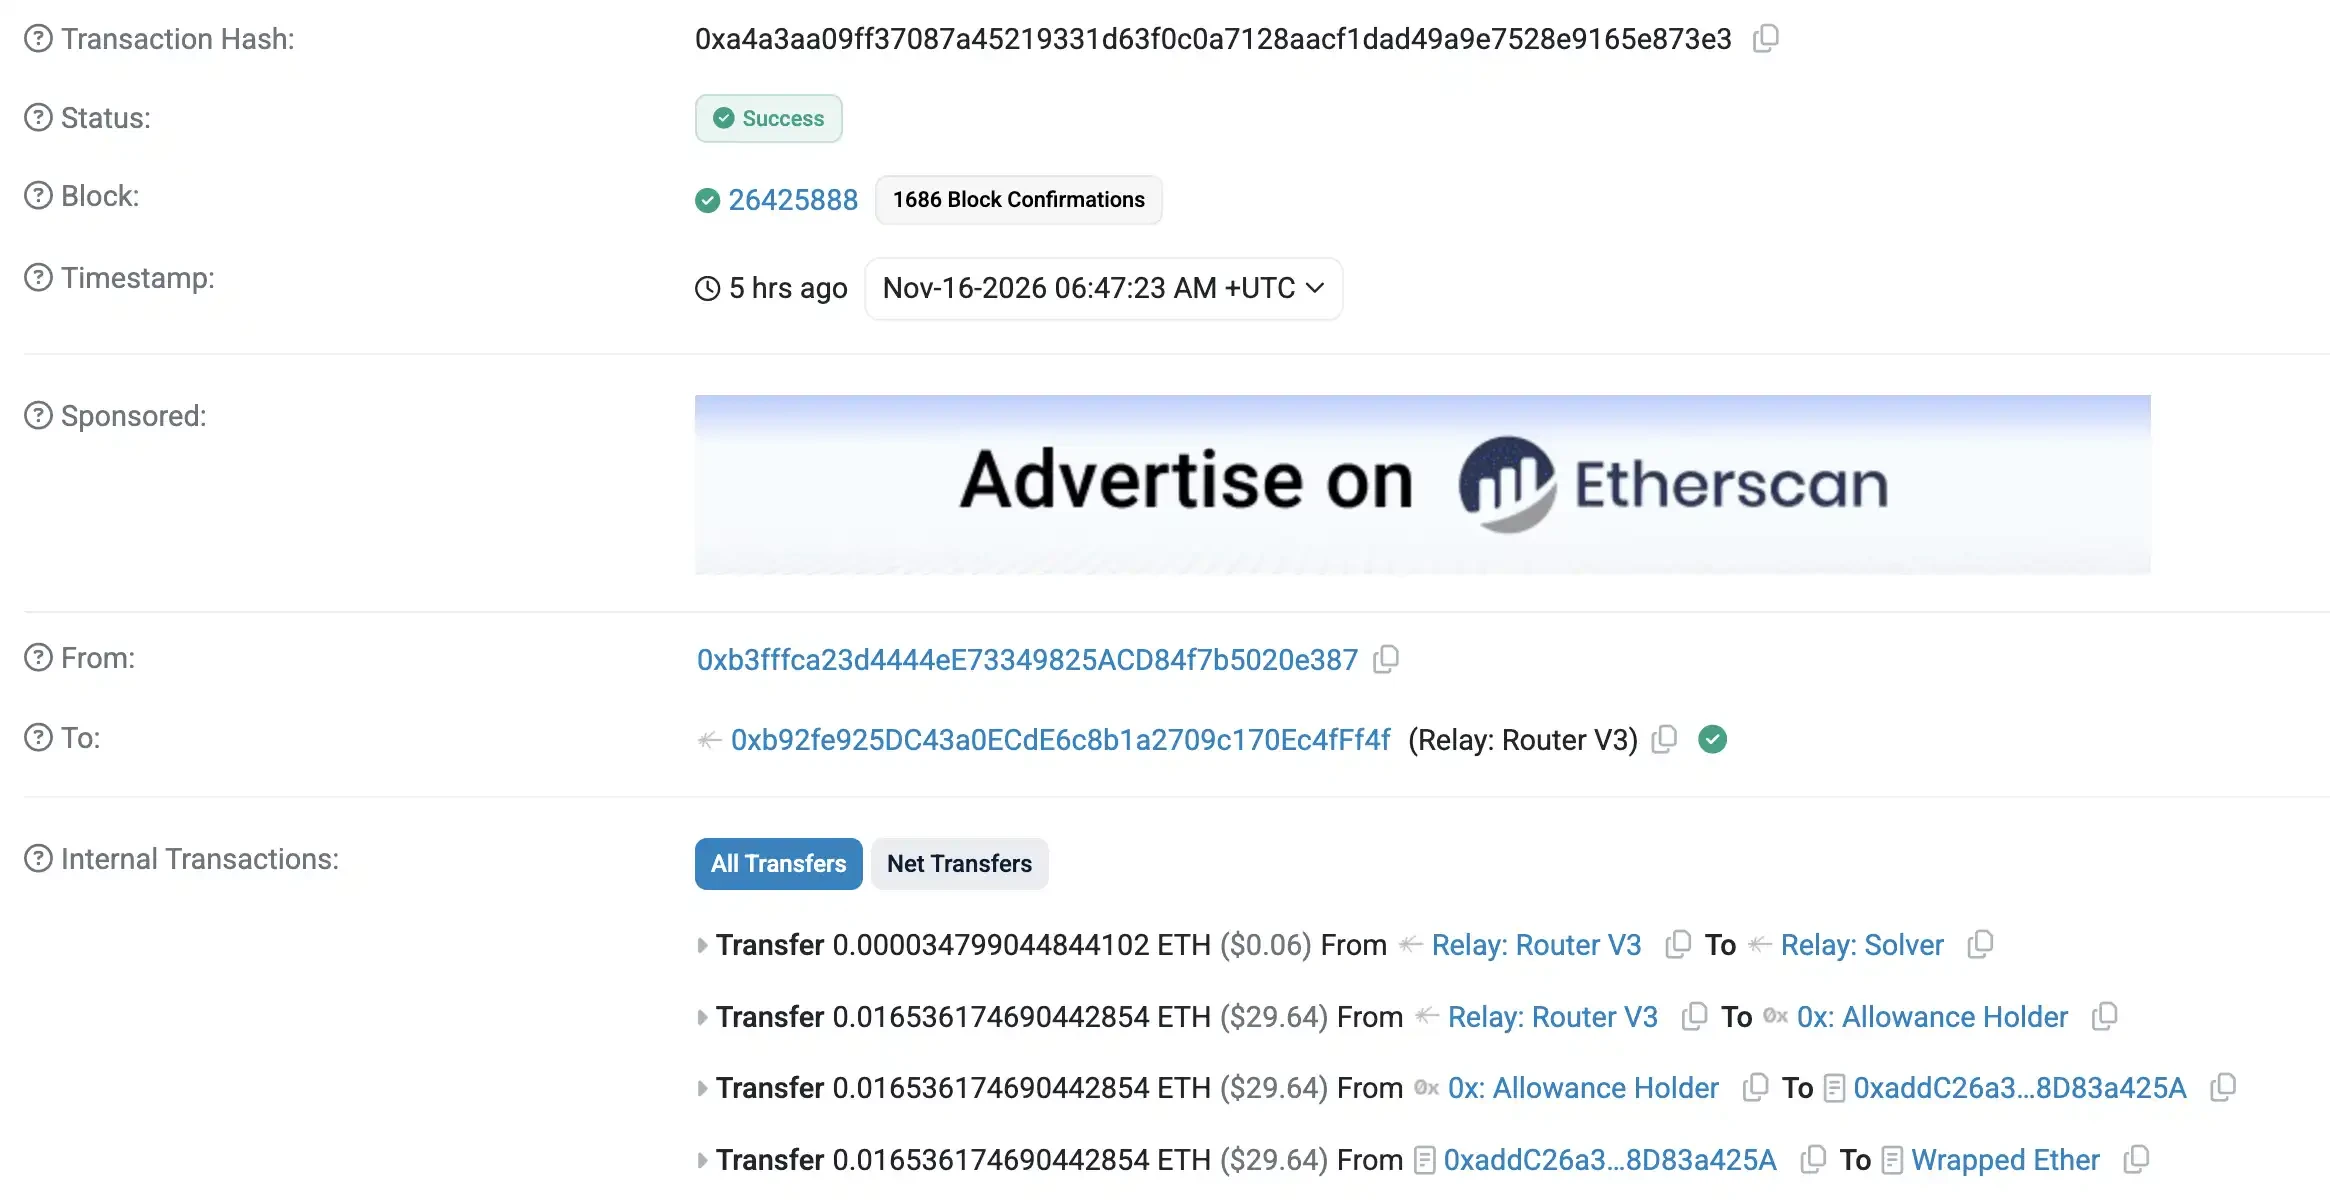
The attacking address is a wallet ending in 0xb3ff, corresponding to Lighter account #769455. Its preparations began several hours earlier than the community warning.
At 14:47:23, this address swapped a small amount of ETH for 29.959999 USDC via the Relay router and deposited it directly into Lighter.
At 16:45, about 10,500 USDC reached the address via cross-chain transfer. At 17:35, the hacker deposited 10,200 USDC into Lighter and began preparing for the first round of operations.
At 17:40:10, Lighter account 714710 (the victim account) created a public pool with a 0 fee. Initially, the victim account bought a pool share with 1 USDC, while the hacker put 9,999 USDC into the pool and obtained a 99.99% share.
This arrangement exploited the dual identity of public pools.
For the pool creator (the victim account), the public pool is an account under its own Ethereum address, allowing internal fund transfers via the API without additional signatures. For external participants, the public pool allows them to purchase shares and redeem assets in proportion to their holdings.
A normal subscription would yield corresponding shares. This time, the victim account used an "internal transfer," and when the funds entered the pool, no corresponding shares were added for it. As a result, the more money transferred into the pool, the more assets the attacker, who already held a 99.99% share, could redeem. This can perhaps be understood as a bug in Lighter.
The attacker first verified this path with 1 USDC.
At 17:44:13, the victim account internally transferred 1 USDC into the public pool. In less than 3 seconds, the attacker redeemed 9,999.9999 USDC. The attacker then put the funds back into the pool and began scaling up the same operation.
At 17:45, the victim account made ten consecutive transfers of 1 million USDC each, followed by an additional remainder of about 384,000 USDC. At 17:45:38, the attacker redeemed about 10.393 million USDC and immediately initiated a mainnet withdrawal.
Timeline
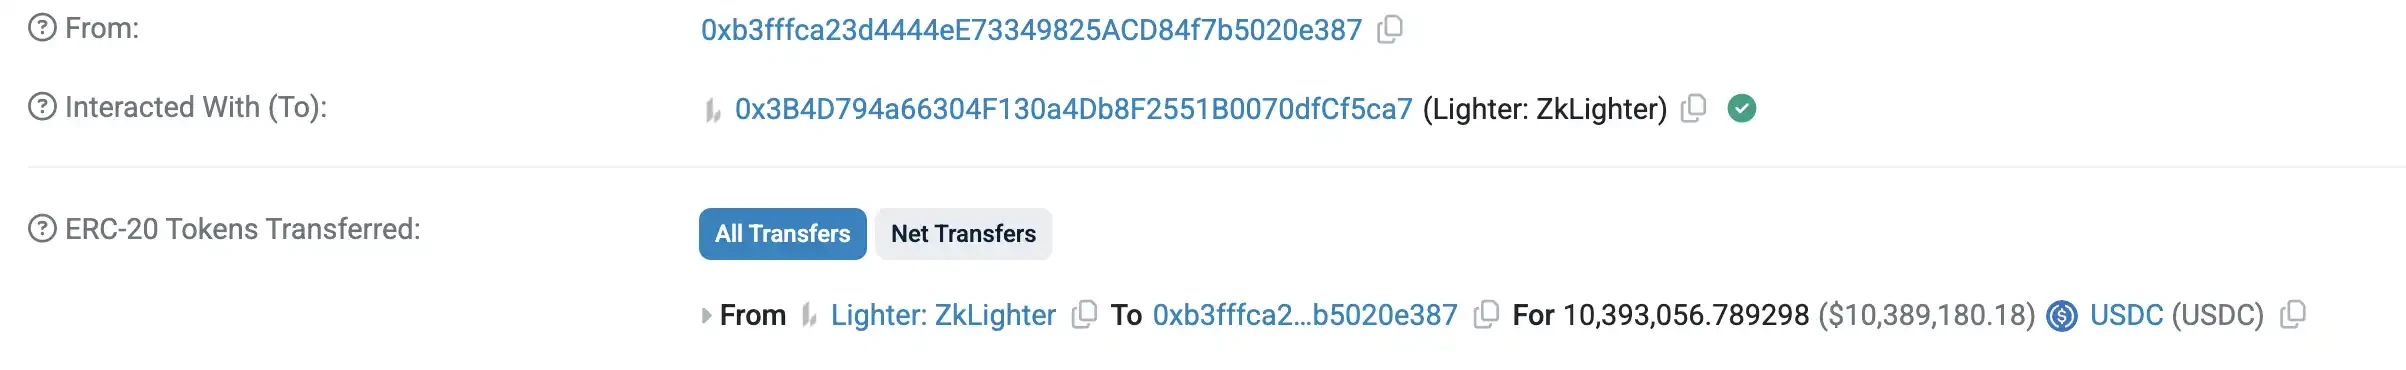
At 18:11:47, the first withdrawal was completed. The Ethereum transaction receipt shows that the Lighter mainnet contract paid 10,393,056.789298 USDC to the attacking address.
After getting the money, the attacker deposited 10,200 USDC into Lighter again and applied the same method to a second victim account, 714723.
At 18:25, the second public pool was created. The victim account put in 1 USDC, the attacker put in 9,999 USDC, and then another 1 USDC internal transfer and redemption test was performed. At 18:27, five transfers of 1 million USDC each and one remainder entered the pool, and the attacker redeemed again. At 18:28:45, a second withdrawal request of about 5.097 million USDC was submitted.
At 18:29, MLM detected this outflow of funds in a Telegram channel.
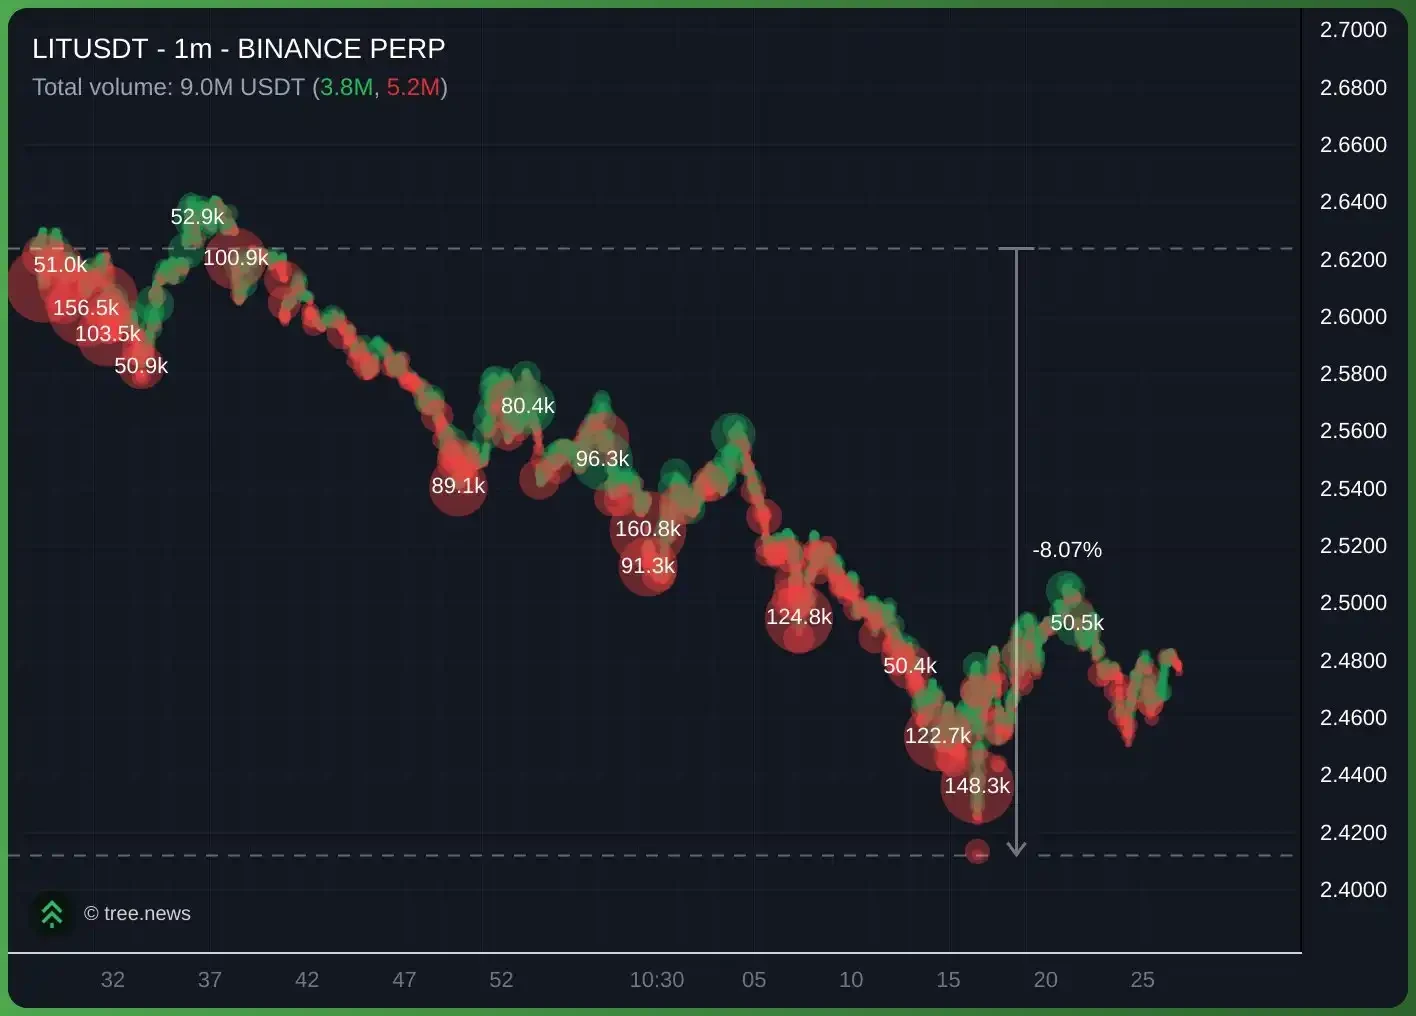
Binance's minute-by-minute market data recorded the sell-off that followed immediately. The LITUSDT perpetual contract opened at $2.725 at 18:29, touched a low of $2.3218 by 18:34, a drawdown of about 14.8% within a few minutes.
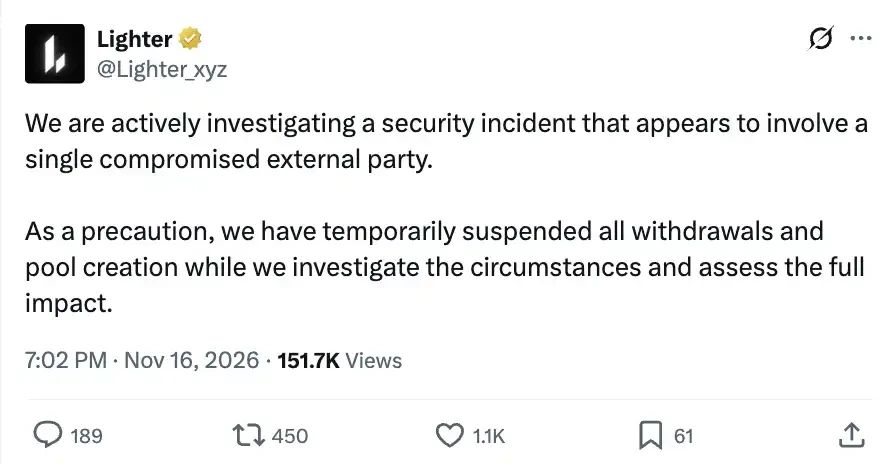
At 19:02, Lighter announced an investigation into the security incident, stating that it appeared to involve a single external entity, and precautionarily suspended all withdrawals and public pool creation.
Funds Entered Hyperliquid via Arbitrum
After the first withdrawal arrived, the attacker sold about 10.383 million USDC through six transactions, obtaining a total of 5,764.47 ETH-equivalent assets.
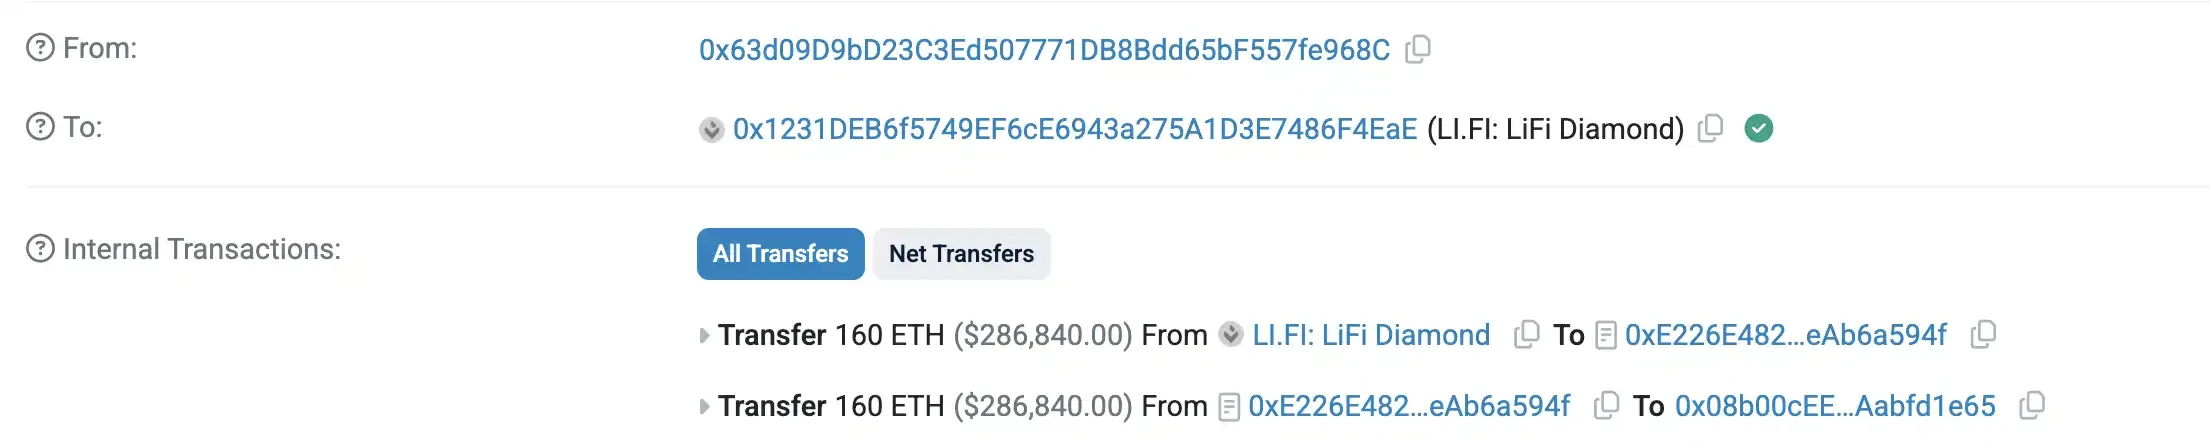
Next, the funds began to be split into tranches of 160 ETH each.
Take the sub-address starting with 0x63d09 as an example. At 18:19:59, it received 160 ETH from the main address. In less than two minutes, this sub-address called LiFi and executed a cross-chain transfer via LayerSwap.
At 18:37, the same address on Arbitrum received 287,557.5548 USDC; at 18:39, it transferred the exact same amount into the Hyperliquid deposit bridge.
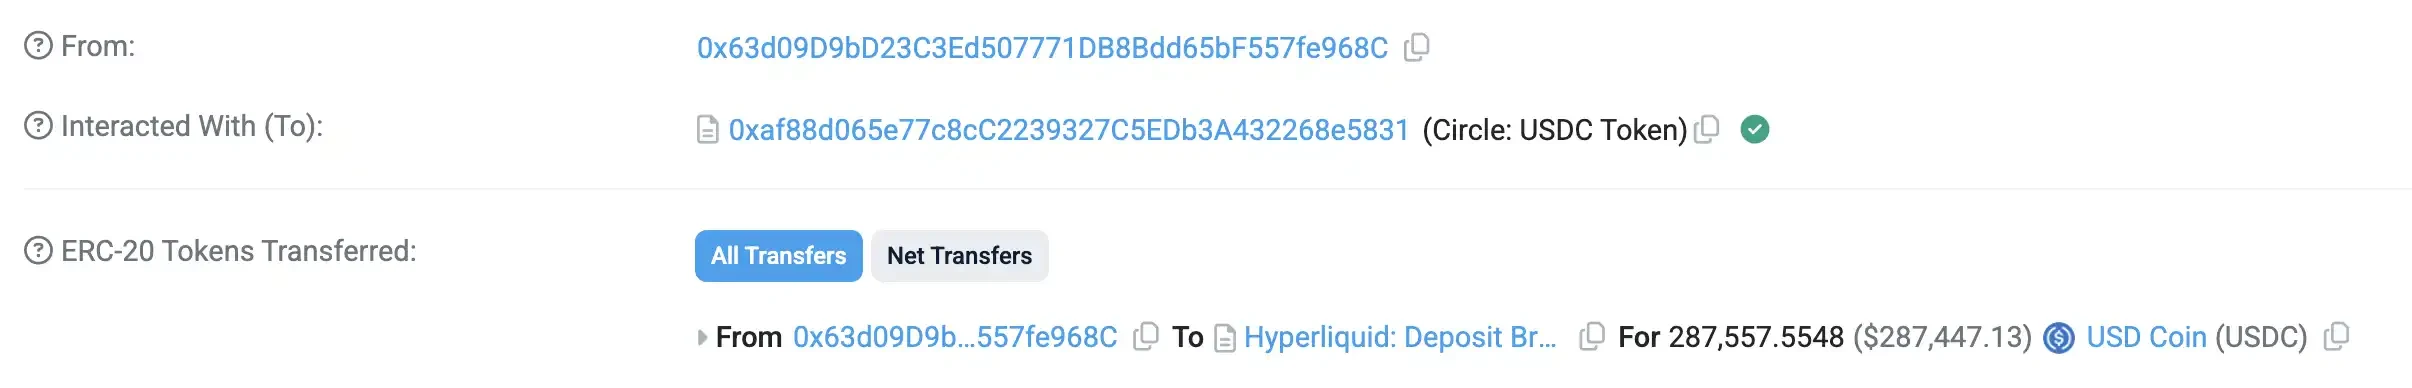
After the funds entered the Hyperliquid spot account, the hacker continuously bought 552 XMR1 (Monero).
The hacker's other sub-addresses also repeated this route. After ETH was bridged from Ethereum, USDC was received on Arbitrum, and then the funds entered Hyperliquid to buy the spot token XMR1.
The Victim Account
Now let's look at the victim.
The Ethereum address corresponding to Lighter account 714710 is a wallet starting and ending with 0x0d1D. On February 16, a Hyperliquid wallet 0xb83de, previously labeled as Abraxas, had transferred 0.1 ETH to it on Arbitrum to top up gas fees for this address.
This record supports the judgment that the compromised Lighter account is related to Abraxas Capital.
According to our previous institutional profile, Abraxas Capital was founded in London in 2002 by Fabio Frontini and Luca Celati, both from traditional banking backgrounds. It initially engaged in global macro trading and shifted to digital assets in 2017. The Elysium Global Arbitrage Fund, launched in 2018, started with Bitcoin cross-market arbitrage and later expanded to stablecoin arbitrage. On-chain data shows that the institution's assets under management have consistently exceeded $1 billion.
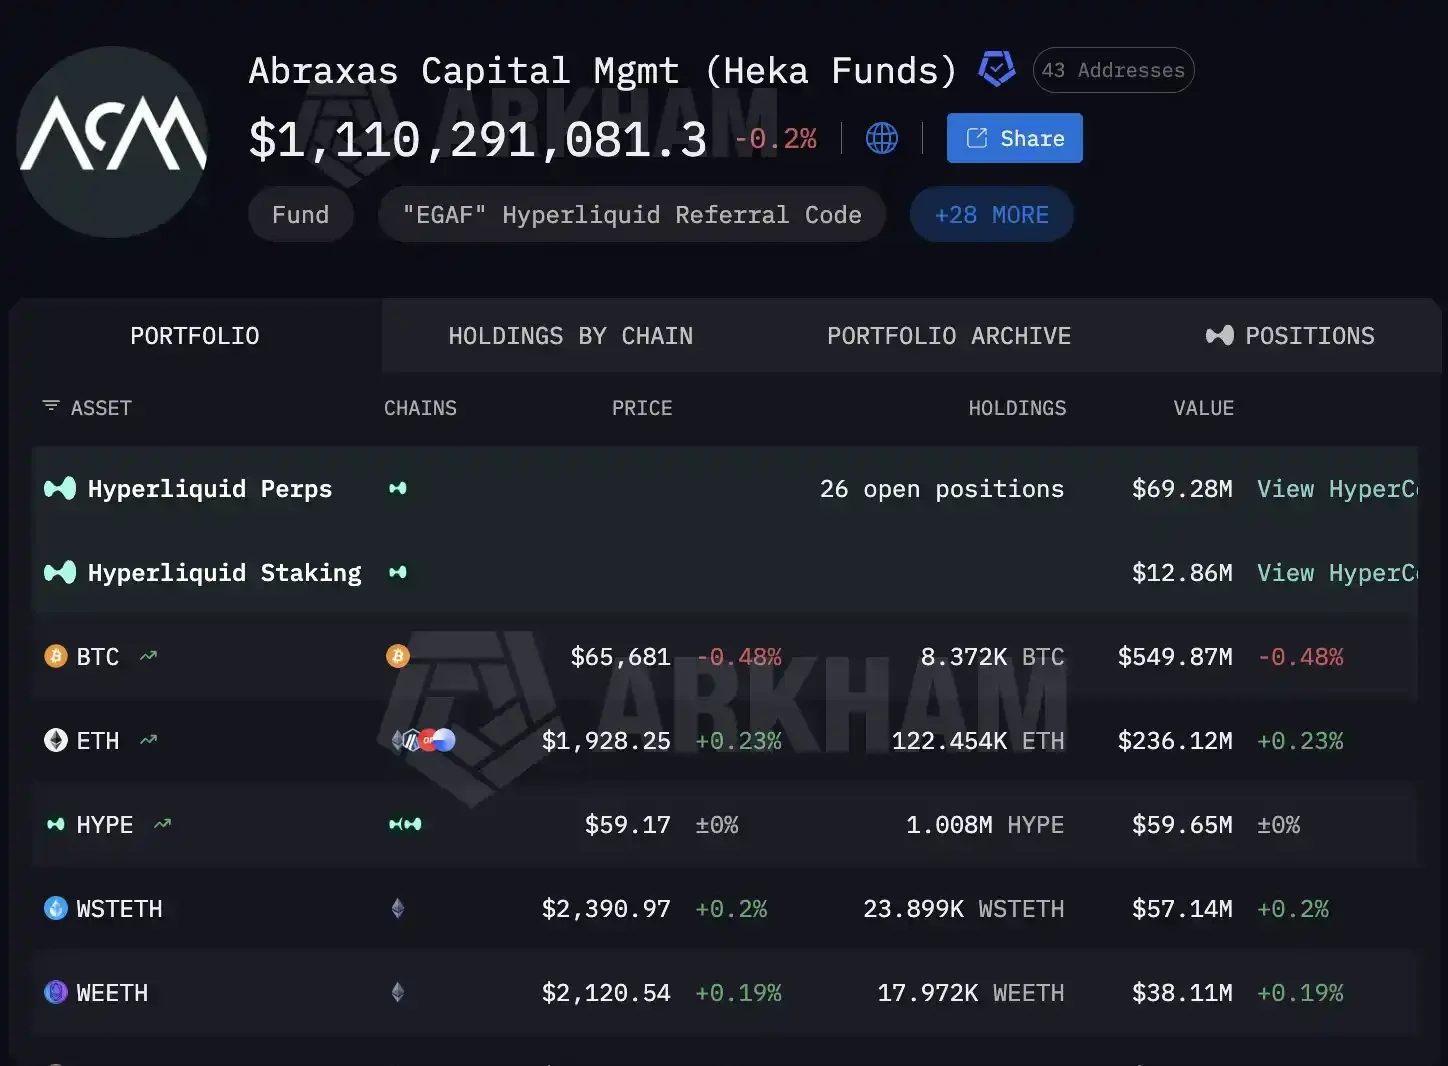
For institutions that rely on programmatic trading, cross-platform position adjustments, and capital turnover, storing API keys is part of daily operations. Yet even the most careful can slip up, and the leaked API was exploited by the hacker.
The shock of Binance's hack in late October had not yet passed, and Lighter then suspended withdrawals due to this security incident.
It is foreseeable that as AI continues to develop, more funds will be deterred by frequent security incidents or even withdraw and exit outright. The threat of hackers will remain a long-term cloud hanging over the crypto industry.





