






The whole network is closing in: Which dirty funds have been frozen in the Binance hack?


- Core Viewpoint: Binance's hot wallet suffered the largest security breach in history, with nearly $6.3 billion flowing out across multiple chains. Industry-wide on-chain interception has frozen approximately $3 billion, with stablecoin issuers becoming the main force in interception through blacklist authority.
- Key Elements:
- The attack spanned Ethereum, Bitcoin, Tron, and multiple L2 networks. Binance's hot wallets were simultaneously compromised, with cumulative outflows approaching $6.3 billion.
- Tether froze approximately 1.768 billion USDT and assets including XAUT and USDT0, while Circle fully froze 823 million USDC. Together, the two locked up nearly $2.6 billion.
- Emerging stablecoin issuers including Ripple, World Liberty Financial, Paxos, and StraitsX coordinated to freeze assets such as RLUSD, USD1, USDP, PAXG, and XUSD.
- Binance froze approximately 29,900 WBETH (worth nearly $80 million to $100 million) through its proprietary contract authority, preventing the hacker from unstaking or selling.
- The Arbitrum Security Council urgently transferred 74.56 million ARB and 8,425 ETH to an intermediary frozen wallet, which requires governance voting before the funds can be moved.
- The remaining tracking focus has shifted to native assets that cannot be frozen through contracts: approximately 195,000 ETH (some already deposited into Aave) and 18,270 BTC.
Original | Odaily (@OdailyChina)
Author | Azuma (@azuma_eth)
In the early hours of this morning, Binance's hot wallets suffered the largest security breach in cryptocurrency history. Within less than an hour, Binance hot wallets across Ethereum, Bitcoin, Tron, as well as Arbitrum, Avalanche, Optimism, Base, and multiple other networks were simultaneously compromised, with cumulative outflows approaching $6.3 billion (confirmed by Binance's latest announcement).
Following the attack, major stablecoin issuers, RWA asset issuers, and public chain protocols launched the largest joint on-chain interception operation in crypto history.
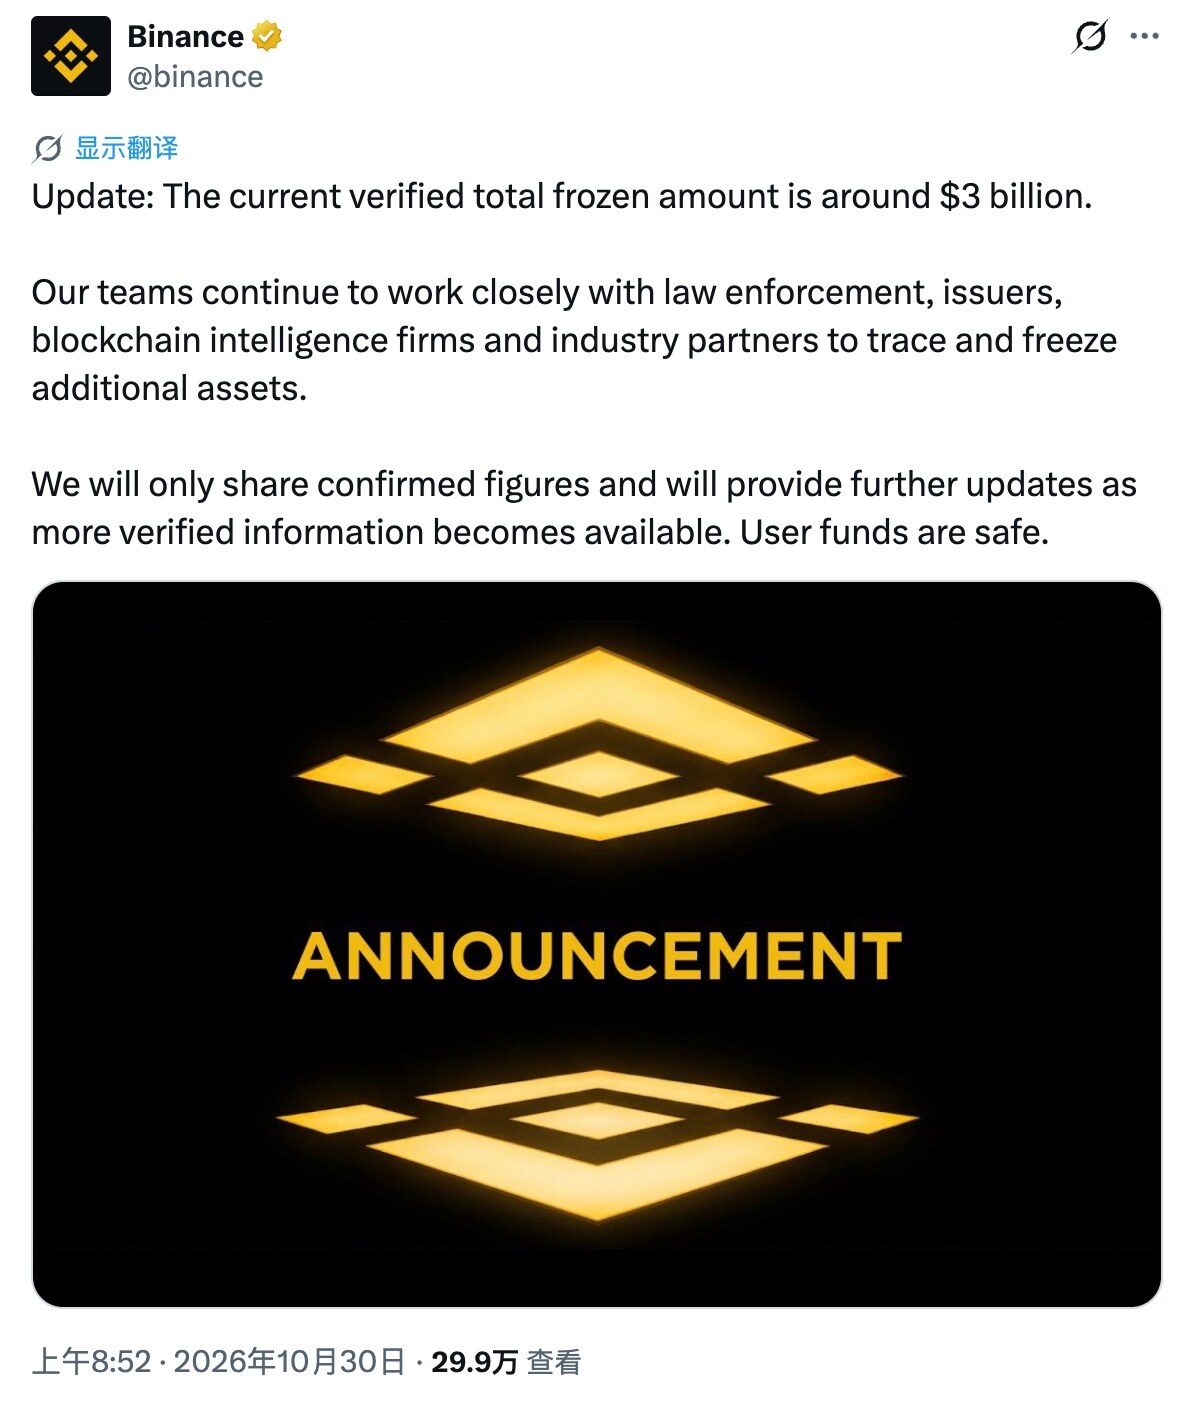
As of 8:52 AM Beijing time, Binance officially updated its incident response progress, stating that approximately $3 billion in stolen assets have been confirmed frozen. Binance also stated that the team continues to work closely with law enforcement agencies, asset issuers, blockchain intelligence firms, and industry partners to trace and freeze additional assets, and will only publish verified data going forward.
Combining the community's latest on-chain tracking dashboard data (source: ZachXBT) with timeline records, we have compiled the 11 types of assets confirmed frozen by various institutions/protocols as of publication.
Freezing Actions Breakdown: Who Is Taking Action? How Was Interception Achieved?
This on-chain interception of up to $3 billion relies primarily on the built-in blacklist or freeze administrator permissions of centralized stablecoins and yield-bearing asset smart contracts, and can be divided into the following four categories.

Stablecoin Duo: Tether and Circle Lock Down Nearly $2.6 Billion
- Tether (froze over $1.809 billion)
On-chain records show that just 41 minutes after Binance 14 was first swept at 4:24 AM Beijing time, Tether was the first to call the blacklist function on-chain at 5:05, initially locking 971 million USDT, and expanding the freeze to 1.567 billion USDT by 5:11.
Subsequently at 5:25, Tether CEO Paolo Ardoino officially posted on X confirming the freeze of over 1.567 billion USDT related to the Binance incident.With the subsequent blacklisting of additional associated addresses, on-chain statistics currently show a total of 1,767,593,979.80 USDT completely locked down.
At the same time, Tether also blacklisted 12,574.05 XAUT (gold tokens, approximately $35 million) that the hacker had opportunistically swept, along with 6,185,900.10 cross-chain stablecoin USDT0.
- Circle (froze $823 million)
After Binance 34 saw outflows totaling 823 million USDC at 4:41 and 4:59, Circle completed the on-chain address blacklisting by 5:13. Subsequently at 5:28, Circle CEO Jeremy Allaire officially posted on X confirming that over 800 million USDC had been frozen in coordination with law enforcement.
According to the latest on-chain statistics, the stolen 823,000,000 USDC has been fully frozen in the hacker's addresses.
Emerging Stablecoin Issuers: Ripple, WLFI, Paxos, and StraitsX Join Forces
Beyond the two largest stablecoin giants, several emerging stablecoin issuers also participated in encircling the hacker.
- Ripple: Has frozen 40,541,065 RLUSD (approximately $40.54 million) in the hacker's addresses;
- World Liberty Financial: Froze 27,824,039.94 USD1 (approximately $27.82 million) and 48 million WLFI tokens (approximately $2 million);
- Paxos: Simultaneously froze 215,657.65 USDP (approximately $215,000) and 1,906.67 PAXG gold tokens (approximately $5.3 million) issued under its umbrella;
- StraitsX: Singapore-compliant stablecoin issuer StraitsX froze 819,820.54 XUSD (approximately $820,000).
Binance's Proprietary Wrapped Assets: Nearly 30,000 WBETH Locked in Place
Among non-stablecoin assets, the hacker swept 29,934.01 WBETH (Wrapped Beacon ETH, valued at nearly $80 million to $100 million) from Binance 14.
Since WBETH is itself a liquid staking wrapped token issued by Binance, its underlying smart contract has administrator restriction permissions. Binance's security team immediately froze this batch of WBETH through internal permissions after the incident, and the hacker can no longer unstake or sell it.
Public Chain Ecosystem Containment: 74.56 Million ARB Restricted from Moving
In addition to the assets directly frozen through token contract blacklists mentioned above, several public chain (L1 & L2) ecosystems have also actively taken emergency measures for containment.
At 8:19 AM Beijing time this morning, the Arbitrum Security Council officially announced that it had taken emergency action to move 74,559,805 ARB and 8,425 ETH held in addresses identified as related to the Binance theft incident to an intermediary frozen wallet. The addresses that originally held these funds can no longer access them, and they can only be moved through further action by the Security Council or an Arbitrum DAO governance vote, with related matters to be coordinated with all parties.
Follow-up Tracking Focus
With approximately $3 billion in stolen funds frozen, the vast majority of stablecoin assets in the hacker's hands have been brought under control.
Currently, the core focus of on-chain tracking and offense-defense has fully shifted to native crypto assets that cannot be directly frozen through contracts — primarily approximately 195,000 ETH still circulating or dormant on-chain (some of which has been deposited into Aave by the hacker to borrow WETH in an attempt to launder it) and 18,270 BTC on the Bitcoin network.
Odaily will continue to track and report on on-chain anomalies and judicial recovery progress regarding the remaining unfrozen funds. The whole network is closing in — which dirty funds have been frozen in the Binance theft incident?





