JulSwap flash loan attack analysis and incident follow-up


secondary title
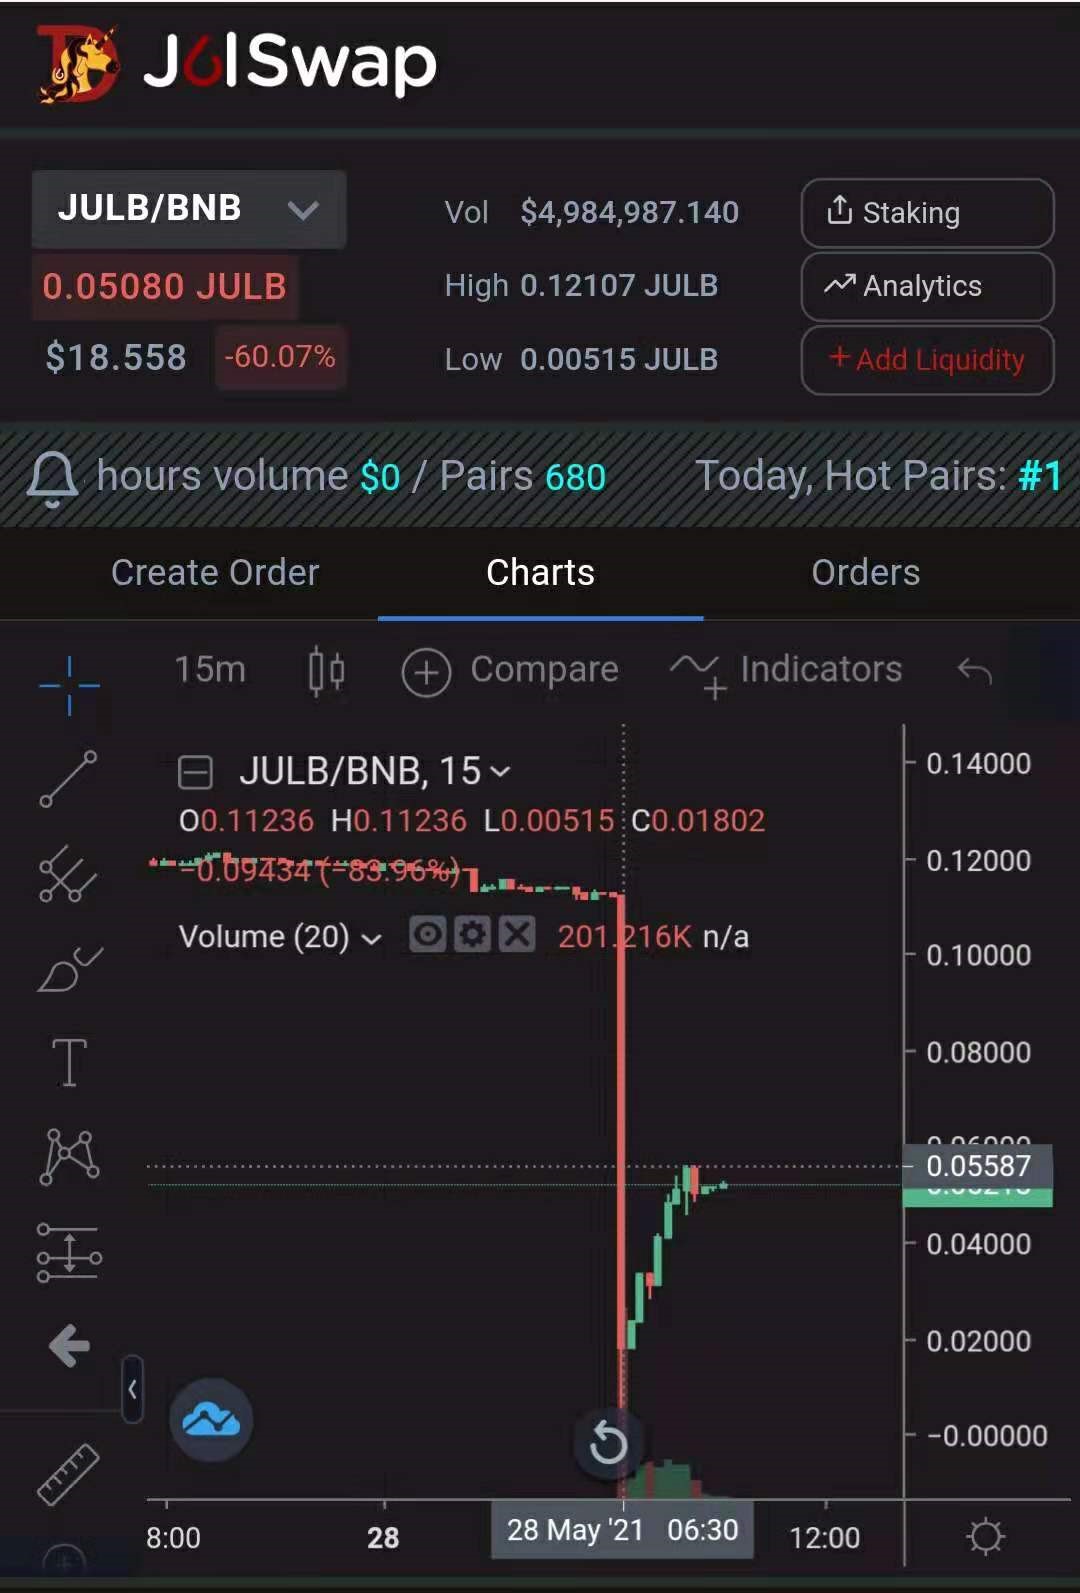
On May 28, 2021, it was reported that JulSwap, the DEX protocol on the BSC chain and the automated liquidity protocol, was attacked by flash loans.Know Chuangyu Blockchain Security Labsecondary title
event analysis
Attacker transaction:
https://bscscan.com/tx/0x1751268e620767ff117c5c280e9214389b7c1961c42e77fc704fd88e22f4f77aAttack contract address:0x7c591aab9429af81287951872595a17d5837ce03
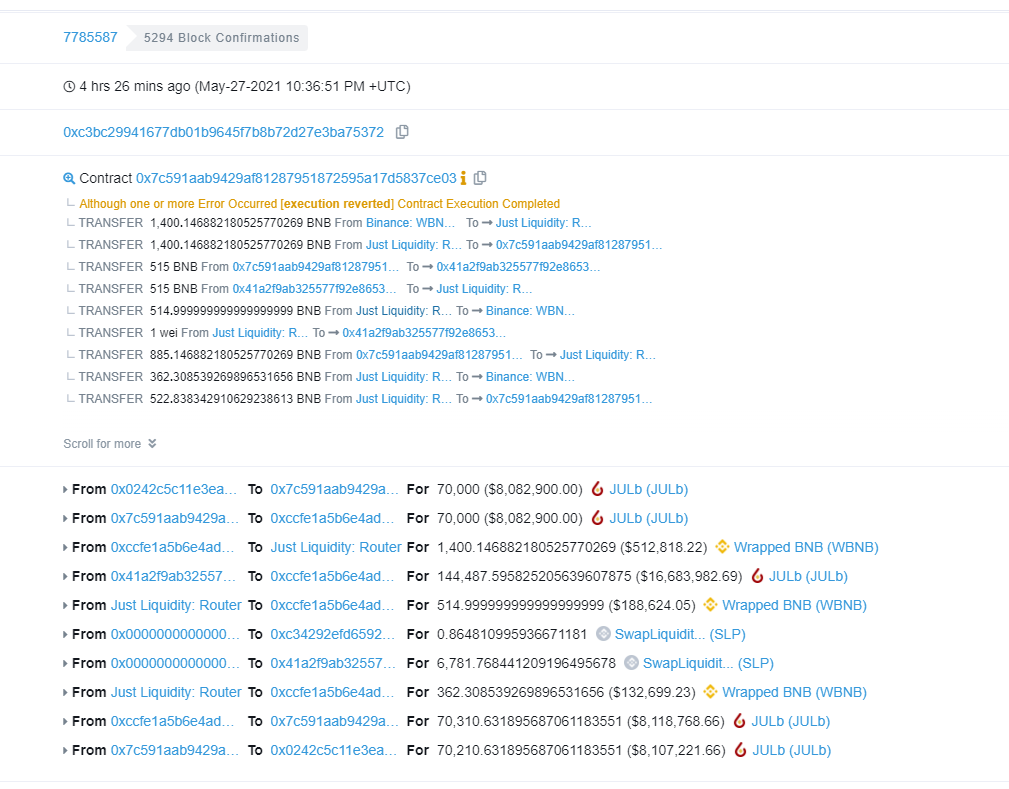
1. Through the transaction records, it can be seen that the attacker borrowed 70,000 JULB tokens through flash loan, and then called the JULB-WBNB transaction pair to exchange to get 1,400 BNB. At this time, there are 1,400 WBNB in the attack contract.
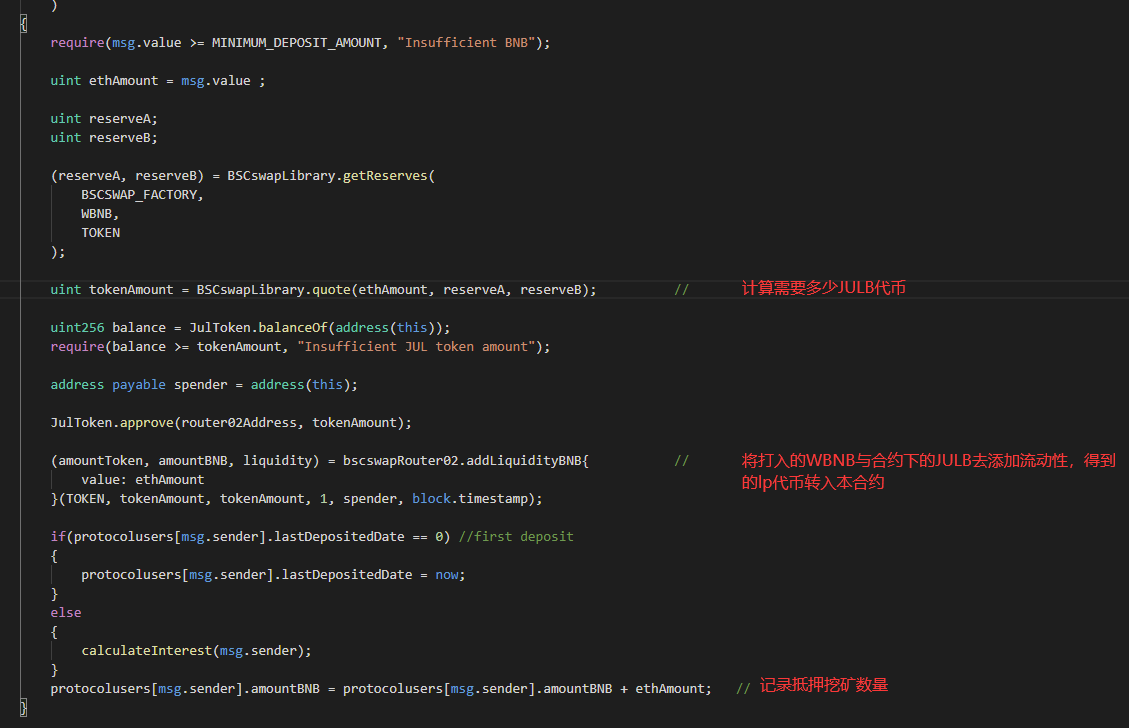
2. Then the attack contract calls the addBNB function of the JulProtocolV2 contract (0x41a2F9AB325577f92e8653853c12823b35fb35c4) for mortgage mining. The function of this function is that by transferring WBNB, the contract will calculate how many JULB tokens are needed to add liquidity mining, and then record the amount of transferred WBNB for mortgage mining. The function code is as follows.
4. The attacker then uses the remaining WBNB to exchange for JULB. Since a large amount of JULB token liquidity is added to the pair, only 363 WBNB are needed to exchange for 70,000 JULB tokens for loan repayment. , there are 885-363=522 WBNB left in the contract, and finally transfer these WBNB to the wallet address, and the attacker completes a flash loan arbitrage.secondary title
Event follow-up