On March 14, Beijing time, a new type of attack occurred on True Seigniorage Dollar, with a total loss of about 16,600 US dollars. CertiK will take you to analyze this attack.
On March 14, Beijing time, the CertiK security technology team discovered a new type of attack on the DeFi stablecoin project True Seigniorage Dollar, with a total loss of about 16,600 US dollars.loophole"loophole"secondary titletechnical analysis
The whole attack process is as follows:
Figure 1: The target (malicious) token implementation contract and proposer information of Proposal 2 of the TSD project
② In Proposal No. 2, the attacker proposed and passed the actual TSD token contract address pointed to by the proxy contract at the address 0xfc022cda7250240916abaa935a4c589a1f150fdd, and changed it to the malicious token deployed by the attacker through another address 0x2637d9055299651de5b705288e3525918a73567f contract.image description
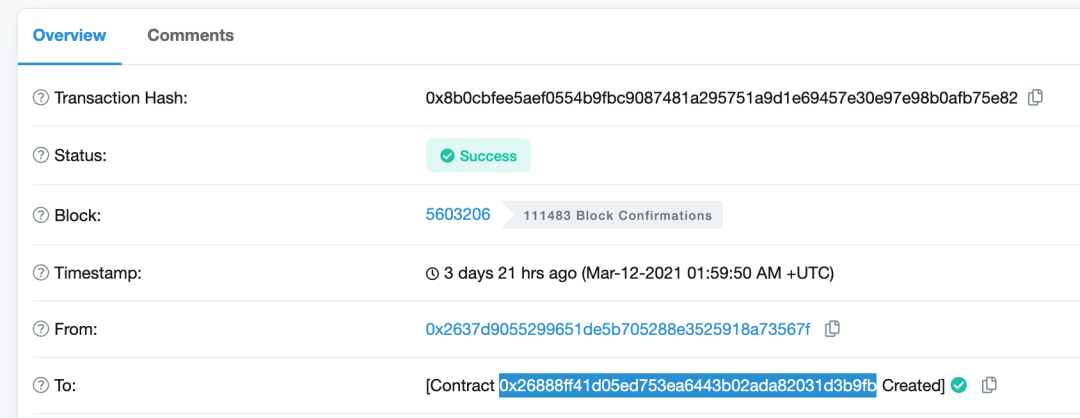
Figure 3: The attacker uses one of the addresses held to create a malicious token to implement the contract
Figure 4: The attacker used one of the addresses held to determine Proposition 2 and minted a huge amount of TSD tokens to the other address held
④ At the same time, the initialize() method in the malicious contract located at the address 0x26888ff41d05ed753ea6443b02ada82031d3b9fb will also be called during the upgrade process.image description
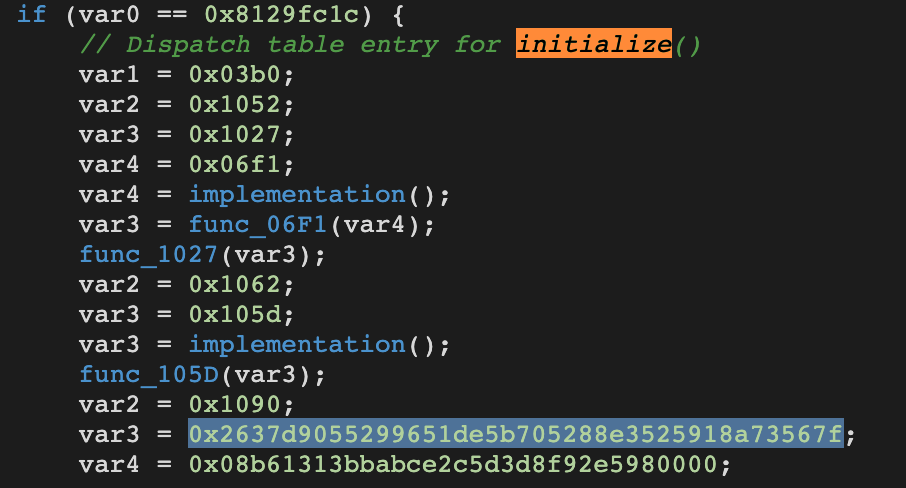
Figure 6: Decompile malicious tokens to implement the initialize() method in the contract to mint tokens to the attacker's address
Summarize
Summarize
The attack did not take advantage of any vulnerabilities in the TSD project smart contracts or Dapps.Based on the understanding of the DAO mechanism, the attacker continues to purchase TSD at low prices, and uses the mechanism that project investors can no longer vote on proposals after they unbond their tokens because they are no longer able to profit from the project , and considering that the project party has a very low proportion of voting rights, so with an absolute advantage"kidnap"The governance result of Proposal 2 is guaranteed, thereby ensuring that the malicious proposal is passed.Although the entire attack was finally completed with a malicious contract implanted with a backdoor, the DAO mechanism was the main reason for the completion of the attack during the entire implementation process.The CertiK Security Technology Team recommends:Starting from the DAO mechanism, the project party should have the ability to ensure that the proposal governance will not be"kidnap"voting rights to prevent this attack from happening again.





