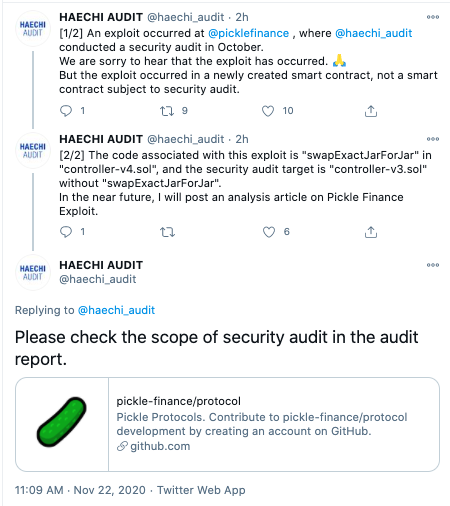
Odaily Frontline|DeFi protocol Pickle Finance lost nearly 20 million US dollars due to a loophole


This article comes fromThe Block、Cointelegraph
Odaily Translator |
 according toThe BlockThis article comes from
Odaily Translator |
according to0x70178102AA04C5f0E54315aA958601eC9B7a4E08。
DeFi protocol Pickle Finance lost nearly $20 million in DAI in a bug on Saturday, according to reports.It is reported that the vulnerability exploit involves Pickle Finance's DAI pJar strategy, which uses the Compound protocol to obtain income through DAI deposits.Funds from the exploit have been transferred to addresses, white hat hacker and co-founder of DeFi Italy, regarding Pickle Finance’s loss of nearly $20 million due to a bug
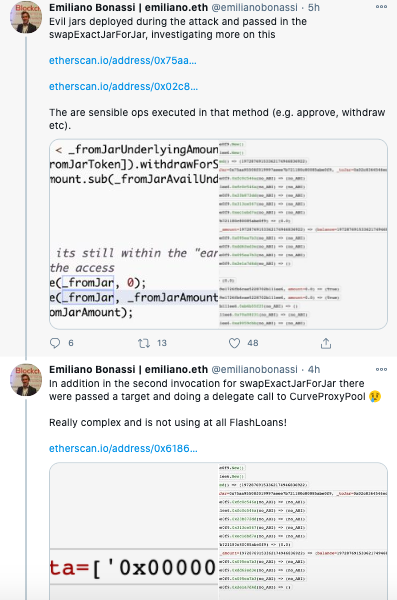
Emiliano Bonassi says
, the attacker deployed an "Evil Jar", a smart contract that has the same interface as a traditional Jar, but does evil. The attacker then swapped funds between his "evil Jar" and the real cDAI Jar, stealing $20 million worth of deposits.secondary title:
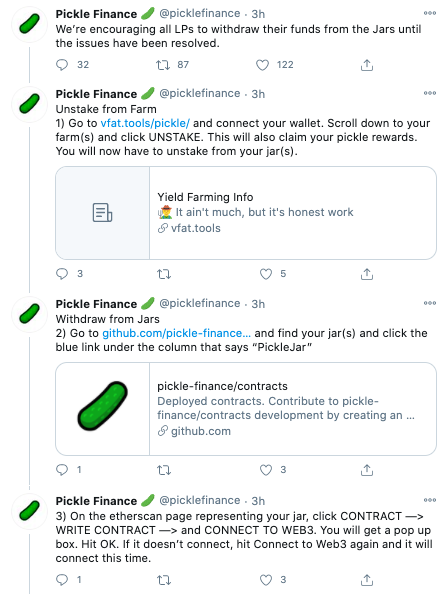
Official Response: LPs are encouraged to withdraw funds from Jar until issue is resolved
On November 22, Pickle Finance tweeted that there were reports that our DAI PickleJar strategy had been exploited. We are actively investigating this matter and will provide further updates. We encourage all LPs to withdraw funds from the Jar until the issue is resolved.https://vfat.tools/pickle/The specific operation is as follows
1) Release from the farm:
accesshttps://github.com/pickle-finance/contracts#pickle-jars-pjars, connect your wallet. Scroll down to find your farm and click UNSTAKE. This will also claim your Pickle rewards. You must now unzip from your Jar.
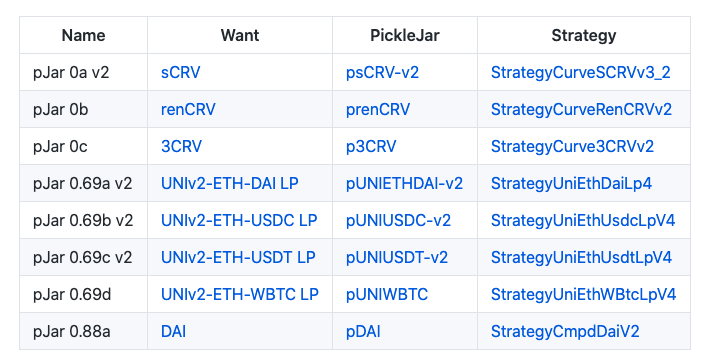
2) Withdrawal from Jar:
access
3) On the Etherscan page representing Jar, click CONTRACT -> WRITE CONTRACT -> CONNECT TO WEB3 (connect to WEB3). You'll see a popup. Click "OK". If it cannot connect, click "CONNECT TO WEB3" again and it will connect.
4) Enter Option 15 and click the blue button "WRITE". Then complete your Metamask transaction as usual (with fast gas).
5) Repeat this process for all Jars that need to withdraw funds.
secondary title
follow-up update
On the afternoon of the 22nd, the SlowMist security team stated that they followed up and analyzed the relevant incidents as soon as possible. The following is a brief analysis process:
1. The swapExactJarForJar function in the project’s Controller contract allows passing in two arbitrary Jar contract addresses for token exchange. Among them, _fromJar, _toJar, _fromJarAmount, and _toJarMinAmount are all variables that users can control. Attackers use this feature to Fill in _fromJar and _toJar with your own address, _fromJarAmount is the amount of DAI set by the attacker to extract the contract, about 20 million DAI.
2. During the exchange process using the swapExactJarForJar function, the contract will obtain the corresponding token through the incoming _fromJar contract and _toJar contract's token() function, which is used to specify the exchanged asset. Since the _fromJar contract and _toJar contract are both passed in by the attacker, the value obtained by using the token() function is also controllable. Here, the token obtained from the _fromJar contract and _toJar contract is DAI.
3. At this time, the exchange occurs, and the Controller contract uses the transferFrom function to transfer a certain amount of ptoken from the _fromJar contract. However, since the fromJar contract is an address controlled by the attacker, the ptoken transferred here is the attacker's counterfeit currency. At the same time, because the token obtained by the contract from the _fromJar contract is DAI, then the contract will judge whether the funds in the contract are sufficient for exchange. If not, it will redeem a certain amount of tokens from the strategy pool and transfer them to the Controller contract . In this attack, the DAI in the contract is not enough for exchange. At this time, the contract will withdraw the insufficient share from the strategy pool to make up the 20 million DAI set by the attacker.4. The exchange continues. After the Controller contract proposes DAI from the policy pool to make up the 20 million DAI set by the attacker, it will call the withdraw function of _fromJar to burn the fake ptoken transferred by the attacker in the third step, and then The contract judges the balance of the token specified by the _toJar contract in the current contract. Since the token specified by the _toJar contract is DAI, the Controller contract will judge the remaining amount of DAI in the contract. At this time, due to the third step, the Controller contract has collected 20 million DAI, so the balance of DAI is 20 million. At this time, the Controller contract calls the deposit function of the _toJar contract to transfer 20 million DAI to the _toJar contract controlled by the attacker. At this point, the attacker has completed the profit.,Summary: In this attack, the attacker forges the contract addresses of _fromJar and _toJar when calling the swapExactJarForJar function in the Controller contract, and completes the attack process by transferring the counterfeit currency in exchange for the real DAI in the contract.In addition, for the Pickle Finance attack,