OKLink: Inventory of security incidents in April 2023


first level title1. Basic
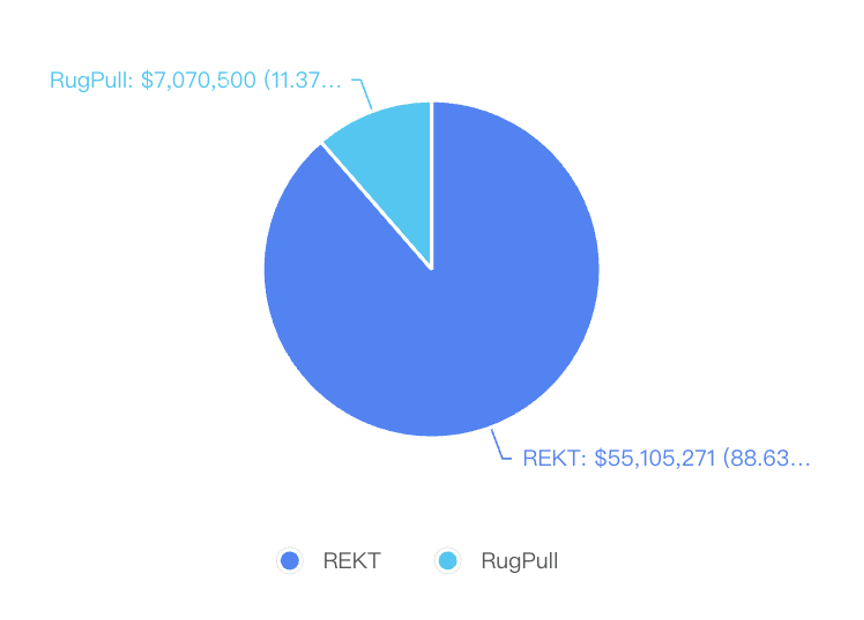
In April 2023, the security incidents caused a total loss of about 60 million US dollars. Compared with the previous month, the amount of losses has decreased, but the number of security incidents remains unchanged. Among them, Yearn Finance caused a loss of more than 10 million US dollars due to parameter configuration errors. At the same time, there are some vulnerabilities that have already appeared, and they also appear on the Arbitrum chain. In addition, the number of RugPull remains unabated. Incidents such as social media fraud are still frequent, and Twitter project party account forgery and official Discord are attacked and released phishing links emerge in endlessly.
secondary title
No.1
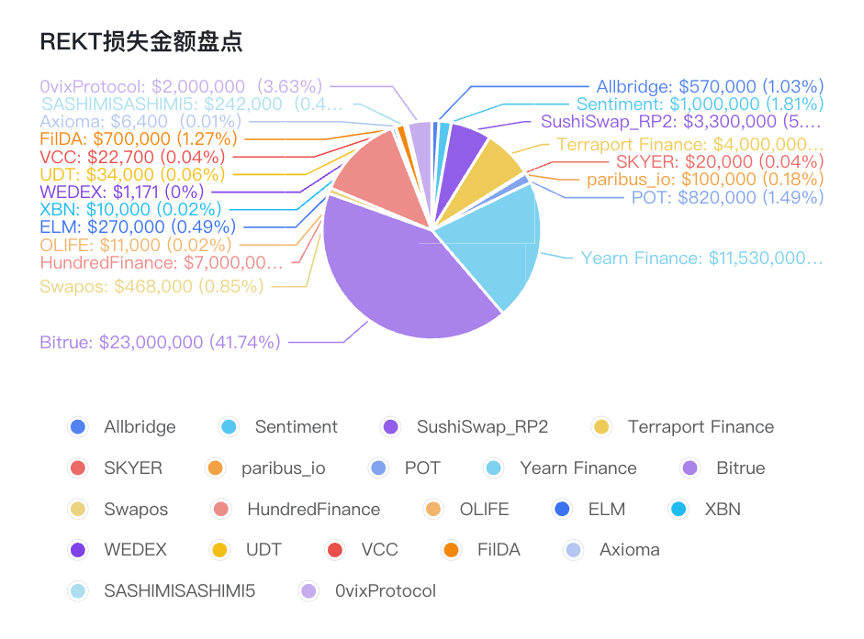
1.1 REKT Inventory
On April 2, the Allbridge_io project was attacked by a flash loan and lost about 570,000 US dollars. The main reason was that the price of the pool 0x 179 a was manipulated through the flash loan to make a profit. The attacker first deposits 0x 179 a 500 m BUSD through flash loan, and then converts bsc_usd into busd by calling swap. At the same time, withdraws cash from the 0x 179 a pool, and finally empties the busd of the pool, and then calls swap , convert busd into bsc_usd, because the pool was destroyed, and finally convert 4 w busds into 78 w bsc_usd.
•https://www.oklink.com/cn/bsc/tx/0x 7 ff 1364 c 3 b 3 b 296 b 411965339 ed 956 da 5 d 17058 f 3164425 ce 800 d 64 f 1 aef 8210
Attack transactions:
•https://www.oklink.com/cn/bsc/address/0x c 578 d 755 c d5 6255 d 3 ff 6 e 92 e 1 b 6371 ba 945 e 3984
No.2
Attacker address:
On April 5th, the Sentiment protocol was attacked by flash loans and lost about US$100,000. The core reason was a price error caused by a re-entry. The attacker first executes the joinPool of Balancer Valut to pledge, and then calls exitPool to withdraw coins. In exitPool, the remaining ETH will be transferred to the attack contract. At this time, the fallback function of the attack contract will be called. If the borrow operation is performed, the entire supply will be reduced, which will affect the price.
•https://www.oklink.com/cn/arbitrum/tx/0x a 9 ff 2b 587 e 2741575 daf 893864710 a 5 cbb 44 bb 64 ccdc 487 a 100 fa 20741 e 0 f 74 d
Attack transactions:
•https://www.oklink.com/cn/arbitrum/address/0x dd 0 cdb 4 c 3 b 887 bc 533957 bc 32463977 e 432 e 49 c 3
No.3
Attacker address:
On April 9th, RouteProcessor 2 in SushiSwap was attacked, and the loss was about 330w. The core reason was that RouteProcessor did not verify the route parameters provided by the user, which led the attacker to specify a malicious pool, and then implemented swap in the malicious pool Interface, and use the uniswap V3 SwapCallback callback function to steal coins from authorized users of RouteProcessor 2.
•https://www.oklink.com/cn/eth/tx/0x ea 3480 f 1 f 1 d 1 f 0 b 32283 f 8 f 28 2c e 16403 fe 22 ede 35 c 0 b 71 a 732193 e 56 c 5 c 45 e 8
No.4
Attack transactions:
No.5
On April 10, Terraport Finance was attacked and lost about US$400w.
On April 10, Meta Skyer (SKYER) was attacked by flash loan and lost 2w USD
•https://www.oklink.com/cn/bsc/tx/0x ee 1 bc 3d 0 b 5 b 9 bbbe 3 fa 47730774 a 391491 f 583 a 602 afb 0969 f 53 2d 521975137 d
No.6
Attack transactions:@paribus_ioApril 11,
The project was attacked and lost about US$100,000. The core reason was a reentrancy vulnerability in an old version of Compound V2.
No.7
Attack transaction: https://www.oklink.com/cn/arbitrum/tx/0x 0 e 29 dcf 4 e 9 b 211 a 811 caf 00 fc 8294024867 bffe 4 ab 2819 cc 1625 d 2 e 9 d 62390 af
On April 12, MetaPoint ($POT) was attacked and lost about US$82w. The core reason is that every time deposit $POT, a new contract will be created to store user assets, but the approve function in this contract It is public, allowing anyone to transfer their assets.
No.8
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x ccd 12 f 22629 b2c 4 2d 2 b 68036 2d adbd 1 b 3d 89 cb 4 a 87 a 8 c 9 b 297766 b 4974 c 6 ad 34
On April 13, Yearn Finance was attacked and lost a total of about US$1153w. The core reason was that the yUSDT contract was misconfigured, and it was configured as a USDC address.
•https://www.oklink.com/cn/eth/tx/0x 055 cec 4 fa 4614836 e 54 ea 2 e 5 cd 3d 14247 ff 3d 61 b 85 aa 2 a 41 f 8 cc 876 d 131 e 0328
•https://www.oklink.com/cn/eth/tx/0 x d5 5 e 43 c 160 2b 28 d 4 fd 4667 ee 445 d5 70 c 8 f 298 f 5401 cf 04 e 62 ec 329759 ecda 95 d
No.9
Related transactions:
On April 16, Swapos V2 Contracts was attacked, and a total loss of 46.8 w was lost. The core reason was that in the swap function of the Swapos contract, there was an error in the judgment of the k value, which allowed the attacker to withdraw the money in the pair.
•https://www.oklink.com/cn/eth/tx/0x 78 edc 292 af 51 a 93 f 89 ac 201 a 74 2b ce 9 fa 9 c 5 d 9 a 7007 f 034 aa 30535 e 3508 2d 50 a
Related transactions:
•https://www.oklink.com/cn/eth/address/0 x 2d f 07 c 054138 bf 29348 f 35 a 12 a 22550230 bd 1405
No.10
Attacker address:@HundredFinanceApril 15,
Being attacked, the loss of about 700 w US dollars, the core reason is that when hToken is redeemed, there is an integer rounding problem, which will appear when the market is empty. The attacker first deposits a small amount of WBTC to clear the hWBTC pool, and then donate a large amount of WBTC to the hWBTC pool, which will affect and increase the price of hWBTC, and then borrow all the assets in the market, and then call redeemUnderlying, due to the integer rounding problem, It will only burn half of the hWBTC in the contract to make a profit.
•https://www.oklink.com/cn/optimism/tx/0x 6 e 9 ebcdebbabda 04 fa 9 f 2 e 3 bc 21 ea 8 b 2 e 4 fb 4 bf 4 f 4670 cb 8483 e 2 f 0 b 2604 f 451
No.11
Related transactions:@OceanLifeTokenApril 19,
Attacked by flash loans, the profit was 32.29 WBNB, about 1.1 million US dollars. OLIFE is a reflection token. The attacker reduces the number of rSupply and tSupply by calling the transfer function and the deliver function multiple times, thereby affecting the number of OLIFE in the pool, and finally swapping OLIFE into WBNB for profit.
•https://www.oklink.com/cn/bsc/tx/0x a 21692 ffb 561767 a 74 a 4 cbd 1 b 78 ad 48151 d 710 efab 723 b 1 efa 5 f 1 e 0147 caab 0 a
No.12
Related transactions:$ELMOn April 20, the cross-chain bridge contract of Tales of Elleria on Arbitrum was attacked, and the attacker mint a total of 5,000,000,000
•https://www.oklink.com/cn/arbitrum/address/0x f 2c bf 39 e 7668 ebb 113 f 2c 609 bbd 6 ea 1 dfce 5 d 376
No.13
(about 27w USD) Related attackers:
On April 20th, XBN was attacked, and the attackers made a total profit of US$10,000.
•https://www.oklink.com/cn/bsc/tx/0x 3 b 698 ba 37 f 3 3ac 0 f 822 a 0 de 7 e 097126 d 71 e 8216 bf 59 ec 9 b 2 e 6044 df 7 d 4 f 40296
No.14
Related transactions:
On April 21, WEDEX Reward token (APP) encountered a flash loan attack, and the attacker made a profit of about 1171 US dollars.
•https://www.oklink.com/cn/bsc/tx/0x b 9217 a 608 da 161803977 dfcf 3 edfd 7 e 7323 bb 942 f 71 f 5 cae 6 da 5 e 1900 e 91174 d
No.15
Related transactions:
On April 21, the Unlock Discount Token $UDT was attacked, and the attacker made a profit of about US$3.4w.
•https://www.oklink.com/cn/eth/address/0x 43 ee 4169 d 9 ff 5 e 5 b 10 ca 42923 b 1 e 5 d 07 a 157 bb 71
No.16
Attacker address:
On April 22, Mutual Aid VCC was attacked. There is a backdoor function in this project, which can transfer VCC tokens to the specified address. The attacker earns 70 WBNB, about 2.27w USD.
•https://www.oklink.com/cn/bsc/tx/0x ef 1746520086 c 224 da 86 c 92 ee 9631366 ddf 883 e 4 ab 1 d 35 e 8958 c 095 f 5 eb 80 ebe
No.17
Related transactions:
No.18
On April 23, FilDA announced that it was attacked on the Elastos Smart Chain and REI network, and lost a total of 700,000 US dollars. The attacker converted 80 k $ELA into 326 BNB through cross-chain, and converted 200 k ELA into 17 ETH.
On April 24th, the Axioma project was attacked and finally made a profit of about 20 WBNB. The attacker first purchased AXT in the contract AxiomaPresale through the flash loan, and then exchanged the purchased AXT for WBNB through the pancake. Because the price of AXT in AxiomaPresale is calculated by a fixed formula, there is a price difference with the price in the pancake, which makes the attacker be able to profit from it.
•https://www.oklink.com/cn/bsc/tx/0x 05 eabbb 665 a 5 b 99490510 d 0 b 3 f 93565 f 394914294 ab 4 d 609895 e 525 b 43 ff 16 f 2
No.19
Related transactions:@SASHIMISASHIMI 5 April 25,
Attacked by flash loans, a total loss of 37.35 BNB & 6.58 ETH, totaling $24.2w.
No.20
Contract address: https://www.oklink.com/cn/bsc/address/0x c 28 e 27870558 cf 22 add 83540 d 2126 da 2 e 4 b 464 c 2@ 0 vixProtocolApril 28,
Attack transactions:
•https://www.oklink.com/cn/polygon/tx/0x 10 f 2c 28 f 5 d 6 cd 8 d 7 b 56210 b 4 d5 e 0 cece 27 e 45 a 30808 cd 3d 3443 c 05 d 4275 bb 008
secondary title
No.1
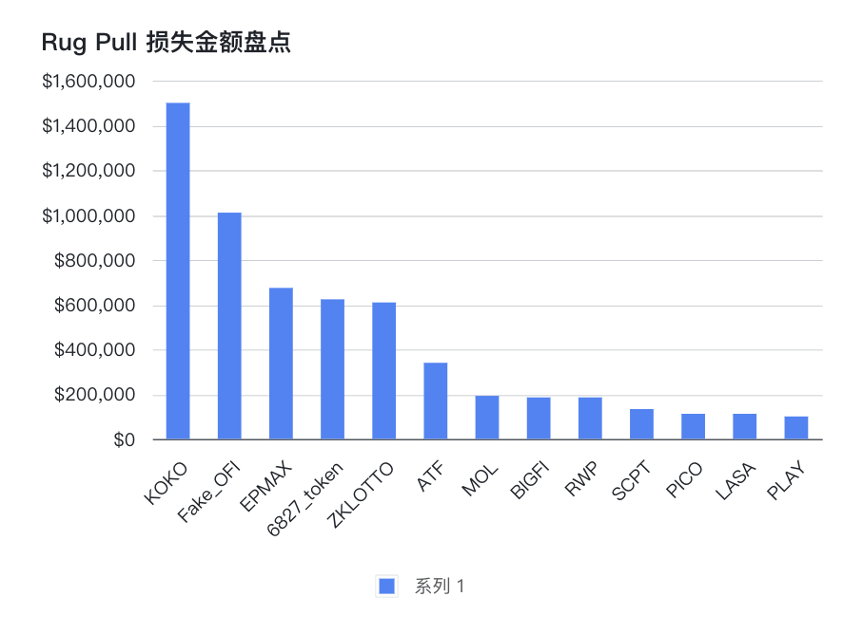
1.2 RugPull Inventory@Chain_Relay_April 1,
The (CRLN) project is suspected to be RugPull, the price fell by 97.7%, and about $1.32w was taken away by two different EOAs.
No.2
Contract address: https://www.oklink.com/cn/bsc/address/0x 5838 b 43 ede 809 dd 39 e 547 ba 09 ee 5 d 0 d5 a 644846 b
No.3
On April 1st, a fake ArbitrumToken was suspected of RugPull, and the contract deployer removed all liquidity. Contract address: https://www.oklink.com/cn/bsc/address/0x 6 2d fdb 6 e 54 b 4 e 876 e 5 e 7003 a 71097 dd d5 affaa 05
No.4
On April 2nd, Kokomo Finance ($KOKO) Rug the remaining $1.5 million by modifying the logic contract, which makes the total Rug amount reach 5.5 Million.
No.5
On April 2, AYW Token (AYW) was suspected of Rugpull, and its price fell by 91%. Related contract: https://www.oklink.com/cn/bsc/address/0x 8 ec 798657 f 574 d 6 b 0 d5 3461870 a 0709230 cf 6 f 7 f
On April 2, Script (SCPT) was suspected of Rugpull, and the contract deployer withdrew liquidity, causing a loss of 133,000 US dollars.
No.6
Related contracts: https://www.oklink.com/cn/bsc/address/0x d 4 ac 227 eb 1 a 4 c 0384 aae 06 f 7808 f 08 bb 8 f 516 ebf
No.6
On April 2, the price of OBB (OBB) fell by 91%, and the contract deployer withdrew liquidity, making a profit of $9.6w. Contract address: https://www.oklink.com/cn/bsc/address/0x c 7654 db 2271194632 e 70310 f 8 adc 925 d 1 2b f 5246
On April 4th, MOL (MOL) was suspected of Rugpull, and the contract deployer withdrew $19.2w of liquidity.
No.7
Contract address: https://www.oklink.com/cn/bsc/address/0x 87 f 2d f 6 f 85 b 5833 f 058 abd 7 d 7 eb 41249084 c 2380
On April 4th, a fake GameFi token (GAFI) was suspected of Rugpull, and the contract deployer withdrew the liquidity, making a profit of 7.3 million US dollars.
No.8
Contract address: https://www.oklink.com/cn/bsc/address/0x ad 3396360 beebc 5 c 3d 3 cb 4 c 036 c 370 f 2891 d 8673
On April 5th, TRT token (TRT) was suspected to be Rugpull, the price dropped by 99%, and the contract deployer made a profit of 9.3 million US dollars by withdrawing liquidity
No.9
Contract address: https://www.oklink.com/cn/bsc/address/0x 52 f 56100 bba 2c be 268 e 32512388811630 2c 4 f 668
On April 6th, CBC token (CBC) was suspected of being Rugpull, and the contract deployer withdrew $11.3w of liquidity and made a profit of $8.1w
No.10
Contract address: https://www.oklink.com/cn/bsc/address/0x 9 e 10 cf 57 c 90 c 937 c 6 ab 51 f 4 b 98 ec 1 d5 bfcaf 4804@bigfinancetechApril 7,
(BIGFI) Suspected of Rugpull, the contract deployer removed $18.5w of liquidity.
No.11
Contract address: https://www.oklink.com/cn/bsc/address/0x 4 a 45 a 331930 ee 997 f 7382 e 9 f 001359 e 1 f 2981 a 71
On April 7th, PCORE token (PCORE) was suspected of Rugpull, and the contract deployer withdrew the liquidity and made a profit of 3.75w USD.
No.12
Contract address: https://www.oklink.com/cn/bsc/address/0x 76 d 44 d 2d 4056 b 48 c 30 a 2 eeacbd 158 3d 3 c 7087 a 6 d
On April 7th, Morgan Coin (MORGAN) was suspected of Rugpull, and the contract deployer removed $1.38w of liquidity and made a profit of $0.58w.
No.13
Contract address: https://www.oklink.com/cn/bsc/address/0x e 0 e 058 a 2b ca 2 a 9974 e 3 be 579 c 19 ac 040 e 84 d 2 e 3 c
On April 8, the Pervasive Information Community Organization (PICO) was suspected of Rugpull, and the contract deployer withdrew $11.19w of liquidity.
No.14
Contract address: https://www.oklink.com/cn/bsc/address/0x e 455228 ead 628 c 6 cade 249929 de 58 d 7 cf 41130 cf
On April 8th, OpenAI LASA (LASA) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of 11.19 million US dollars.
No.15
Contract address: https://www.oklink.com/cn/bsc/address/0 x 2d 4256 b 0 ee 0 f 359 ed 3 ab 39148 dceb 56 3d e 1 a 1 e 08
On April 8, OpenAI ATF (ATF) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of 33.96 w USD.
No.16
Contract address: https://www.oklink.com/cn/bsc/address/0x f 830423378 d 0 bad 39 f 8 d 03 2c f 5 df 7187 abe 7 2c 1 c
On April 9th, Zodiac Credit - ZOC (ZOC) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of 7.7 million US dollars.
No.17
Contract address: https://www.oklink.com/cn/bsc/address/0x 76401604 de 3d c 379 aec 0 cf 54005 c 0 d 0937 a 11717
On April 10, MED (MED) was suspected of Rugpull, and the price fell by 80%.
No.18
Contract address: https://www.oklink.com/cn/bsc/address/0x ee 0 ed 249325 a 8284 d 66 af 5 f 98 dcbb 7 c 620 ebbe 45
On April 11, Theory Craft Fames (TYF) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of US$6.9w.
No.19
Contract address: https://www.oklink.com/cn/bsc/address/0x 5459 b 93 a 1 bdf 9 cb 027 e 70 cdf 7 bfc 450 e 41 fdf 326
On April 11, XCAD (PLAY) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of $100,000.
No.20
Contract address: https://www.oklink.com/cn/bsc/address/0x 2 f 872619 2d 599806 e 1 eabbed 1687 e 48 e 38 e 56489
On April 11th, Real Web Project (RWP) was suspected of Rugpull, and the contract deployer withdrew liquidity and made a profit of 18.5 million US dollars.
No.21
Contract address: https://www.oklink.com/cn/bsc/address/0x 79 eb 19 ba 58963 b 11394 fd 14041 c 15027 eabc 1537
On April 12, the Iwr token (IWR) was suspected of Rugpull, and the contract deployer withdrew $3.4w of liquidity.
No.22
Contract address: https://www.oklink.com/cn/bsc/address/0x b 993456 2d 37 e 5 a 6 c 88 3d e 7 ce 54 d 6 febb 36 dcbfda
On April 12, ChainGPT (CGPT) was suspected to be Rugpull, and the contract deployer removed 7.6 million US dollars of liquidity.
No.23
Contract address: https://www.oklink.com/cn/bsc/address/0x 6 e 70 ee 54564298 e 7 f 1 dc 0523 f 8190 aef 8529 ebbf
On April 14, Mulit Level Processing (MLP) was suspected of Rugpull, and the contract deployer removed $4.98w of liquidity.
No.24
Contract address: https://www.oklink.com/cn/bsc/address/0x 354 b 8 2b d 70 a 578 fa 553765 da 23040 a 55380 ee 67 e
On April 15th, a fake Hepton token (HTE) was suspected to be Rugpull, and the contract deployer withdrew the liquidity and made a profit of 5.5w USD.
No.25
Contract address: https://www.oklink.com/cn/bsc/address/0x 9 d 77 c 78 d 1 f 06 d5 f 7 b 599 f 0654 dbb 61 ea 706 d 9 de 3
On April 16, Crown Token (CROWN) was suspected of Rugpull, and the contract deployer withdrew $5w of liquidity.
No.26
Contract address: https://www.oklink.com/cn/bsc/address/0x 820 e 625965 d 0 eac 316 e 98 ee 3 efa 74 fa 6531 f 1315
On April 16, Doge Twitter Token (DOGETWIT) was suspected of Rugpull, and the contract deployer removed $4.1w of liquidity.
No.27
Contract address: https://www.oklink.com/cn/bsc/address/0x 1 f 528 ea 4 d5 d 0 bf 9 e 78 a 15 db 65 ae 07953 edc 6 edf 6
On April 16, Move token (MOVE) was suspected of Rugpull, and the contract deployer removed 8.7w USD of liquidity.
No.28
Contract address: https://www.oklink.com/cn/bsc/address/0x ed 062451 2d 6 d 4 c 8 e 6 b 1335 d5 039 b 53 e 82400 e 037
On April 18, ANT (ANT) was suspected of Rugpull, the price fell by 95%, and about 3.6 million US dollars were transferred away.
No.29
Contract address: https://www.oklink.com/cn/bsc/address/0x d 029 fdbf 7 b 826 c 97982 f 3d abe 4 f 930 d 9148363 fe
On April 18, ArbShibAI was suspected of Rugpull, and the contract deployer withdrew about US$6.8 million in liquidity.
No.30
. Contract address: https://www.oklink.com/cn/arbitrum/address/0x c 9752 2d eaae 1 d 3d 94 cc 491 cc 4 f 81 e 0 b 33 f 33 a 13 a
On April 20th, a Pepe Coin imitation project was suspected of Rugpull, and the contract deployer removed 6.5 million US dollars of liquidity.
No.31
Contract address: https://www.oklink.com/cn/bsc/address/0x 79879 c 0 a 8 b 949458 dfa 60 ca 7 a 8 df 24 f 59 e 4 2b b 1 b
On April 20, 6827 Token ( 6827) was suspected of Rugpull, and the liquidity of 62.3 w USD was removed.
No.32
Contract address: https://www.oklink.com/cn/bsc/address/0x 941 f 3 bef 8 b 076 b 9 ff 978 b 54971 2b 4 eea 6832 ffee
On April 21, fcdep (EPMAX) was suspected of Rugpull, and the contract deployer withdrew $67.4 of liquidity.
No.33
Contract address: https://www.oklink.com/cn/bsc/address/0x 66 fff 5 bb 007 c 4885 a 00 fc 14 bdb 1 eee 389 b 804 ef 7
On April 21, ZKLOTTO (ZKLOTTO) was suspected of Rugpull, and the contract deployer removed about $60.9w of liquidity.
No.34
Contract address: https://www.oklink.com/cn/bsc/address/0x cf 0 c 777 2b 8 c 1 b 1 f 30 aa 61 e 4 c 51 a 2b 3 fec 65990 f 7http://Void.CashApril 23,
The project is suspected of Rugpull, and the contract deployer sold about 20 eth, causing the price to drop.
No.35
Contract address: https://www.oklink.com/cn/eth/address/0x 37 cd 4 e 8875 e 3 edaffdfe 9 be 63958 f 07 effbd 0 bfd$OFIThe project is suspected of Rugpull, and the contract deployer removed all liquidity, about 101w USD, and deposited 551 eth into TornadoCash.
secondary title
No.1
1.3 Social Media Fraud and Phishing Inventory
No.2
On April 1st, the @UnicrnSwap Twitter account posted a phishing link hxxps://uniornswap.org/# Do not interact with the site or approve any transactions.@YogapetzApril 1,
No.3
The Discord server of the project is under attack. Do not click on any published links before confirming the server permissions.
No.4
On April 1st, a fake LayerZero Labs Twitter account posted a phishing link, do not interact with hxxps://layerzeros.network/#.
No.5
On April 1st, the fake @sunsetventurer Twitter account posted a phishing link, do not interact with hxxps://cryptocanvasx.xyz/.
No.6
On April 1st, the fake ChainGPT Twitter account posted a phishing link, do not interact with hxxps://www.chaingpt.in/.
No.7
On April 1st, the fake zkSync Twitter account posted a phishing link, do not interact with hxxps://zksyncdistribution.com/.
No.8
On April 1st, the fake Treasure DAO Twitter account posted a phishing link, do not interact with hxxps://treasure.claims-web3.com/.
No.9
On April 1st, the fake Scroll Twitter account posted a phishing link, Do not interact with hxxps://scroll.cx/.
No.10
On April 2, beware of hxxps://dojocoin.online/presale/index.html and do not interact with it.
No.11
On April 2, the fake Ripple Twitter account @xrpevent_live posted a phishing link, do not interact with hxxps://xrpdouble-official.com/xrp/#.
No.12
On April 2, the fake Vela Exchange Twitter account @vela_exchang posted a phishing link, do not interact with hxxps://app.vela.exchange/.metafabric_ioOn April 2, the fake METAFABRIC Twitter account @
No.13
, post a phishing link, do not interact with hxxps://metafabric-claim.pages.dev/.
No.14
On April 2, the fake GMX Twitter account posted a phishing link, do not interact with hxxps://gmxio.drop-web3.com/.
No.15
On April 2, the fake Scrolls Twitter account posted a phishing link, do not interact with hxxps://scroll.zone/.
No.16
On April 2, the fake zkSync Twitter account posted a phishing link, do not interact with hxxps://zksyncx.pw/.@raise_fiApril 2,
No.17
The Discord server of the project is under attack. Do not click on any published links before confirming the server permissions.
No.18
On April 2nd, beware of a fake Sui airdrop phishing link and do not interact with hxxps://suiprotocols.com/.
No.19
On April 2, the fake Arbitrum Twitter account posted a phishing link, do not interact with hxxps://arbitrumgift.pw/.@cedro_financeApril 3,
No.20
The Discord server of the project was attacked and released a fake airdrop link. Do not click on any published link before confirming the server authority.
No.21
On April 3, the fake Andrew Tate Twitter account posted a phishing link, do not interact with hxxps://www.tate-token.com/.@GyroStableApril 4,
No.22
The Discord server of the project was attacked and posted a fake mint link. Do not click on any published link before confirming the server authority.
No.23
On April 4th, the fake ZetaChain Twitter account posted a phishing link, do not interact with hxxps://zetachain.cc/.
No.24
April 4th, beware of a fake Arbitrum phishing link, do not interact with hxxps://arbitrumprotocol.org/.
No.25
On April 5th, the fake Chainlink Twitter account posted a phishing link, do not interact with hxxps://chainlink.bz/.
No.26
On April 5th, the fake Beep Boop Twitter account posted a phishing link, do not interact with hxxps://beepboopbotz.org/.
No.27
April 5th, beware of a fake Nakamigos phishing link, do not interact with hxxps://nakamigo.io/.
No.28
April 5th, beware of a fake OP airdropped phishing link and do not interact with hxxps://optimismprotocols.com.
No.28
On April 5th, the fake HEX Twitter account posted a phishing link, do not interact with hxxps://hex-layer 2.com/.
No.29
On April 5th, the fake BabyDogeCoin Twitter account posted a phishing link, do not interact with hxxps://babydogecoins.co/.@TriBuzzNFTApril 6,
No.30
The Discord server of the project was attacked and posted a fake mint link. Do not click on any published link before confirming the server authority.@Gravity_FinanceApril 6,
No.31
The Discord server of the project was attacked and released a fake airdrop link. Do not click on any published link before confirming the server authority.
No.32
On April 6, the fake AIPAD Tech Twitter account posted a phishing link, do not interact with hxxps://claim.aipad.technology/.
No.33
On April 6, beware of a fake Dogecoin phishing link, do not interact with hxxps://doge.whitelist.network/.
No.34
April 7, @krakenbet is a scam account, do not interact with hxxps://krakenbet.xyz.
No.35
On April 7th, the fake zkSync Twitter account posted a phishing link, do not interact with hxxps://zksyncx.store/.
No.36
On April 7th, the fake Myria Twitter account posted a phishing link, do not interact with hxxps://claimairdrop.app/.
No.37
On April 7th, the fake DeGods Twitter account posted a phishing link, do not interact with hxxps://degods.ch/.
No.38
On April 8, the fake LayerZero Labs Twitter account posted a phishing link, do not interact with hxxps://layerzero-labs.info/.
No.39
On April 8, the fake Sui Network Twitter account posted a phishing link, do not interact with hxxps://suinetworks.org/.
No.40
On April 8th, beware of a fake Arbswap phishing airdrop link and do not interact with hxxps://arbswap.premint.id/?=claim.
No.41
On April 8th, the fake Ape Coin Twitter account posted a phishing link, do not interact with hxxps://airdrops-apecoin.com/.
No.42
On April 9th, the fake CAWMmunity Twitter account posted a phishing link, do not interact with hxxps://cawnetwork.info/.
No.43
On April 9th, the fake Shardeum Twitter account posted a phishing link, do not interact with hxxps://sharduem.org/.
No.44
On April 10th, the fake Lens Protocol Twitter account posted a phishing link, do not interact with hxxps://lensprotocolddrop.com/claim.html.
No.45
On April 10th, the fake zkSync Twitter account posted a phishing link, do not interact with hxxps://zk-synsc.com/.
No.46
On April 10, the fake Sui Twitter account posted a phishing link, do not interact with hxxps://sui-networks.org/.@meanfinanceApril 11,
No.47
The Discord server of the project is under attack. Do not click on any published links before confirming the server permissions.
No.48
On April 11, beware of a phishing link exploiting Nakamigos and do not interact with hxxps://nakamidead.com/.
No.49
On April 11th, beware of a phishing link for free mint for a fake Nakarocks collection, do not interact with hxxps://nakarocks.com/.
No.50
On April 11, the fake RTFKT Twitter account posted a phishing link, do not interact with hxxps://rtfkt-x-nikeairforce 1.com/
No.51
On April 12th, the fake ChainGPT Twitter account posted a phishing link, do not interact with hxxps://join-chainpt.com/
No.52
On April 12, the fake Venus Twitter account posted a phishing link, do not interact with hxxps://venus-protocols.com/.
No.53
On April 12, the fake zkSync Twitter account posted a phishing link, do not interact with hxxps://whitelist-zk 5 async.org/.@Suteki_NFTApril 13,
No.54
The Discord server of the project is under attack. Do not click on any published links before confirming the server permissions.@chimpsverseApril 13,
No.55
The Discord server of the project was attacked and posted a phishing link. Do not click on any published link before confirming the server authority.@SavedSoulsNFTApril 14,
No.56
The Discord server of the project was attacked and posted a phishing link. Do not click on any published link before confirming the server authority.@walkerworld_April 15,
No.57
The Discord server of the project was attacked and posted a phishing link. Do not click on any published link before confirming the server authority.
No.58
On April 15th, the fake Sei Twitter account posted a phishing link, do not interact with hxxps://seinetworks.cc/.
No.59
On April 15th, the fake Optimism Twitter account posted a phishing link, do not interact with hxxps://join-optimism.info/.
No.60
On April 15, the fake SingularityNET Twitter account posted a phishing link, do not interact with hxxps://singularity.link 3.su/.
No.61
On April 15th, the fake HEX Twitter account posted a phishing link, do not interact with hxxps://claim.airdrophex.com/.
No.62
On April 17, the fake Twitter account @thenakazukis posted a wallet drainer, do not interact with hxxps://nakazukis.xyz/.
No.63
On April 17, the fake SUI Twitter account posted a phishing link, do not interact with hxxps://sui.web3-dashboard.com/.
No.64
On April 17th, a phishing link related to the wallet was found, do not interact with hxxps://outlawsnft.wtf/mint/.
No.65
On April 17th, do not interact with hxxps://www.beanz.icu/, a victim lost 494.7 ETH, interacted with it before.
No.66
On April 17th, the fake SUI Twitter account posted a phishing link, do not interact with hxxps://sui-labs.org/.@agility_lsdApril 18,
No.67
The Discord server of the project was attacked and posted a phishing link. Do not click on any published link before confirming the server authority.@Starknet_idApril 18,
No.68
The Discord server of the project was attacked and posted a phishing link. Do not click on any published link before confirming the server authority.@NakaPenguinsApril 18,
No.69
The twitter account posted a wallet scam, do not interact with hxxps://nakapenguins.com/.
No.70
April 18th, do not interact with hxxps://animalconcerts.live/, this is a phishing link.
No.71
On April 18, the Discord server of the Animal Concerts project was attacked and a phishing link was released. Do not click on any published link before confirming the server authority.
No.72
On April 18, the fake Frax Twitter account posted a phishing link, do not interact with hxxps://frax.netlify.app/.@Zebec_HQApril 19, Project
No.73
It is claimed that a bot posted a fake airdrop link, please do not click on any link posted by this bot.@ETCCooperativeApril 19,
No.74
The Discord server of the project was attacked and released a phishing airdrop link. Do not click on any published link before confirming that you have taken out the server authority.
No.75
On April 19th, watch out for a fake Scroll link appearing on a hacked Twitter account, do not interact with hxxps://scroll-zkp.io/.
No.76
On April 19, the fake Syncswap Twitter account posted a phishing link, do not interact with hxxps://zksyncswap.io/.
No.77
On April 19th, the fake Phala Twitter account posted a phishing link, do not interact with hxxps://phala.app/en/.@zkLinkorgApril 19,
No.78
The Discord server of the project was attacked and released a phishing airdrop link. Do not click on any published link before confirming that you have taken out the server authority.
No.79
On April 19th, the fake Layer Zero Twitter account posted a phishing link, do not interact with hxxps://layerzero-labs.app/.
No.80
On April 20th, the fake ArbDoge AI Twitter account posted a phishing link, do not interact with hxxps://aidoge.me/.
No.81
On April 20th, beware of a fake Consensys phishing link appearing on Twitter, do not interact with hxxps://consensys.financial/.
No.82
On April 20th, the fake Wojak Coin Twitter account posted a phishing link, do not interact with hxxps://claimwojak.com/.
No.83
April 20th, do not interact with hxxps://precmint.xyz/launchmyNFT, it is a phishing link
No.84
On April 20, the Discord server of the LaunchMyNFT project was attacked and posted a phishing link. Do not click on any published link before confirming that you have taken out the server authority.
No.85
On April 20, the fake Pepe Coin Twitter account posted a phishing link, do not interact with hxxps://claimpepe.wtf/.
No.86
On April 21st, be aware that a fake Pepe phishing link appears on Twitter, do not interact with hxxps://pepescoin.com/.@prrfbeautyApril 21,
No.87
Claim a phishing link posted on their Discord server, do not interact with hxxps://pob.claims/.
No.88
On April 21, the fake Azuki Twitter account posted a phishing link, do not interact with hxxps://azuki-vegas.com/.@WeAreMetallicusApril 22,
No.89
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.
No.90
On April 22, be aware that a fake Uniswap x DOH airdrop phishing link appeared on Twitter, do not interact with hxxps://uniswapdoh.com/.
No.91
On April 22, be aware that a fake Suidex airdrop phishing link appeared on Twitter, do not interact with hxxps://airdrop.suidex.live/.@DOHgovphApril 22,
No.92
Stolen Twitter account, do not interact with hxxps://claim.optimsm.net/.
No.93
On April 23rd, beware of a fake Pepe Coin Twitter account posting a phishing link, do not interact with hxxps://pepescoin.com/.@Coredao_OrgApril 23,
No.94
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.@dynexcoinApril 23,
No.95
The Discord server of the project was stolen, and a phishing link was released. Do not interact with hxxps://dynexcoin.xyz/airdrop/, and do not click on any published link before confirming the server authority.@harvest_financeApril 24,
No.96
The Discord server of the project was stolen, and a phishing link was released. Do not click on any published link before confirming the server authority.@kucoincomApril 24,
No.97
The Twitter account has been stolen, please do not click on any posted links before confirming to get back the permission.@FlowX_financeApril 24,
No.98
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.
No.99
On April 24, beware of a phishing link imitating Scroll, do not interact with hxxps://scrolllabs.org/.
No.100
On April 24, the Discord server of the HasukiNFTs project was stolen. Do not click on any published links before confirming that you have taken out the server permissions.
No.101
April 25, beware of a phishing link and do not interact with hxxps://claimrektarb.com/.
No.102
April 25, beware of a phishing link, do not interact with hxxps://pepe.holdings/.
No.103
April 26, beware of a phishing link, do not interact with hxxps://opencampus.pw/.
No.104
April 26, beware of a phishing link, do not interact with hxxps://notable-pepes.io/.
No.105
On April 27th, beware of a phishing link on Twitter, do not interact with hxxps://claimpeepo.army/.
No.106
April 28, beware of a phishing link, do not interact with hxxps://zestypass.xyz/, this is a fake Zesty Zebra's Zesty Pass site.
No.107
April 28, do not interact with hxxps://breederdao.ink/, it is a phishing link.@BreederDAOApril 28,
No.108
The Discord server of the project was stolen, and a fake airdrop link was posted on it. Do not click on any published link before confirming the server authority.@solimax_April 29,
No.109
The Telegram account has been stolen. Do not click on any posted links before confirming that you have obtained the account permission.@JPEGd_ 69 April 29,
No.110
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.@TapioFinanceApril 29,
No.111
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.@Monkes_NFTApril 29,
No.112
The Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.
No.113
Beware of a fake PepeCoin Twitter account posting a phishing link on April 29th, do not interact with hxxps://pepe-claims.net/.@XEX_CryptoThe Discord server of the project has been stolen, please do not click on any published links before confirming the permission to take out the server.
secondary title
No.1
1.4 Others
No.2
On April 3rd, MEV bots were attacked, resulting in a loss of $25.38 million, because transactions in MEV were replaced by malicious verification nodes.
No.3
On April 10, the South Korean exchange GDAC encountered a private key leakage incident, with a total loss of about 13 million US dollars.@BitrueOfficialClaimed that one of their hot wallets was attacked and lost about $23 million.
first level title
2. Safety summary