


AI 'Challenges' Cryptography? Web3 Must Prepare for the Worst, But Must Never Rush Migration


- Core Viewpoint: AI's progress in mathematical research may accelerate attacks on elliptic curve cryptography, sparking industry discussion about migrating assets ahead of time; however, both key figures believe the risk has not yet materialized, ordinary users should not act hastily, and underlying upgrades and user migration are two separate matters.
- Key Elements:
- Justin Drake calls for planning a "fortress mode," concerned that AI may find new mathematical attacks to break ECC before quantum computers mature, with a worst-case scenario window possibly as short as a few months.
- Vitalik acknowledges that AI risk is worth studying, but emphasizes that real-world losses from hasty migration—such as address errors and key mistakes—may be more urgent than attacks that have not yet occurred.
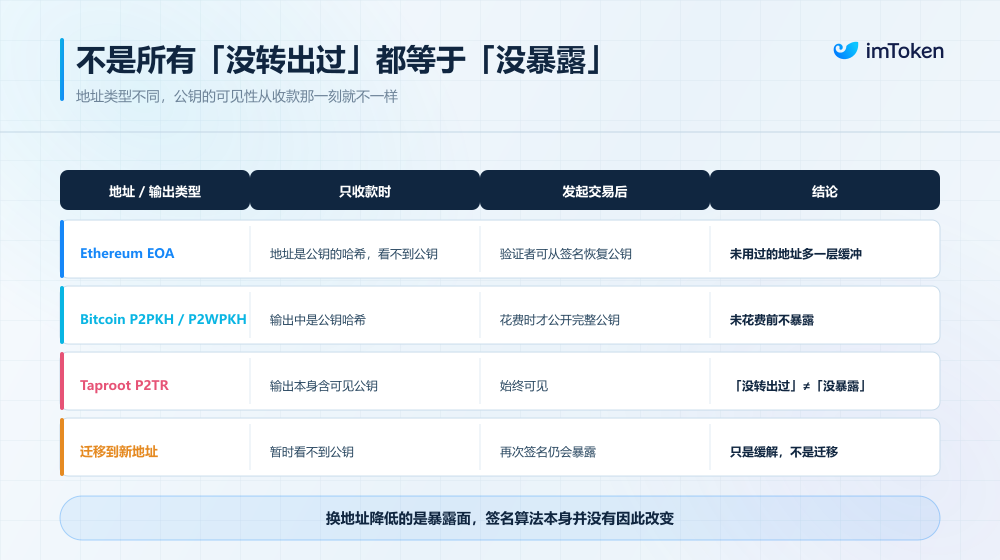
- Ethereum's regular account addresses are hash-processed, and public keys are not exposed until a transaction is initiated; once a transaction is initiated, the public key is recovered and publicly exposed long-term, so risk varies by address type.
- Bitcoin Taproot outputs themselves contain visible public keys; unspent does not mean the public key is unexposed, and new addresses are not inherently quantum-resistant.
- Ethereum has established a Post-Quantum Security team to explore flexible signature schemes such as account abstraction and EIP-8141; NEAR's mainnet already supports ML-DSA post-quantum signatures.
- Wallet upgrades need to accommodate new address types, key management, and hardware compatibility, and require coordination across public chains, smart contracts, and the ecosystem—it is not something that can be solved with "one-click quantum resistance."
- Ordinary users should be wary of phishing links under the guise of "quantum-resistant upgrades"; large holders can optimize address management habits, and reduce migration risk through small-amount testing and batch operations.
Over the past few days, discussions about "AI potentially breaking cryptography" have stirred up a wave of panic in the Crypto community.
The matter originated on October 7, when Justin Drake called on the entire blockchain industry on X to calmly begin planning "Bunker Mode" to prepare for potential cryptographic risks in the future.
His core concern is that as AI continues to advance in mathematical research, the elliptic curve cryptography widely used in networks such as Bitcoin and Ethereum could face new mathematical attack methods even before truly cryptographically capable quantum computers emerge.
In the worst-case scenario he outlined, related breakthroughs could even be measured in "months rather than years," so he suggested that large holders and institutions should be the first to consider orderly asset migration to minimize the potential risks posed by already exposed public keys.
Subsequently, Vitalik Buterin also joined the discussion.
Interestingly, Vitalik did not deny that AI could accelerate cryptographic research, and even went further by suggesting that some cryptographic schemes believed to be resistant to quantum attacks could also be affected by future mathematical breakthroughs.
But on the question of whether ordinary users should immediately migrate their assets, he emphasized that the real losses caused by hasty upgrades and migrations may be more worthy of immediate vigilance than cryptographic attacks that have not yet occurred.
This also raises a long-standing question that troubles the entire crypto industry: When the underlying cryptographic assumptions protecting on-chain assets begin to face new challenges, how far in advance do public chains need to prepare, and when should ordinary users act?
1. Why Is There Risk? First Understand the Distance Between "Addresses" and "Public Keys"
To understand the focus of this discussion, we first need to return to the most fundamental account and signature mechanisms of public chains.
As is well known, in non-custodial wallets, the private key is the key credential for controlling assets. At the technical level, wallets use digital signature algorithms to prove that a transaction has indeed been authorized by the holder of the corresponding key without revealing the private key.
Among these, the most typical is elliptic curve cryptography (ECC).
Taking Ethereum as an example, ordinary externally owned accounts (EOAs) use ECDSA to generate transaction signatures. Bitcoin's traditional signature system also widely uses ECDSA, while Taproot adopts Schnorr signatures based on the same elliptic curve.
These schemes can operate reliably over the long term because they depend on an important mathematical assumption: It is very easy to calculate a public key from a private key, but deriving the private key from the public key alone is almost infeasible under currently known classical computation methods.
We can understand this as a mathematical problem that is easy to verify but extremely difficult to reverse-solve. Anyone on the network can use the public key to verify whether a signature is valid, but cannot easily derive the signer's private key from it.
It is precisely this asymmetry that forms an important foundation of modern blockchain asset ownership.
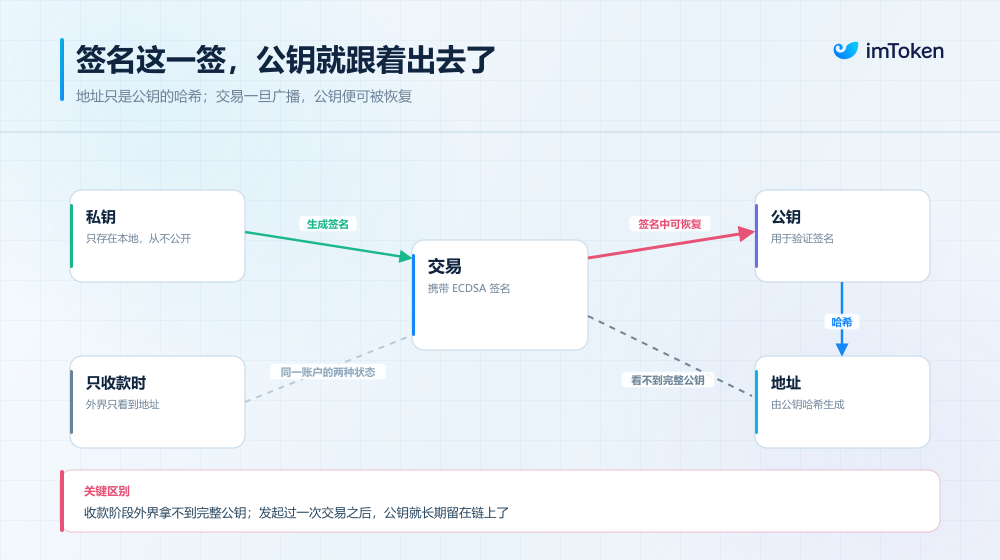
But there is also an easily overlooked detail here: the "wallet address" we see in daily use is not always the complete public key.
Taking an ordinary Ethereum EOA as an example, the wallet address is an identifier generated by applying a Keccak-256 hash to the public key and taking a portion of it. In Bitcoin, common address types such as P2PKH and P2WPKH also adopt designs based on public key hashing.
This creates a very interesting security difference.
For an ordinary Ethereum account that has never initiated an on-chain transaction and has not exposed public key information through other means, the outside world can usually only see the hashed wallet address. Since existing computation methods make it difficult to reverse the full public key from the address hash, the public key effectively has an extra layer of protection.
But when this account actively initiates a transaction and submits an ECDSA signature, nodes can recover the corresponding public key from the signature information. Because on-chain transaction records are public for the long term, this part of the information will also remain continuously exposed to the outside world.
This means that for accounts using public-key-hash addresses, whether the public key has not yet been exposed or has already been exposed may carry different levels of risk when facing certain future cryptographic attacks.
It should be emphasized that this does not mean all public chains follow exactly the same rules.
For example, Bitcoin's Taproot outputs themselves contain a visible elliptic curve public key, so even if a Taproot address has never actively spent funds, it cannot simply be assumed that its public key is still hidden behind a hash function. In addition, some public key information may also be exposed in advance through address reuse, public signatures, extended public keys, or other means.
Therefore, "having never transferred out assets" does not necessarily equal "the public key has not been exposed," and a new address does not inherently have quantum-resistant security.
Once this distinction is understood, it becomes much easier to look at the challenges brought by quantum computing and AI.
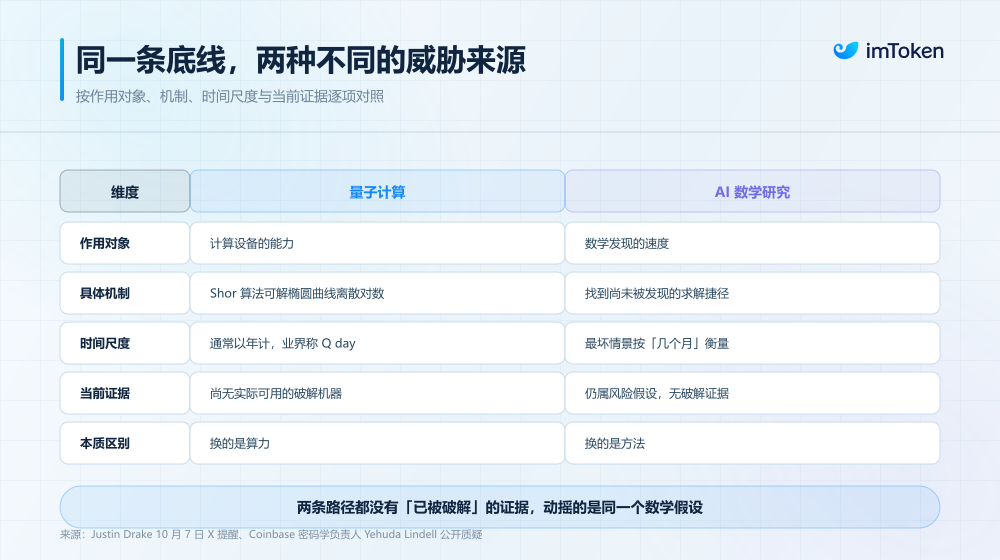
Theoretically, a quantum computer with sufficient scale and error-correction capability could use this algorithm to efficiently solve the elliptic curve discrete logarithm problem and derive the private key from the public key, thereby threatening signature systems such as ECDSA and Schnorr.
But as of now, there is no evidence that a quantum computer capable of actually breaking the mainstream signature systems of Bitcoin or Ethereum already exists.
What Justin Drake raised this time is that, beyond quantum computers, the concern focuses on how AI may help humans discover solution shortcuts that existing mathematical algorithms have not yet found, especially as AI has continued to make progress over the past year in areas such as mathematical reasoning, algorithm search, and formal proofs. Some researchers have begun to rethink whether computational hardness problems that have been tested for decades could be reassessed because of new mathematical discoveries.
2. Justin and Vitalik Have No Fundamental Disagreement
Once the underlying logic is clarified, looking back at the discussion between Justin and Vitalik reveals that their judgments are not completely opposed; they simply assign different priorities to different risks.
Let us first look at Justin Drake.
Traditionally, the replacement of cryptographic systems is often a lengthy process. After all, from identifying potential risks and formulating new standards to completing engineering implementation, and then to compatibility coordination among public chains, wallets, exchanges, custodial institutions, and hardware devices, it often takes years or even longer.
Not to mention decentralized networks such as Bitcoin and Ethereum, which are massive and require extensive coordination. Upgrades at the underlying layer usually cannot be completed with a single version update like ordinary software.
What Justin worries about is precisely that this long upgrade cycle may not keep pace with the speed of future mathematical research breakthroughs.
For example, if AI really helps researchers find new cryptographic attack methods in the future, then even without waiting for quantum computers to gain practical cracking capability, the existing elliptic curve signature system could be threatened in advance.
And once such a breakthrough truly emerges, the migration window left for public chains and the wallet ecosystem may be far shorter than previously expected.
Therefore, his standpoint is to prepare for danger in times of safety, emphasizing that exchanges, large institutions, and users holding large amounts of assets should begin thinking now about future risk-avoidance paths.
This includes taking stock in advance of addresses whose public keys have already been exposed, orderly transferring some long-term holdings to new addresses whose public keys have not been exposed, and minimizing unnecessary signatures and address reuse in subsequent use.
Technically speaking, this suggestion does have its rationality — if future attacks depend on deriving private keys from publicly exposed public keys, then reducing the public key exposure surface in advance could, under certain conditions, buy more defensive time.
But the problem is that transferring funds to a new address whose public key has not been exposed does not equal completing a true post-quantum cryptographic migration.
Because as long as the new address still uses traditional signature schemes such as ECDSA, its underlying security assumptions have not fundamentally changed. Once that address is used to initiate a transaction, the public key may still be exposed again. If the attack capability is strong enough, even the brief window after a transaction is broadcast and before confirmation could become a new risk point.
In other words, this is a transitional risk mitigation measure, not a final solution that can solve the problem once and for all. More importantly, reducing potential risk from a cryptographic perspective does not mean it is necessarily safer from the perspective of actual asset management.
This is also what Vitalik specifically emphasized.
Under currently known technical conditions, directly recovering an ECDSA private key from a public key still lacks a feasible practical attack method. But losses during on-chain asset migration caused by wrong addresses, key backup mistakes, malicious approvals, or other operational issues are real risks that can occur every day.
Vitalik even mentioned that his losses from migration configuration mistakes were greater than those caused by hacker attacks.
For ordinary users who only hold a small amount of ETH, migrating assets may just mean creating a new address, backing up the key, and initiating a few transfers. But for users who have long participated in DeFi, staking, cross-chain interactions, or even manage funds through multisig wallets, the situation is much more complicated.
Assets may be scattered across different networks, some funds may still be in staking or lending protocols, and old addresses may also hold smart contract admin, fund withdrawal, or other critical operational permissions.
If users conduct large-scale asset migration on the spot simply because they saw news that "AI may break wallets," they may instead suffer irreversible losses due to transferring to the wrong network, misusing cross-chain tools, signing malicious transactions, or making multisig operational mistakes.
Not to mention that once panic spreads in the market that "wallets are about to be broken," various links impersonating official quantum-resistant upgrades, asset protection tools, and so-called migration services may also appear.
It is worth noting that Vitalik's caution does not mean he holds a conservative attitude toward underlying cryptographic upgrades.
On the contrary, he also believes that the mathematical progress brought by AI deserves serious study, and even reminds the industry to re-examine some post-quantum schemes based on lattice cryptography, so as to avoid assuming that an algorithm can withstand all future mathematical breakthroughs just because it has been labeled "quantum-resistant."
Where conditions permit, he also leans toward giving more consideration to cryptographic structures based on hash functions and adopting more conservative security parameters for other schemes.
Therefore, Justin and Vitalik cannot simply be categorized into aggressive and conservative camps. There is no fundamental deep contradiction between the two.
3. From Public Chain Upgrades to Wallet Migration: How Far Has Real Quantum-Resistant Preparation Come?
Many users may ask: Since the underlying cryptography carries long-term risk, can wallets directly help me upgrade to a "quantum-resistant wallet"?
Updating the wallet App alone is not enough.
Because for blockchain, cryptographic upgrades involve not only how private keys are generated and how transactions are signed, but also whether the entire network can recognize and verify new signatures, and whether existing accounts can transition smoothly.
In fact, even without this discussion triggered by AI, mainstream public chains and cryptographic research institutions had already begun preparing for the post-quantum era.
Taking Ethereum as an example again, its quantum-resistant preparation already involves multiple levels.
In addition to the ECDSA used by ordinary accounts, the BLS signatures used for validator consensus, the KZG commitments related to data availability, and some zero-knowledge proof systems all involve cryptographic structures that will need to be reassessed or upgraded in the future.
The Ethereum Foundation has established a dedicated Post-Quantum Security research team for this purpose and is exploring technologies such as leanXMSS and leanVM to provide new signature and proof schemes for the consensus layer.
At the account level for ordinary users, account abstraction provides another path worth watching. Unlike traditional EOA signature verification mechanisms, which are tightly bound to the underlying protocol, account abstraction and replaceable signature verification mechanisms are expected in the future to allow user accounts to adopt different signature algorithms, thereby preserving more flexible space for post-quantum upgrades.
For example, EIP-8141, which is still under discussion, is related to Ethereum native account abstraction and is expected to become an important foundation for supporting more flexible signature verification in the future. However, its specific deployment time and final implementation method still await further community discussion and testing.
By contrast, the challenges facing Bitcoin are different.
Because it uses the UTXO model, combined with complex historical address types and some early assets that have been dormant for a long time, Bitcoin not only needs to consider new signature algorithms and output structures, but must also solve the problem of how to migrate a large number of existing assets. At present, related community drafts are still in the proposal and coordination stage.
In addition, some other public chains have also begun attempting more direct engineering implementation. For example, NEAR announced in July 2026 that its mainnet upgrade already supports ML-DSA post-quantum signatures based on FIPS 204, giving accounts the ability to add quantum-safe keys.
Of course, supporting a certain post-quantum signature does not mean that the entire public chain and all its accounts, applications, and infrastructure have already completed quantum-resistant migration.
Putting these developments together, we can see that the real difficulties facing the industry are diverse. They include not only that new cryptographic schemes must be sufficiently secure in theory, but also that signature size, on-chain verification cost, node performance, hardware compatibility, and whether a large number of existing accounts can transition smoothly must all be taken into account.
And these changes at the protocol layer will ultimately land on the wallets users use every day.
For a multi-chain non-custodial wallet like imToken, future cryptographic upgrades cannot be just a simple version update:
- On the one hand, wallets need to gradually adapt to new account and address types, key management methods, transaction signing and verification mechanisms as different public chains upgrade, and may also involve compatibility with hardware wallets, smart contract accounts, and multisig systems;
- On the other hand, wallets also need to translate complex underlying technical changes into operations that ordinary users can understand. Suppose a public chain officially supports a new post-quantum signature scheme in the future. What users really care about is only whether their original address can still be used, whether they need to create a new account, whether the existing mnemonic and hardware devices are compatible, and how already held Tokens, NFTs, staked assets, and DeFi positions should be handled;
Some of these issues can be gradually solved through wallet product capabilities, while others must wait for support from public chain protocols, smart contracts, and the entire ecosystem.
This is also why, the more complex the underlying security upgrade is, the more the user-side migration process needs to undergo sufficient testing, rather than hastily launching a so-called "one-click quantum-resistant" entry point.
So at this stage, what exactly should ordinary users do?
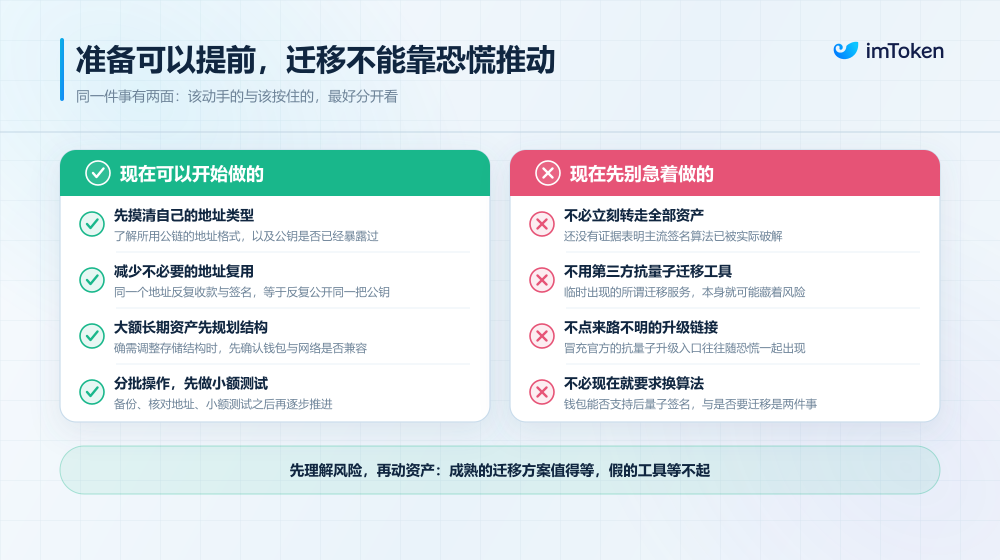
- First, do not immediately transfer all assets simply because of this discussion. There is currently no evidence that the signature algorithms of mainstream public chains have been actually broken. In particular, be vigilant against unfamiliar links and migration tools spread under the name of "quantum-resistant upgrades." Any operation that asks for mnemonic phrases or private keys, or induces signing of unknown transactions, should be treated with high vigilance;
- Second, for large, long-term holdings, users can begin to consciously improve address management habits. For example, understand the public chain and address type you are using, and reduce unnecessary reuse and signing operations for addresses holding high-value assets. If asset storage structure really needs to be adjusted, first confirm wallet and network compatibility, make key backups, verify receiving addresses, and reduce migration risk through small-amount tests and batch operations;
- Finally, and most easily overlooked: whether wallets can support post-quantum signatures in the future and whether users need to migrate assets today are two different questions;
Final Thoughts
In the world of blockchain, we rely on mathematics and code to build trust.
From this perspective, for an open financial network that hopes to carry trillions of dollars in assets over the long term, no one can guarantee that a cryptographic scheme secure enough today will not need adjustment in the coming decades.
But this does not mean that every breakthrough in frontier research requires ordinary users to immediately rearrange their assets.
Cryptographic researchers need to focus on the worst possibilities, public chain developers need to design new security mechanisms in advance, wallet teams need to provide reliable support for future upgrades and migrations, and ordinary users need to avoid making hasty decisions based on unverified information on the basis of truly understanding the risks.
There is no need to assume the crisis is already at hand, nor to underestimate the inevitability of evolution. Stay clear-headed and act prudently.
For every holder, this is the best way to face the unknown.





