






One article to understand the new trends in Ethereum in 2023: ZK and privacy


1. Background
Ethereum co-founder Vitalik Buterin has made it clear that without a technological shift in the privacy transition, Ethereum will fail. Because all transactions are publicly visible, the privacy sacrifice is too great for many users, and everyone will turn to centralized solutions that at least hide the data to some extent.
In 2023, Vitalik conducted a series of research on privacy protection and the advancement of zero-knowledge proofs (ZK) technology. In the first half of the year, Vitalik published three articles on his website specifically discussing ZK and privacy protection.article. In April, he also presented a project on Reddit regarding Wallet Guardian privacy issues.Research. In September, he co-authored an article with other professionalspaper, proposes a solution aimed at balancing privacy and compliance.
In addition, the Ethereum ecosystem is also actively promoting the discussion and popularization of this topic. At the ETHDenver event in March, a special event focused on privacy was held. At the annual EDCON (Ethereum Community Conference) conference in May, Vitalik emphasized that “in the next 10 years,ZK-SNARKwill be as important as blockchain.”
This article tracks the latest developments in the Ethereum ecosystem in 2023 in using ZK technology to promote privacy protection. If you want to join the Ethereum ZK track, this article can provide the necessary interpretation and guidance.
2. Ethereum ZK Track: Building the Future of Privacy Protection
Ethereum’s transparency may put users’ personal information at risk of being leaked. There are no secrets on blockchains such as Ethereum, and all information is public, including transactions, voting and other on-chain activities. Such publicity could lead to specific transactions and addresses being tracked and associated with real user identities. Therefore, implementing privacy protection on Ethereum becomes crucial. Hiding information on the chain can be achieved through encryption technology, but the challenge is to ensure that the validity of these transactions can be verified while protecting privacy.ZKTechnology provides a solution that can prove the authenticity of a transaction without revealing additional information, taking into account both privacy and verifiability.
Ethereum attaches great importance to ZK-SNARK, especially in some key privacy protection application scenarios. This is evident in Vitalik’s research and proposals, and Salus has compiled typical scenarios proposed by Vitalik in his research, namely privacy transactions and social recovery.
2.1 Private transactions
Regarding privacy transactions, Vitalik proposed two concepts: Stealth Addresses and Privacy Pools.
1. The privacy address scheme allows transactions to be conducted while hiding the identity of the transaction recipient. This solution not only provides privacy protection functions, but also ensures the transparency and auditability of transactions.
2. Based on the privacy pool protocol, users can prove that their transaction funds belong to known and compliant sources without disclosing historical transactions. This solution allows users to conduct private transactions while complying with regulations.
Both solutions are inseparable from ZK. In both scenarios, users are allowed to generate zero-knowledge proofs to prove the validity of their transactions.
2.1.1 Privacy address
Suppose Alice intends to transfer some asset to Bob. When Bob receives the asset, he does not want the global public to know that he is the recipient. While it is difficult to conceal the fact that an asset is being transferred, it is possible to hide the identity of the recipient. It is against this background thatPrivacy addressThe solution came into being, and the main problem it solved was how to effectively hide the identity of the transaction recipient.
So, what is the difference between a private address and a normal Ethereum address? How to use ZK-based private addresses for private transactions? Salus will introduce you to each of them.
(1) What is the difference between a private address and a normal Ethereum address?
A private address is an address that allows the sender of a transaction to generate it non-interactively and is only accessible to its recipient. We illustrate the difference between a private address and an ordinary Ethereum address from two dimensions: who generates it and who can access it.
Generated by whom?
Ordinary Ethereum addresses are generated by the user himself based on encryption and hashing algorithms. The privacy address can be generated by the person or the other party to the transaction. For example, when Alice transfers money to Bob, the address used by Bob to accept the transfer can be generated by Bob or Alice, but it can only be controlled by Bob.
Who can access?
The types, amounts and sources of funds under ordinary Ethereum accounts are publicly visible. In transactions using private addresses, only the recipient can access the funds stored in their invisible address. Observers are unable to associate the recipients private address with their identity, thus protecting the recipients privacy.
(2) How to use ZK-based privacy addresses for private transactions?
If Alice wants to send assets to Bobs private address to hide the recipient of the transaction. Below is a detailed description of the transaction process:
1. Generate private address
Bob generates and saves a spending key, which is a private key that can be used to spend funds sent to Bobs private address.
Bob uses the consumption key to generate a stealth meta-address, which can be used to calculate a stealth address for a given recipient, and passes the stealth meta-address to Alice. Alice calculates the privacy meta-address and generates a private address belonging to Bob.
2. Send assets to private address
Alice sends the assets to Bobs private address.
Since Bob does not know that this private address belongs to him at this time, Alice also needs to publish some additional encrypted data (a temporary public key, ephmeral pubkey) on the chain to help Bob discover that this private address belongs to him.
Private addresses in the above process can also be constructed using zero-knowledge proofs constructed from hashes and public key cryptography. Smart contract code in private addresses can be integrated with ZK. By embedding zero-knowledge proof verification logic, smart contracts can automatically verify the validity of transactions. Compared with other schemes for constructing private addresses, this scheme includes elliptic curve cryptography, elliptic curve isogenies, lattices, and generic black-box primitives. Much simpler.
2.1.2 Privacy Pool
Whether private transactions are achieved by hiding the identity of the transaction recipient or other information about the transaction, there is a major problem: how users can prove that their transaction funds belong to a known compliant source without having to disclose their entire transaction history. As a public blockchain platform, Ethereum must avoid becoming a medium for money laundering and other illegal activities.
Vitalik proposed a project called"privacy pool"solutions dedicated to balancing the privacy protection and compliance needs of blockchain. However, what are the privacy protection and compliance challenges? How to balance privacy and compliance? On both issues, Salus provides in-depth and instructive discussions.
(1) Privacy protection and compliance challenges
The challenge of ensuring transaction compliance while achieving privacy protection is vividly demonstrated by analyzing the Tornado Cash case.
Tornado Cash is a cryptocurrency mixer that mixes together a large number of deposits and withdrawals. After the user deposits the token at an address, he or she shows ZK Proof to prove that he or she has deposited the money, and then uses a new address to withdraw the money. These two operations are public on the chain, but the correspondence between them is not public, so they are anonymous. While it can enhance privacy for users, it is often used by illegal actors to launder money. As a result, OFAC, the U.S. Department of the Treasury, ultimately placed Tornado Cash’s smart contract address on the sanctions list. Regulators believe that the agreement facilitates money laundering and is not conducive to the fight against financial crime.
The shortcoming of Tornado Cash in privacy protection is that it cannot verify whether the users token source is compliant. To address this problem, Tornado Cash provides a centralized server to help users prove that their tokens are compliant. However, the server must obtain the specific information about the withdrawal provided by the user, determine which deposit the withdrawal corresponds to, and generate a certificate. This centralized mechanism not only has the cost of trust assumptions, but also creates information asymmetry. Ultimately, the mechanism was used by few users. Although Tornado Cash implements privacy functions, it does not provide an effective mechanism to verify whether the source of user tokens is compliant, which allows criminals to take advantage of it.
(2) How to balance privacy and compliance?
Based on the above challenges, Vitalik proposed the concept of Privacy Pools, which allows users to prove that their fund sources are compliant without revealing historical transaction information. This creates a balance between privacy and compliance.
Privacy Pools are based on ZK and association sets, allowing users to generate and publish ZK-SNARK certificates proving that their funds come from known compliant sources. This means that the funds belong to a compliant association set, or they do not belong to a non-compliant association set.
Association collections are constructed by association collection providers according to specific strategies:
1. Membership Proof: Put deposits from all trusted trading platforms into an associated set, and there is definite evidence that they are low risk.
2. Exclusion Proof: Identify a group of deposits that are flagged as risky, or that there is definite evidence to be non-compliant funds. Construct an associated collection containing all deposits except these deposits.
When making a deposit, the user generates a secret through ZK and hashes it to calculate a public coin ID to mark his association with the funds. When withdrawing money, the user submits a nullifier corresponding to the secret (nullifier is the unique identifier derived from the secret) to prove that the funds are theirs. Moreover, users use ZK to prove two merkle branches to prove that their funds belong to known compliant sources:
1. His coin ID belongs to the coin ID tree, which is the collection of all transactions currently occurring;
2. His coin ID belongs to the association set tree, which is a collection of some legitimate transactions that the user considers.
(3) What are the application scenarios of ZK in privacy pool?
1. Ensure the flexibility of private transactions: In order to handle transfers of any denomination in private transactions, an additional zero-knowledge proof is added to each transaction. This proof ensures that the total denomination of tokens created will not exceed the total denomination of tokens consumed, thereby ensuring the validity of the transaction. Secondly, ZK maintains the continuity and privacy of transactions by verifying each transactions commitment to the original deposit token ID, so that even in the case of partial withdrawals, each withdrawal is guaranteed to be associated with its corresponding original deposit.
2. Resist balance-summing attacks: By merging tokens and committing to a set of token IDs, and committing to the union of parent transactions for multiple input transactions, balance-summing attacks can be resisted. This approach relies on ZK to ensure that all committed token IDs are in their associated set, thereby enhancing transaction privacy.
2.2 Social recovery
In real life, we may have multiple bank card accounts. Losing the bank card password means that we cannot use the funds in the bank card. In this case, we usually go to the bank and ask for help to recover the password.
Similarly, in blockchains such as Ethereum, we may have multiple addresses (accounts). The private key is like a bank card password and is the only tool to control account funds. Once you lose your private key, you lose control of your account and can no longer access the funds in your account. Similar to real-world password retrieval, blockchain wallets provide a social recovery mechanism to help users retrieve their lost private keys. This mechanism allows users to select a group of trusted individuals as guardians when creating a wallet. These guardians can help users regain control of their accounts by approving the reset of a users private key if it is lost.
Under this social recovery and guardian mechanism, Vitalik proposed two privacy protection points that need attention:
1. Hide the correlation between multiple addresses of a user: In order to protect user privacy, we need to prevent the ownership of these addresses from being exposed when using a single recovery phrase to restore multiple addresses.
2. Protect user property privacy from intrusion by guardians: We must ensure that during the process of approving user operations, guardians cannot obtain the users asset information or observe their transaction behavior to prevent user property privacy from being infringed.
The key technology to achieve these two types of privacy protection is zero-knowledge proof.
2.2.1 Hide the correlation between multiple addresses of users
(1) Privacy issues in social recovery: correlations between addresses are disclosed
In blockchains such as Ethereum, in order to protect their privacy, users usually generate multiple addresses for various transactions. By using a different address for each transaction, you prevent outside observers from easily linking those transactions to the same user.
However, if the users private key is lost, the funds under multiple addresses generated by the private key will not be recovered. In this case, social recovery is needed. A simple recovery method is to recover multiple addresses with one click, where the user uses the same recovery phrase to recover multiple addresses generated by one private key. But this approach is not ideal, because the original intention of users generating multiple addresses is to prevent them from being related to each other. If a user chooses to restore all addresses at the same time or at a similar time, this is actually equivalent to revealing to the outside world that these addresses are owned by the same user. This practice defeats the original purpose of users creating multiple addresses to protect privacy. This constitutes a privacy protection issue in the social recovery process.
(2) ZK solution: How to prevent the correlation of multiple addresses from being disclosed?
ZK technology can be used to hide the correlation between multiple addresses of a user on the blockchain through a method that separates verification logic and asset holdings.Architecture(an architecture that separates verification logic and asset holdings) to solve privacy issues during social recovery.
1. Verification logic: Users have multiple addresses on the blockchain, but the verification logic for all these addresses is connected to a main authentication contract (keystore contract).
2. Asset holding and trading: When users operate from any address, they utilize ZK technology to verify operation authority without revealing the specific address.
In this way, even if all addresses are connected to the same keystore contract, external observers cannot determine whether these addresses belong to the same user, thus achieving privacy protection between addresses.
It is very important to design a private social recovery solution that can recover multiple addresses of users at the same time without revealing the correlation between addresses.
2.2.2 Protect user property privacy from intrusion by guardians
(1) Privacy Issues: Guardian’s Privileges
In blockchains such as Ethereum, users can set up multiple guardians when creating a wallet. Especially for multisig wallets and social recovery wallets, the role of the guardian is crucial. Typically, a guardian is a collection of N addresses held by others, where any M addresses can approve an operation.
What privileges do guardians have? for example:
1. For a multi-signature wallet, each transaction must be signed by M of N guardians before it can proceed.
2. For the social recovery wallet, if the users private key is lost, then M out of N guardians must sign a message to reset the private key.
Guardians can approve your actions. In multisig, this would be any transaction. In a social recovery wallet this would be to reset your account private key. One of the challenges facing the guardian mechanism today is how to protect users’ financial privacy from being invaded by guardians?
(2) ZK solution: Protect user property privacy from guardian intrusion
Vitalik is inThis articleIn Zhongzhanwang, what the guardian protects is not your account, but a lockbox contract. The link between your account and this lockbox is hidden. This means that guardians do not have direct access to the users account and can only operate through a hidden lockbox contract.
The main role of ZK is to provide a proof system that allows guardians to prove that a certain statement is true without revealing the specific details of the statement. In this case, guardians can use ZK-SNARKs to prove that they are authorized to perform an action without revealing any details related to the link between the account and the lockbox.
2.3 Exploration: A new chapter of ZK and privacy in the Ethereum ecosystem
Although the Ethereum ZK track is still in the development stage, and many innovative ideas and concepts are still being conceived and researched, the Ethereum ecosystem has already launched more extensive actual exploration activities.
(1) Funding from the Ethereum Foundation
In September this year, the Ethereum Foundation funded two projects on privacy protection.IoTeXandZK-Team. IoTex is an account abstraction wallet based on zero-knowledge proofs, and ZK-Team is committed to enabling organizations to manage team members while maintaining personal privacy.
(2) Investment
In October this year, Ethereum co-founder Vitalik invested inNocturne Labs, aiming to introduce private accounts to Ethereum. Users will have internal accounts in Nocturne, and receiving/spending funds from these accounts is anonymous. Through ZK technology, users can prove that they have sufficient funds for payments, pledges and other transactions.
(3)Meetings and activities
ETHDenver is considered one of the most important Ethereum and blockchain technology-related events in the world. In March of this year, ETHDenver hosted a special event focused on privacy. This event not only demonstrates the Ethereum communitys concern for privacy issues, but also reflects the global blockchain communitys emphasis on privacy protection. In this special event, heldPrivacy by Design、Privacy vs Securityand nine privacy-related themed conferences.
EDCON (Ethereum Community Conference) is a global annual conference hosted by the Ethereum community, aiming to promote the development and innovation of Ethereum and strengthen the connections and cooperation of the Ethereum community. At this year’s EDCON conference in May, Vitalik presented aImportant statement, he said: “In the next 10 years, ZK-SNARKs will be as important as blockchain.” This statement emphasizes the important position of ZK-SNARKs in the development trend of blockchain technology.
(4) Project
At present, some application layer projects have begun to use ZK technology to provide privacy protection services for users and transactions. These application layer projects are called ZK Applications. For example, ZK Application deployed on Ethereum,unyfy, a privacy asset exchange. The transaction order prices here are hidden, and the integrity of these orders with hidden prices is verified by ZK technology. In addition to unyfy, there are other ZK Applications on L2s, such as ZigZag and Loopring. Although these ZK Applications implement privacy protection functions based on ZK, they cannot currently be deployed on Ethereum because the EVM cannot directly run these ZK Applications.
(5) Research
Moreover, researchers areEthereum ResearchThere was a heated discussion on ZK technology and its applications on the platform. Among them, there was an article from SalusResearchThe article is dedicated to using ZK to promote privacy protection and other implementations in the Ethereum application layer. This article tests the performance of several different ZK languages, Circom, Noir and Halo 2, and the results show that Circom has better performance. This article also proposes a general solution to integrate Circom in Solidity to implement ZK-based Ethereum application layer projects. This has important implications for Ethereum’s privacy transition. This study gained significant traction in 2023, ranking at the top of the list.
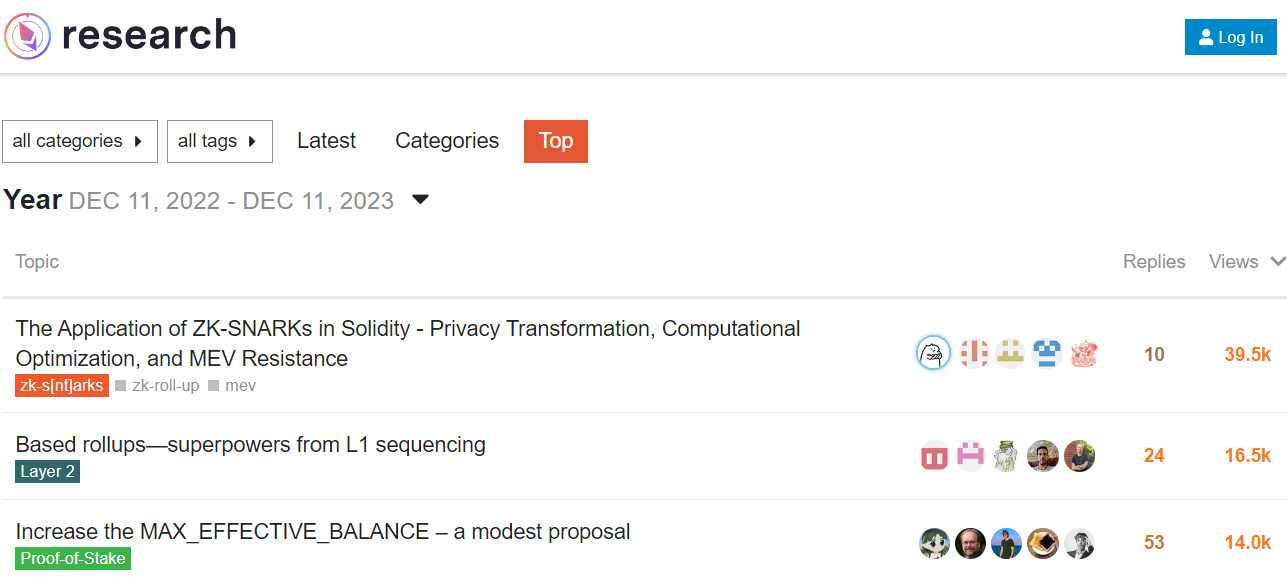
This research article is the most read research in 2023 on Ethereum Research --- Author Salus
3. Challenge
Although many existing Ethereum application layer projects urgently need to introduce ZK-based privacy protection mechanisms, this process faces a series of challenges.
1. Lack of ZK talent resources: Learning ZK technology requires a solid theoretical foundation, especially in the fields of cryptography and mathematics. Since the implementation of ZK technology involves complex formulas, learners also need to have strong formula interpretation abilities. But the problem is that there are relatively few people dedicated to learning ZK technology.
2. Limitations of ZK development languages: Rust, Cairo, Halo 2 and other languages are used to develop ZK proof circuits, but they are usually only applicable to specific scenarios and are not suitable for application layer projects. Some of these languages, such as Cairo, are still in the experimental stage and may have compatibility issues between different versions, which increases the difficulty and complexity of adopting them in real-world applications.
3. Difficulty in implementing ZK technology: The solution proposed by Vitalik to apply ZK technology to Ethereum privacy protection may face a variety of complex problems in actual implementation, such as how to avoid private transactions from being subject to balance summation attacks (balance- summing attacks), double-spending attacks, etc. There are certain technical difficulties in solving these problems.
4. Privacy protection vs. compliance: Although private transactions can protect users’ identities and transaction details, they may also conceal illegal activities, such as money laundering. In the future, it remains to be verified whether ZK Applications on Ethereum can comply with regulations when implementing privacy protection.
Despite the challenges, a prerequisite for Ethereums privacy transformation - ensuring privacy-preserving fund transfers and ensuring that all other tools being developed (social recovery, identity, reputation) are privacy-preserving - is the widespread deployment of ZK Applications. Posted by Salus mentioned aboveResearchBased on ZK technology to promote privacy protection and other functions of the Ethereum application layer. Moreover, Salus proposed for the first time a universal solution that integrates Circom and Solidity and is applied to Ethereum application layer projects. It implements the ZK proof system off-chain based on Circom and implements smart contracts and ZK verification logic on Ethereum based on Solidity. . If you need support or have any questions, feel free toconnectSalus。
4. Summary and outlook
In 2023, the Ethereum community, led by Vitalik Buterin, deeply explored the potential of zero-knowledge proof technology with the purpose of enhancing the platforms privacy protection capabilities. Although these proposals are still in the research stage, Vitaliks research and papers, especially on the balance between privacy protection and compliance, lay the theoretical foundation for zero-knowledge technology to protect user privacy.
Although there are challenges in integrating zero-knowledge proof technology into Ethereum, as the technology matures and the community continues its efforts, it is expected that zero-knowledge proofs will play a more important role in the Ethereum ecosystem in the near future. Therefore, timely participation and active exploration of this field, taking advantage of early opportunities, will help to occupy a favorable position in this emerging field.





