






On-chain guards of the Okey Cloud chain: an inventory of security incidents in March 2023


first level title
secondary title
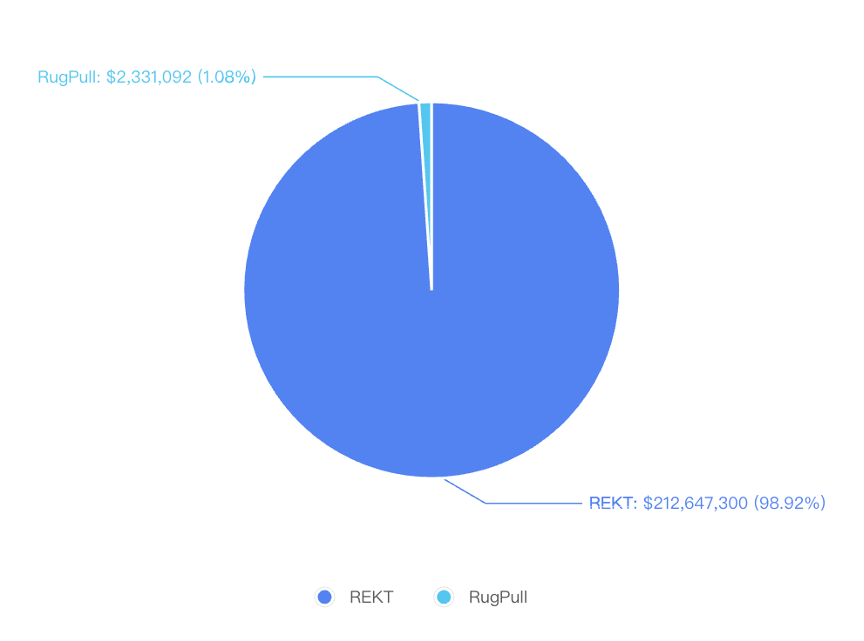
1.1 REKT Inventory
No.1
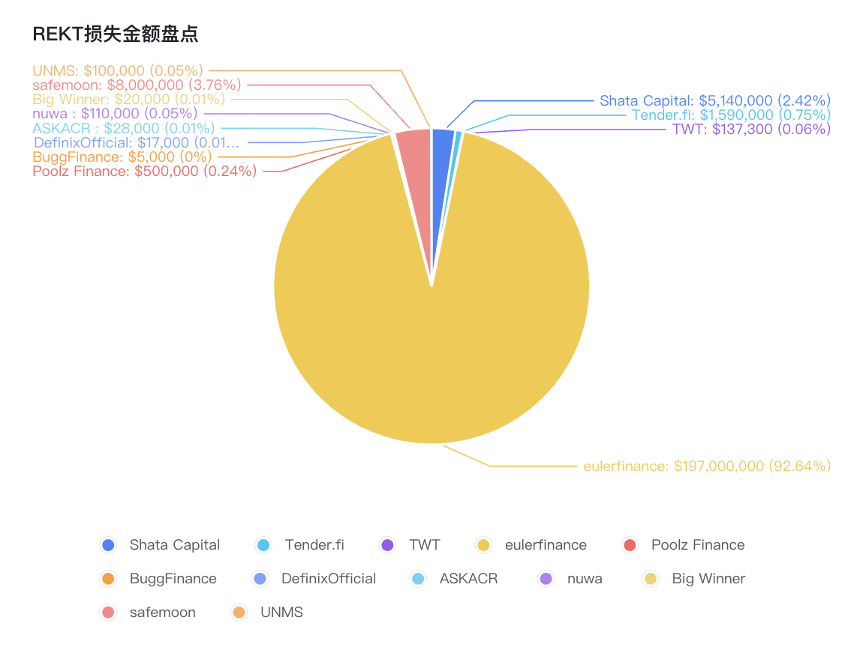
On March 1, the EFVault contract of Shata Capital was attacked after the upgrade, and the loss was about 5.14 million US dollars. The main reason was that the contract upgrade did not take into account the data storage structure of the old version. When reading the assetDecimal variable, the read data is still The proxy contract slot, that is, the value of the old version maxDeposit variable, caused the attacker's asserts to be huge, and the hacker transferred the profit funds to Tornado Cash.
Attack transactions:
https://www.oklink.com/cn/eth/tx/0x 31565843 d5 65 ecab 7 ab 65965 d 180 e 45 a 99 d 4718 fa 19 2c 2 f 2221410 f 65 ea 03743
https://www.oklink.com/cn/eth/tx/0x 1 fe 5 a 53405 d 00 ce 2 f 3 e 15 b 214 c 7486 c 69 cbc 5 bf 165 cf 9596 e 86 f 797 f 62 e 81914
Attack transactions:
EFVault contract address: https://www.oklink.com/cn/eth/address/0x f 491 AfE 5101 b 2 eE 8 abC 1272 FA 8 E 2 f 85 d 68828396
No.2
Attacker address: https://www.oklink.com/cn/eth/address/0x 8 B 5 A 8333 eC 27 2c 9 Bca 1 E 43 F 4 d 009 E 9 B 2 FA d5 EFc 9
oracle address:
https://www.oklink.com/cn/arbitrum/address/0x 614157925 d 4 b 6 f 7396 cde 6434998 bfd 0478927 2d
Attack transactions:
https://www.oklink.com/cn/arbitrum/tx/0x c 6 e 90441 a 684 f 370 f 0 a 1 cd 845 e 0 d 639088 df 20548 a 5 c 2d 37 f 770 cc 85 ea 7306 f 9
No.3
On March 13, the Euler Finance project was attacked, with a total loss of approximately $197 million. The main reason for this attack is that there is a loophole in donateToReserve in the Euler Pool contract. Since this function lacks a check on the caller's position health, users can voluntarily give up part of their leveraged deposits to make their own positions unbalanced, and then use Euler's characteristic liquidation rules to liquidate their own positions to make a profit. The attacker responded to the attack and claimed to return the stolen funds.
Attack transactions:
https://www.oklink.com/cn/eth/tx/0x c 310 a 0 affe 2169 d 1 f 6 feec 1 c 6 3d bc 7 f 7 c 62 a 887 fa 48795 d 327 d 4 d 2d a 2d 6 b 111 d
No.4
Attack transactions:
On March 15, Poolz Finance's LockedDeal contracts on ETH, BSC, and Polygon were attacked, worth approximately $500,000. The attacker calls the vulnerable function "CreateMassPools". Since the contract version is relatively low and the overflow check is not performed in the contract, the attacker passes in a malicious value in the parameter _StartAmount to trigger an integer overflow vulnerability.
ETH attack transaction: https://www.oklink.com/cn/eth/tx/0x 118 a 617 bddd 1 c 14810113 be 81 ce 336 f 28 cc 1 ee 7 a 7 b 538 a 07184 b 93 e 7 c 51 bdc 00
https://www.oklink.com/cn/bsc/tx/0x 39718 b 03 ae 346 dfe 0210 b 1057 cf 9 f 0 c 378 d 9 ab 943512264 f 06249 ae 14030 c 5 d5
BSC attack transaction:
https://www.oklink.com/cn/polygon/tx/0x 606 be 0 ac 0 cdba 2c f 35 b 77 c 3 ccbbd 8450 b 82 e 16603157 facec 482958032558846
No.5
Polygon Attack Transactions:
On March 16, BuggFinance was attacked, and the project lost about $5,000. The hacker called the 0x 814 b 2047 method of the 0x Fea 6 aA 4 a 9 d 44137 Ac 7 cA 1 a 288030 A 4161 f 686 df 3 contract to modify the slot of the contract to The malicious $XjdgZU token address (0x 616 F 26 C 1394645653 C 74 FEa 49029 DBf 4 d 8119482) created by the attacker bypasses the check in the swap function of the victim contract by constructing malicious parameters and exchanges $XjdgZu for BUGG, and then The exchange is 17 BNB, and the profit is completed.
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x 01 e 8 efe 7 b 5 d 791 b 0786 a 23 e 98 dcd 1 af 196863 c 85 d 86 af 2d e 0 f 9 f 3178 ffb 9903 b
No.6
Victim contract: https://www.oklink.com/cn/bsc/address/0x Fea 6 aA 4 a 9 d 44137 Ac 7 cA 1 a 288030 A 4161 f 686 df 3
On March 17, the DefinixOfficial project was attacked by price manipulation and lost about $17,000. Due to the low liquidity of Definix, the attacker first performs swap to manipulate the price, and then calls RebalancePool.rebalance () to forcibly restore the price, making a profit of 51 BNB.
No.7
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x 5 de 8 b 8 ac 186116 ea 7 d 887 b 3366 de 953 f 9 facb 77 ef 694 ddcd 4 a 3 e 4641 c 57217 c 0
On March 17, the ParaSpace project was attacked. The white hat hackers attacked and returned the relevant assets first. The project did not suffer any financial loss. The main reason is that the function scaledBalanceOf( ), this function is used to calculate the user's collateral through the supply() function. However, scaledBalanceOf() can return a large value by manipulating the number of APE tokens in the function getPooledApeByShares(). Users can hold a large amount of collateral and use it to borrow more assets.
No.8
Attack transaction: https://www.oklink.com/cn/eth/tx/0x e 3 f 0 d 14 cfb 6076 cabdc 9057001 c 3 fafe 28767 a 192 e 88005 bc 37 bd 7 d 385 a 1116 a
On March 21, the ASKACR Token on the BSC chain was attacked, and the project lost 85 BNB of about $28,000. The root cause was that in the transfer function, rewards were distributed to lp holders, but the transfer amount was not verified, which led to the attack Those who first add a large amount of liquidity and then make profits through batch zero amount transfers.
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x c 24 a 5705670873 f 21 c 937499 ca 4493 a 1 a 5423 a 9 be 44 b 406 bebfc 6 bd 7726 adca 3
No.9
Victim contract: https://www.oklink.com/cn/bsc/address/0x 5 aE 4 b 2 F 92 F 03717 F 3 bdFE 3 B 440 D 14 d 2 f 21 2D 3745
On March 22, the nuwa project on the BSC chain was attacked, and the loss was about 110,000 US dollars. The main reason was that there was a backdoor function 0x fa 319 eee in the open-source nuwa contract, which would replace the deposited $BUSD with $nuwa and All $nuwa sent to the caller. It is worth noting that the original attacker was preempted by the MEV robot 0x 286 E 0993 2B 8 D 096 cbA 342 3d 12965042736 b 8 F 850, and the robot then sold the profitable nuwa for profit.
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x 4 cd 49 b 9 bf 7 ee 4 d 1 bd 1265 a 0 eaec 2 f 3 c 2 2b eabbb 91 f 1 dae 1848 f 2c efe 774 aa 9 2c
https://www.oklink.com/cn/bsc/address/0x 11 a 31 bb 12 f 57 b 0 f 3d d 403 f 6 b 73 ea 28 c 64 fdb 5 ccb
No.10
On March 25, the project Big Winner on the BSC chain was attacked, and the project lost 20,000 US dollars. The main reason was that there was an error in the calculation of the project reward. The reward was based on the proportion of the user's current LP holdings, and multiple dividends after the LP transfer were not considered. The attacker creates multiple sub-contracts, transfers the LP obtained by increasing liquidity to the sub-contracts in turn, and then the sub-contracts pledge LP, receive rewards through getStaticIncome, and withdraw LP through redemption_lp.
Attack transactions:
https://www.oklink.com/cn/bsc/tx/0x 99 b d5 00387 e 8135 c 15 dc 6 c 04 fb 3 cb 5 d 2d 50 ff 8 d 14 2c 2 f 1 bd 3d 8 eca 21 f 80565 3d
No.11
On March 29, the safemoon project was attacked. Because a public burn vulnerability was introduced when the project updated the contract, the attackers burned the tokens in the apir pool to increase the price of the attack.
Attack transactions:
https://www.oklink.com/cn/bsc/tx/0x 48 e 52 a 1 2c b 297354 a 2 a 1 c 54 cbc 897 cf 3772328 e 7 e 71 f 51 c 9889 bb 8 c 5 e 533 a 934
No.12
secondary title
Attack transactions:
https://www.oklink.com/cn/bsc/tx/0x 5 feb 28 c 35 ddda 566 cf 224714 f 7 f 721 d 093 ab 1 de 964 ea 0420 f 025 dd 44 d 953 a 344
1.2 RugPull Inventory
No.1
1.2 RugPull Inventory
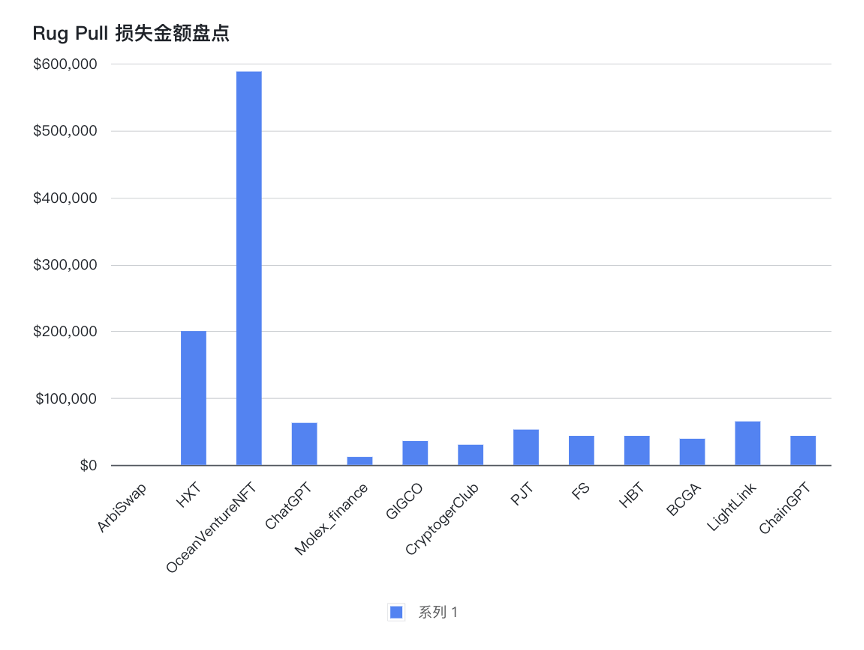
On March 2, the Arbitrum ecological DEX ArbiSwap was suspected of Rug Pull. ArbiSwap deployers minted 1 trillion ARBI before Rug Pull, and then converted ARBI to USDC, resulting in a sharp drop in ARBI in the USDC/ARBI transaction pair. In the next block , the robot conducts space arbitrage through the transaction from USDC to ARBI and then to ETH, making a profit of 68.47 ETH, about 100,000 US dollars. ArbiSwap has transferred 84 ETH to the Ethereum mainnet and sent it to TornadoCash.
Related transactions: https://www.oklink.com/cn/arbitrum/tx/0x 54 ca 307057 b 38110 f 60 fce 515 ba 35321 fde 8 2b 876 b 4 a 2 abf 77368924903216 e 1
https://www.oklink.com/cn/arbitrum/address/0x 9 dB 8 a 10 C 7 FE 60 d 84397860 b 3 aF 2 E 686 D 4 F 90 C 2b 7
No.2
Contract address:
On March 2, Hex Trust Token (HXT) project, suspected RugPull, 670 BNB (~$200,000) was transferred to TornadoCash
No.3
Contract address: https://www.oklink.com/cn/bsc/address/0x 0003018 BA 0 2B acafC 28 cd 8926 D 4 a 46 A 4 bb 20 d 76 A#code
On March 3rd, OceanVentureNFT project, suspected RugPull, token price dropped 98%, 50 wallets sold tokens for ~$588k. Tokens are distributed by EOA 0x e 7 e.
No.4
Contract address: https://www.oklink.com/cn/bsc/address/0x A 592581 FC 325 a 368 f 17 D 0 B 3 B 82854 f 4 c 9 f 3 E 4400
On March 5th, the fake ChatGPT project, suspected RugPull, contract deployers withdrew $62,800 in liquidity and deleted their social media accounts.
No.5
Contract address: https://www.oklink.com/cn/bsc/address/0x C 73126 E 7 f 0 b 24 Eba 8 f 5430768650 C 8233 c 875985
On March 7th, the Molex_finance project, suspected of RugPull, the contract deployer removed liquidity and deposited 42.8 BNB (approximately $12,000) into TornadoCash.
No.6
Contract address: https://www.oklink.com/cn/bsc/address/0x d 6 F 71 D5 9 bC 11221733637 3d 03245 Cc 59 E 50 2C DCd
On March 8, the price of the prvt_data (PRVT) project, suspected of RugPull, dropped by 87%.
No.7
Contract address: https://www.oklink.com/cn/bsc/address/0x 2578 F 9 Dc 1 a 9 F 3 C 4784 BD 6 D 9 D 69 A 1070607 DC 898 c
On March 9, the CryptogerClub ($CToger) project, a suspected RugPull contract deployer, withdrew 105 BNB ($30.2 k) of liquidity.
No.8
Contract address: https://www.oklink.com/cn/bsc/address/0x 910 b 0 Cb 55121190 d 9 E 4176 D 449 E 26 EE 3 BBbBff 1 F
On March 9th, the fake GIGCO token (GIG) project, suspected of RugPull, the contract deployer withdrew $35,700 in liquidity.
No.9
Contract address: https://www.oklink.com/cn/bsc/address/0x 7 A 51 D 02 aba 1751 B 4917 E 9 D5 a 21 bB 6 A 179 ef 8 B 791
On March 9, the PJT (PJT) project, contract deployers withdrew $52,800 in liquidity.
No.10
Contract address: https://www.oklink.com/cn/bsc/address/0x d 6 B 51 f 9017 fe 83 c 636 b 1 d 769 DA 9 Bd 61 C 27 AdD 018
On March 10, the price of Mosquitos_fin on the aptos chain dropped by 99%, and the administrator minted a large number of tokens for selling.
No.11
Contract address: https://www.oklink.com/cn/aptos/address/0x 4 db 735 a 9 d5 7 f 0 ed 393 e 44638540 efc 8 e 2 ef 2d ccca 3 bd 30 c 29 bd 09353 b 6285832
On March 10, the FS project, the contract deployer withdrew $43,400 in liquidity.
No.12
Contract address: https://www.oklink.com/cn/bsc/address/0x e 3 a 19 e 70987 b 5 aa 6643343729 cC 0 B 327 d 76 dE 70 A
On March 10, the HBT project, the contract deployer withdrew $43,400 in liquidity.
No.13
Contract address: https://www.oklink.com/cn/bsc/address/0x e 3 a 19 e 70987 b 5 aa 6643343729 cC 0 B 327 d 76 dE 70 A
On March 13, the BCGA project Rug Pull on the bsc chain, the owner 0x 44 f 2526 bca 61 fb 789 fef 81 c 3 a 36 bee 2 fdecf 8 acb called 0x 25 bbb 5 ae to mint a large amount of $BCGA, and then immediately exchanged for 128.45 BNB, making a profit of about $39,092.
No.14
Attack transaction: https://www.oklink.com/cn/bsc/tx/0x 59367 a 104 e d5 737 fc 61691 dd 7 a 09 c 4 a 34 e 590 aa 5 a 7 f 340 d 06 c 3592 e 66004355 c
On March 16, the DofferingDoc project, the token price dropped by more than 83%.
No.15
Contract address: https://www.oklink.com/cn/bsc/address/0x f 9 d5 01495055 E 17 F 681 D 7 Cd 858 Ef 6628 dFF 71823
On March 18, the LightLink (LL) project, contract deployers withdrew $65,000 in liquidity.
No.16
Contract address: https://www.oklink.com/cn/bsc/address/0x 44 CE 3 a 2 e 98125 c 1 C 370 Beb 6 fbA 6 E 8 Bc 19 CaB 3 fD 9
On March 18, the ChainGPT (CGPT) project, contract deployers withdrew $43,400 in liquidity.
No.17
Contract address: https://www.oklink.com/cn/bsc/address/0x 6 e 70 ee 54564298 e 7 F 1 dc 0523 f 8190 aEf 8529 eBBF
On March 18, the Sloth Climb (SLOTH) project, liquidity worth $93,500 was removed by EOA 0x e 9 b 7 d.
No.18
Contract address: https://www.oklink.com/cn/bsc/address/0x BCC 1 AE 526 d 8 BeBAB 02 af 19945 A 866 dDC 0 DF 80 F 37
On March 19, the APPLE token project, the contract deployer withdrew $30,000 in liquidity, and the price dropped by 95%.
No.19
Contract address: https://www.oklink.com/cn/bsc/address/0x 8 F 81 bbC 8 Cd 2484 b 252 e 8288528 cf 2 ec 903619369
On March 19, the SpaceID (ID) project, contract deployers withdrew 96.5 BNB (~$32k) of liquidity.
No.20
Contract address: https://www.oklink.com/cn/bsc/address/0x 8993 bb 14 2c 1 be 4 dd 2 2c 1 f 79 b 3 a 68 b 1885 2b 55 aad
On March 20, the FlyghtLite (FLE) project, the contract deployer withdrew 95 BNB (~$31k) of liquidity.
No.21
Contract address: https://www.oklink.com/cn/bsc/address/0x 8993 bb 14 2c 1 be 4 dd 2 2c 1 f 79 b 3 a 68 b 1885 2b 55 aad
On March 21, the BNQ project RugPull on the bsc chain, the contract owner invoked the back door of the contract, obtained a large number of tokens for selling, and made a profit of 71,000 US dollars.
No.22
Related transactions: https://www.oklink.com/cn/bsc/tx/0x 97824224 c 549 a 5 a 5158 d 7 2c 34166 ae 88 f 538 fecb 491 dfb 4 bff 548 efabb 624 b 28
On March 21, the BELE_GameFi (BELE) project removed $66,600 in liquidity.
No.23
Contract address: https://www.oklink.com/cn/bsc/address/0x 6 e 3d 2986 a 5 dea 289 d 2682 acbba 684814 d 63 e 9 eb 9
On March 21, the culs ($culs) project removed $27,800 in liquidity.
No.24
Contract address: https://www.oklink.com/cn/bsc/address/0x c 31 AbB 4 BE 8 d 3877 2b 90 b 46 BE 7 e 88 f 84 Cfe 08 cef 9
On March 22, the fake SpaceID project withdrew $191,000 in liquidity.
No.25
Contract address: https://www.oklink.com/cn/bsc/address/0x 1472 a 65 DdB 95 d 3575 A 38 adf 55 b 0 c 38 E 6 adD 22278
On March 22, another fake SpaceID project withdrew $33,000 in liquidity.
No.26
Contract address: https://www.oklink.com/cn/bsc/address/0x 42837 f 96 2d add 0951235 d 7694451 f 6 ed 68072 ece
On March 23, the DEAT token project withdrew $63,800 in liquidity.
No.27
Contract address: https://www.oklink.com/cn/bsc/address/0x 6 A 187 2c 88 d 45 e 1 e 38045582133 a 77 f 021 A 14184 d
On March 23, a fake Arbitrum token token project removed $59,000 in liquidity.
No.28
Contract address: https://www.oklink.com/cn/bsc/address/0x C 7 Ecf 9 dc 57076 eFEa 7009 a 24 c 7155968 CbEB 7500
On March 24, the EC token project removed $43,000 in liquidity, and the price dropped by 98%.
No.29
Contract address: https://www.oklink.com/cn/bsc/address/0x E 7 a 4 d 4669 Ad 6 b 445 F 213 e 213768 d 0673 c 2637795
On March 24, the DESTINY project removed $120,000 in liquidity, and the price dropped by 98%.
No.30
Contract address: https://www.oklink.com/cn/bsc/address/0x 673246 c 704 b 6 ba 3982549230 e 9 b 05 acf 07 c 255 b 6
On March 25th, the EDAO project removed $39,300 in liquidity, and the price dropped by 99%.
No.31
Contract address: https://www.oklink.com/cn/bsc/address/0x 90088 2B e 74 c 5 Cb 53 eF 0 2D 603 fCF 006 CDEf 0495 c 9
On March 26, KOKO project, the price dropped by 99%.
No.32
Contract address: https://www.oklink.com/cn/optimism/address/0x 7 da 25 bc 4 cfaed 3 f 29414 c 6779676 e 53 b 19 a 356 f 5
On March 27, the ARKEN project removed $81,000 in liquidity, and the price dropped by 99%.
No.33
Contract address: https://www.oklink.com/cn/bsc/address/0x 636 cc 5 d 886 F 928 c 2 E 3 3d 0 d5 2 b 0 fcAe 0155 CbCE 25
On March 27, the AGD project removed $49,000 in liquidity, and the price dropped by 99%.
No.34
Contract address: https://www.oklink.com/cn/bsc/address/0x 6 d 04 B 585 eC 4 b 3 fE 27 d5 356 ca 270 fD 6 bd 4 3d 0 Af 47
On March 28, the MYSL project removed $38,300 in liquidity, and the price dropped by 99%.
No.35
Contract address: https://www.oklink.com/cn/bsc/address/0x 3 Ec 8 e 938 C 7 EFb 109 B 60 D 27 e 754 2D B 283 e 297378 f
secondary title
1.3 Social Media Fraud and Phishing Inventory
No.1
1.3 Social Media Fraud and Phishing Inventory
No.2
On March 1, the Discord server of the WickensNFT project was attacked, and the attacker released a phishing message.
No.3
On March 1, the Discord of TheDogePound NFT project was attacked, and the attacker released phishing messages.
No.4
On March 1, the Discord server of the aliquoxyz project was attacked, and the attackers released phishing messages.
No.5
On March 2, the Discord server of the MetaclubSociety project was attacked, and the attacker posted false news.
No.6
On March 3, the @CetsB 00 bs twitter account posted a phishing link hxxps://launclnmynft.io Do not interact with the site or approve any transactions.
No.7
On March 4, the @arbitrum Twitter account posted a phishing link. Do not interact with hxxps://arbitrum-live.com/.
No.8
On March 4, the @FractonProtocol Twitter account posted a phishing link. Do not interact with hxxps://fratcon.cool/.
No.9
On March 4, the @LegendsYokai Twitter account posted a phishing link. Do not interact with hxxps://legendyokai.com/.
No.10
On March 4, the Discord server of the FiHPnft project was attacked, and the attacker posted false news.
No.11
On March 5, the fake @Uniswap Twitter account posted a phishing link. Do not interact with hxxps://app.connectify-web3.com/
No.12
On March 5, the Discord server of the GGMC_nft project was attacked, and the attacker released false news.
No.13
On March 6, the Discord server of the zkboredapes project was attacked, and the attacker posted false news.
No.14
On March 5, a fake @arbitrum Twitter account posted a phishing link, do not interact with hxxps://arbiitrum-bridge.club/.
No.15
On March 8, the Discord server of the DumpiesNFT project was attacked, and the attacker released false news.
No.16
On March 9, the Discord server of the CasualSloths project was attacked, and the attacker posted false news.
No.17
On March 9, a fake @quant_network Twitter account posted a phishing link, do not interact with hxxps://stake-quant.com/.
No.18
On March 9th a fake @apecoin twitter account posted a phishing link, do not interact with hxxps://apescoineth.com/.
No.19
On March 9, the Discord server of the generative_xyz project was attacked, and the attacker posted false news.
No.20
On March 9, a fake @Polkadot Twitter account posted a phishing link, do not interact with hxxps://claim.polkapot.network/.
No.21
On March 10, a fake @SingularityNET Twitter account posted a phishing link, do not interact with hxxps://singularitynet-airdrop.org/.
No.22
On March 11, the Discord server of Theta_Network project was attacked, and the attacker released false news.
No.23
On March 11, the Discord server of the DanketsuNFT project was attacked, and the attacker released false news.
No.24
On March 10th, due to the recent attack on Euler Finance, phishers created a phishing website, please do not interact with hxxps://eulerrefunds.com.
No.25
On March 14, a fake @Gamiumcorp Twitter account posted a phishing link, do not interact with hxxps://gamium-airdrop.com.
No.26
On March 15, a fake @FEGtoken twitter account posted a phishing link, do not interact with hxxps://fegtokens.in/.
No.27
On March 16, the Discord server of the EchelonFND project was attacked, and the attacker posted false news.
No.28
On March 16, a fake @abraCATabranft twitter account posted a phishing link, do not interact with hxxps://mint-page.github.io/-abraCATabra/.
No.29
On March 17, the phishing website hxxps://maroon-golden-track[.]glitch[.]me/indcoinh[.]html was advertised as a fake coinbase recovery page.
No.30
On March 18, a fake @BoredApeYC Twitter account posted a phishing link, do not interact with hxxps://mdvmm-summon.xyz/.
No.31
On March 18, a fake @arbitrum Twitter account posted a phishing link, do not interact with hxxps://arbitrum l2.io/airdrop/.
No.32
On March 19, the Discord server of the DreamlandGEN project was attacked, and the attacker posted false news.
No.33
On March 19, a fake @avalancheavax Twitter account posted a phishing link, do not interact with hxxps://avax-v2.xyz/.
No.34
On March 20, the Discord server of the bobanetwork project was attacked, and the attacker released false news.
No.35
On March 21, the Discord server of the theartbankers project was attacked, and the attacker posted false news.
No.36
On March 21, a fake @arbitrum Twitter account posted a phishing link, do not interact with hxxps://claim.arbltrum.foundation/.
No.37
On March 22, a website hxxps://airdrop.arbitram.io/AbJJ that attempted to use arb airdrops for phishing has successfully defrauded $97,000. Please do not interact with it.
No.38
On March 23, a fake opensea airdrop phishing website hxxps://aidropopensea.com/, please do not interact with it.
No.39
On March 23, a fake blur airdrop phishing website hxxps://blur-airdrop.top/, please do not interact with it.
No.40
On March 24, the Discord server of the KaspaCurrency project was attacked, and the attacker posted false news.
No.41
On March 24, a fake zkSync airdropped a phishing website hxxps://zsync.cc/, please do not interact with it.
No.42
On March 25, the Discord server of the arbitrum project was attacked, and the attacker posted false news.
No.42
secondary title
1.4 Others
No.1
1.4 Others
No.2
first level title
2. Safety summary
2. Safety summary





