






On-chain guards of Okey Cloud Chain: Inventory of security incidents in February 2023


first level title
secondary title
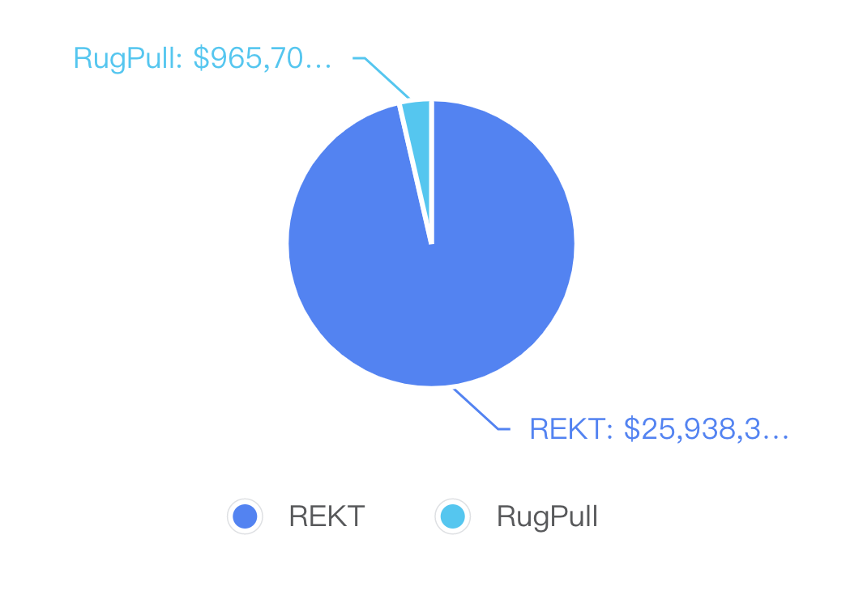
1.1 REKT Inventory
No.1
1.1 REKT Inventory
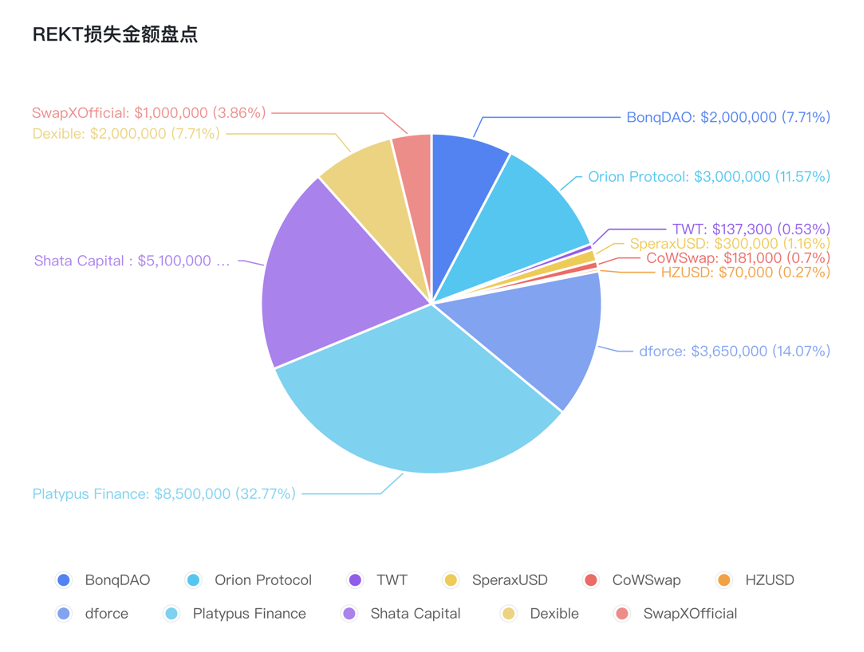
On February 2, the non-custodial lending platform BonqDAO and the encrypted infrastructure platform AllianceBlock were hacked due to BonqDAO’s smart contract vulnerabilities, and lost tokens worth about 120 million US dollars. The profit is about 2 million US dollars. After mortgaging 10 TRB tokens, the hacker has the authority to call the "updatePrice" function of the oracle in the Bonq smart contract, and then updates the feed price of the WALBT collateral Tellor. The attacker sets the price of WALBT to an extremely high value, which allows him to borrow the asset with little collateral in the same transaction after updating the price. The attacker then mints assets from Bonq with almost zero collateral and converts them into other assets.
Attack transaction: https://www.oklink.com/zh-cn/polygon/tx/0x 31957 ecc 43774 d 19 f 54 d 9968 e 95 c 69 c 882468 b 46860 f 921668 f 2c 55 fad d5 1 b 19
BonqDAO contract address: https://www.oklink.com/zh-cn/polygon/address/0x 4248 fd 3 e 2c 055 a 02117 eb 1 3d e 4276170003 ca 295
No.2
Attack contract: https://www.oklink.com/zh-cn/polygon/address/0x e d5 96991 ac 5 f 1 aa 1858 da 66 c 67 f 7 cfa 76 e 54 b 5 f 1 Attacker address: https ://www.oklink.com/zh-cn/polygon/address/0x cacf 2d 28 b 2 a 5309 e 099 f 0 c 6 e 8 c 60 ec 3d df 656642
On February 3, Orion Protocol suffered a reentrancy attack and lost more than $3 million on the ETH and BSC chains. The main reason for this vulnerability is that the swapThroughOrionPool function allows users to provide a path for exchanging tokens, and the hacker hijacks the exchange path by constructing a malicious token containing a hook, and transfers the call logic to the depositAsset function, thereby increasing the balance at 0 cost.
BSC attack transaction: https://www.oklink.com/zh-cn/bsc/tx/0x fb 153 c 572 e 304093023 b 4 f 9694 ef 39135 b 6 e d5 b 2515453173 e 81 ec 0 2d f 2 e 2104
ETH attack transaction: https://www.oklink.com/zh-cn/eth/tx/0x a 6 f 63 fcb 6 bec 8818864 d 96 a 5 b 1 bb 19 e 8 bd 85 ee 37 b 2c c 916412 e 720988440 b 2 aa
BSC attacker address: https://www.oklink.com/zh-cn/bsc/address/0x 83796 2b 686 f d5 a 407 fb 4 e 5 f 92 e 8 be 86 a 230484 bd
ETH attacker address https://www.oklink.com/zh-cn/eth/address/0x 83796 2b 686 f d5 a 407 fb 4 e 5 f 92 e 8 be 86 a 230484 bd
BSC attack contract address (self-destructed): https://www.oklink.com/zh-cn/bsc/address/0x 8445204 2c b 7 be 650 be 4 eb 641025 ac 3 c 8 a 0079 b 67
No.3
On February 4, the revenue automation protocol SperaxUSD on Arbitrum was attacked, resulting in a loss of approximately $300,000. The root cause of the hacker attack is that when the contract exists to migrate the account from rebasing-based to non-rebasing, the premature modification of the account type leads to the use of the non-rebasing mechanism to calculate the balance in advance.
Attack transactions:
https://www.oklink.com/zh-cn/arbitrum/tx/0x e 74641 b 4 b 7 e 9 c 9 eb 7 ab 46082 f 322 efbc 510 b 8 d 39 af 609 d 934 f 41 c 41 d 7057 fe 49
https://www.oklink.com/zh-cn/arbitrum/tx/0x faf 84 cabc 3 e 1 b 0 cf 1 ff 1738 dace 1 b 2810 f 4 2d 98 baeea 17 b 146 ae 032 f 0 bdf 8 2d 5
Attack transactions:
https://www.oklink.com/zh-cn/arbitrum/address/0x 5 c 978 dF 5 F 8 AF 72298 fe 1 c 2C 8 C 2C 05476 a 10 F 2539
https://www.oklink.com/zh-cn/arbitrum/address/0x 4 AfcD 19 bB 978 Eaf 4 F 993814298504 eD 285 df 1181
No.4
On February 7, the TWT project on the BSC chain was attacked, and the hackers made a profit of 137,300 US dollars. The cause of this attack is that the claimReward() function is flawed, and hackers can obtain excess rewards by transferring tokens to the reward contract.
Contract address:
https://www.oklink.com/zh-cn/eth/address/0x d 4 df 22556 e 07148 e 591 b 4 c 7 b 4 f 555 a 17188 cf 5 cf
No.5
Contract address:
Contract address:
https://www.oklink.com/zh-cn/eth/address/0x 9008 d 19 f 58 aabd 9 ed 0 d 60971565 aa 8510560 ab 41
Attack transactions:
https://www.oklink.com/zh-cn/eth/tx/0x 61 a 5196468 b 276 bcedc 3 aab 2 f 2 fe 255 c 2d 54 ca 1 c 655523 f 4 b 25 c 99 b 1 a 224 e 715
No.6
On February 8, the BSC chain HZUSD project was attacked and lost about $70,000. The core of the vulnerability is that the withdrawal function lacks permission restrictions.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/0x cb 9 d 192 f 6 b 846 d 9 adcefa 56382 f 6 cf 60 b 2 e 2b 0 fb
No.7
Contract address:
On February 10, the decentralized financial protocol dforce suffered a read-only reentrancy attack, resulting in a loss of about $3.65 million. The reason for the vulnerability is that the price function get_virtual_price obtains the token ratio, and the raw_call function in the remove_liquidity function can implement an external call to get_virtual_price, causing the attacker to manipulate the price through flashloan.
https://www.oklink.com/zh-cn/optimism/tx/0x 6 c 19762186 c 9 f 3 2c 81 eb 2 a 79420 fc 7 ad 4485 aa 916 cab 37 ec 278 b 216757 bfba 0 d
Optimistic attack transactions:
https://www.oklink.com/zh-cn/arbitrum/tx/0x 5 db 5 c 2400 ab 56 db 697 b 3 cc 9 aa 02 a 05 deab 658 e 1438 ce 2 f 869 2c a 009 cc 45171 dd
arbitrum attack transaction:
ETH:https://www.oklink.com/zh-cn/eth/address/0x e 0 d5 51017 c 0111 ac 11108641771897 aa 33 b 2817 c
Optimistic:https://www.oklink.com/zh-cn/optimism/address/0x e 0 d5 51017 c 0111 ac 11108641771897 aa 33 b 2817 c
Arbitrum:https://www.oklink.com/zh-cn/arbitrum/address/0x e 0 d5 51017 c 0111 ac 11108641771897 aa 33 b 2817 c
Hacker address:
https://www.oklink.com/zh-cn/arbitrum/address/0x 6 eb 2d c 694 eb 516 b 16 dc 9 fbc 678 c 6005 2b bdd 7 d 80
Arbitrum attacked contract:
https://www.oklink.com/zh-cn/optimism/address/0x b 90 b 9 b 1 f 91 a 01 ea 22 a 18 2c d 84 c 1 e 22222 e 39 b 415
No.8
Optimistic attacked contract:
No.9
On Feb. 17, decentralized exchange aggregator Dexible was attacked, losing a combined $2 million on Ethereum and Arbitrum. The core of the vulnerability is that the Dexible v2 contract allows users to define their own transaction routes through the selfSwap function. However, this function does not check whether the router address is really a DEX contract by using the on-chain permission list. The router address was not verified on-chain in any way, meaning hackers could call the token contract directly and transfer tokens from any account authorized on the Dexible contract.
Attacker address:
ETH:https://www.oklink.com/zh-cn/eth/address/0x 684083 f 312 ac 50 f 538 cc 4 b 634 d 85 a 2 feafaab 77 a
BSC:https://www.oklink.com/zh-cn/bsc/address/0x 684083 f 312 ac 50 f 538 cc 4 b 634 d 85 a 2 feafaab 77 a
Arbitrum:https://www.oklink.com/zh-cn/arbitrum/address/0x 684083 f 312 ac 50 f 538 cc 4 b 634 d 85 a 2 feafaab 77 a
Attacker address:
https://www.oklink.com/zh-cn/eth/tx/0x 138 daa 4 cbeaa 3d b 42 eefcec 26 e 234 fc 2c 89 a 4 aa 17 d 6 b 1870 fc 460 b 2856 fd 11 a 6
No.10
On February 24, Shata Capital's EFVault was attacked and lost about $5.1 million. The reason for the problem was an error in the upgrade.
Attack transactions:
https://www.oklink.com/zh-cn/eth/tx/0x 1 fe 5 a 53405 d 00 ce 2 f 3 e 15 b 214 c 7486 c 69 cbc 5 bf 165 cf 9596 e 86 f 797 f 62 e 81914
https://www.oklink.com/zh-cn/eth/tx/0x 3156584 3d 565 ecab 7 ab 65965 d 180 e 45 a 99 d 4718 fa 19 2c 2 f 2221410 f 65 ea 03743
Attack transactions:
https://www.oklink.com/zh-cn/eth/address/0x 8 b 5 a 8333 ec 27 2c 9 bca 1 e 43 f 4 d 009 e 9 b 2 fa d5 efc 9
No.11
Attack contract:"On February 27, the SwapXOfficial project on the BSC chain was attacked and lost $1 million, and the hacker made a profit of about $313,000. The core of the vulnerability is that there is a permission control defect in the purchase function. After the hacker purchases tokens,"Attack transactions:
Attack transactions:
https://www.oklink.com/zh-cn/bsc/tx/0x b 05164989 d 3 ccefd 68 e 81791841 c 20723 e 6 cfcaf 980 e 9 bcb d5 06 d 8551173 eedb
Attacker address:
https://www.oklink.com/zh-cn/bsc/address/0x 2 c 1 f 05 e 120710 de 792061031 cfb 05847 ce 53 fc 56
secondary title
https://www.oklink.com/zh-cn/bsc/address/ 0 x c 4 bea 60 f 5644 b 20 ebb 4576 e 34 d 84854 f 9588 a 7 e 2
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 0 ccee 62 efec 983 f 3 ec 4 bad 3247153009 fb 483551
1.2 RugPull Inventory
No.1
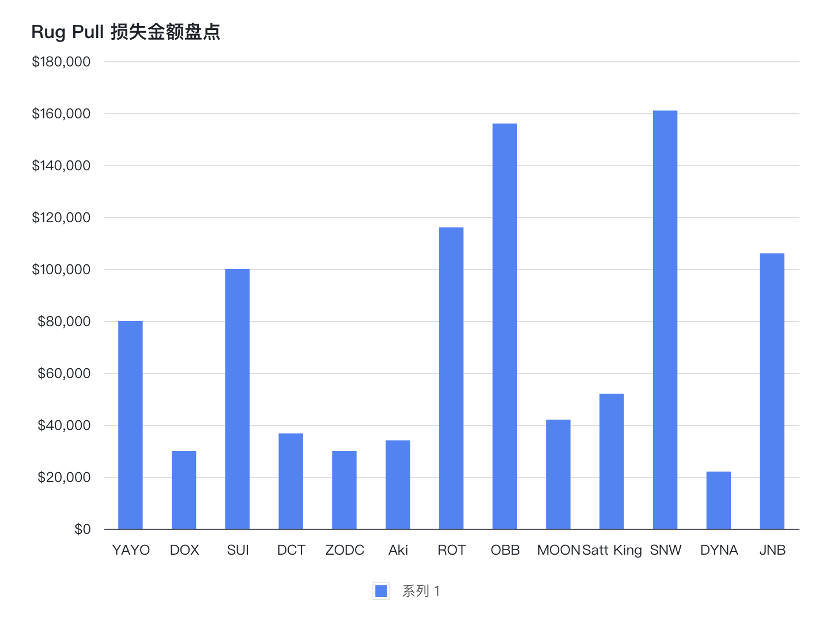
On February 5th, the polygon chain YAYO project was suspected of RugPull, the attacker removed $80,000 in liquidity, and the price of YAYO fell by more than 81%.
Contract address:
https://www.oklink.com/zh-cn/polygon/token/ 0 x 078 f 358208685046 a 11 c 85 e 8 ad 32895 ded 33 a 249
No.2
On February 5th, the BSC chain DOXED (DOX) was suspected of RugPull, the attacker removed $30,000 in liquidity, and the price of YAYO fell by more than 99%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x eda 3 eb 7 a 5494443 beb 800 cd 4 cc 70388228 cee 84 e
No.3
On February 6, the BSC chain SUI project was suspected of RugPull, involving more than $100,000.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 29 bb 058 cc 9 f 11 ec 778 a 6691 a 4 ea 4 c 54186837112
No.4
On February 6, a RugPull occurred in the DCT project of the BSC chain. The attacker removed the liquidity of 27,000 US dollars and exchanged the DCT in his hand for 9,700 USDT.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 48 a 0 b 5 f 2 d 0 f 36598 f 470334 f 4 fe 21900 bf 2 b f 71 b
No.5
On February 6, a RugPull occurred in the BSC chain ZODC project, and the deployer removed the liquidity and made a profit of 30,000 US dollars.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 436 f 510 a 72 f 7972996 b 07 dc 2 edeafa 26308539 e 7
No.6
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 4 b 6 cb 2 b f 1 f 0 b 594 d 0211 c 4 df 2 b 0 dd 1 aa 4 c 7 a 1892
No.7
On February 9th, Rug pull was suspected to have occurred in the BSC chain ROT project, and the amount of liquidity removed was 116,000 US dollars.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x c 631 a 358 c 9 ef 5 da 18144 a 185 b 7122735 d 4 c 04 be 9
No.8
On February 9, a RugPull occurred in the OBB project of the BSC chain, the OBB currency price fell by more than 98%, and the attacker made a profit of 156,000 US dollars.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x d 23 b 64 dbd 334 d 1 2 c 38 f 09 cc 9 eb 23350 aa 1034 c 30
No.9
On February 10, a RugPull occurred in the BSC chain MOON project, the price of MOON currency fell by more than 99%, and the attacker's vitality was 42,000 US dollars.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 5 a 6 b 8 dad 07 2 b b 9257 dcd 6 b 3125126 c 0637 aa 2 f 0 a
No.10
On February 11, a RugPull occurred in the BSC chain MHT project, and the currency price fell by more than 50%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 5 cb 2 c 3 ed 882 e 37 da 610 f 9 ef 5 b 0 fa 25514 d 7 bc 85 b
No.11
On February 11, a RugPull occurred in the BSC chain BAT project, and the currency price fell by more than 88%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 8 d 9 b 0 d 8 cbb 313969059 a 029322 a 3911059087899
No.12
On February 13, a RugPull occurred in the BSC chain SwtAi project, and the currency price fell by more than 88%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 8741021 bd 9 f 7124 e 5 fcb 638 c 1 b 3 c 181260 a 99022
No.13
On February 19, RugPull occurred on the BSC chain SATT KING (Satt King) project, which was sold at a price of about 52,000 US dollars, and the currency price fell by more than 99%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 2682 2 d 43 f 34224707 e 267 e 6496 a 3 f 2 2 c f 8478 bdd
No.14
On February 19, a RugPull occurred in the TG project of the BSC chain, and the currency price fell by more than 95%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 7 3 d 4 f 19933 ad 86 cc 004 bf 5 de 696 b 1 f 1 e 64 ec 6377
No.15
On February 22, a RugPull occurred in the BSC chain SNW project, the attacker made a profit of 161,000 US dollars, and the currency price fell by 97%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 8 aa 19 e 10 d 5 2817 cacba 5 ee 066 eff 38330 c 900223
No.16
On February 22, a RugPull occurred in the BSC chain DYNA project, the attacker made a profit of 22,000 US dollars, and the currency price fell by 93%.
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 5 c 0 d 0111 ffc 63880 2 c 9 efccf 55934 d 5 c 63 ab 3 f 79
No.17
secondary title
Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x 9119 e 3 f 30 c 18 b 9 e 6 b 16 ab 6589534391 e 5 e 4 a 5653
1.3 Social Media Fraud and Phishing Inventory
No.1
1.3 Social Media Fraud and Phishing Inventory
No.2
On February 1, the Discord server of the Rektdogs project was attacked, and the attacker posted phishing messages.
No.3
On February 1, Discord of the Squishiverse project was attacked, and the attacker posted phishing messages.
No.4
On February 1, the Discord server of the realmhunterio project was attacked, and the attacker posted false news.
No.5
On February 1, the Discord server of the oogyNFT project was attacked, and the attacker released false news.
No.6
On February 1, the Discord server of the SoDeadNFT project was attacked, and the attacker released false news.
No.7
On February 1, the Discord server of the Candies_NFT project was attacked, and the attacker released false news.
No.8
On February 2, the Discord server of TheSquaresNFTs project was attacked, and the attacker released false news.
No.9
On February 2, the Twitter of the SuperordinaryF project was stolen, and the attacker posted false news.
No.10
On February 3, the Twitter and Discord servers of the OogaVerse project were stolen, and the attackers posted false news.
No.11
On February 4th, the Discord server of the gemxyz project was compromised, and the attacker posted false news.
No.12
On February 5th, the Discord server of the loudpunxnft project was compromised, and the attacker posted false news.
No.13
On February 6, the Discord server of the 3 mojiHQ project was compromised, and the attacker posted false news.
No.14
On February 7, the Twitter of the ChimpersNFT project was stolen, and the attacker posted false news.
No.15
On February 7, the fake Twitter account subberxyz posted false news.
No.16
On February 7, the Discord server of the EXONIKS_NFTs project was compromised, and the attacker released false news.
No.17
On February 7, the Discord server of the ScarecrowwNft project was compromised, and the attacker released false news.
No.18
On February 8, the Discord server of the DrunkenApeSC project was compromised, and the attacker posted false news.
No.19
On February 8, the Discord server of TheWanderverse_ project was stolen, and the attacker posted false news.
No.20
On February 10, the Twitter account of the weaboveofficial project was compromised, and the attacker posted false news.
No.21
On February 11, the Discord server of the FusionXnft project was compromised, and the attacker posted false news.
No.22
On February 14, the Discord server of the Yosei_NFT project released false news.
No.23
On February 14, the fake account LidoFinance released a phishing message.
No.24
On February 15, the Discord server of the PRJTzumi project was compromised, and the attacker posted false news.
No.25
On February 15, the Discord server of the ssv_network project was compromised, and the attacker released false news.
No.26
On February 15, the Discord server of the Undeadscom project was compromised, and the attackers posted false news.
No.27
On February 16, the Discord server of the arts_dao project was stolen, and the attacker released false news.
No.28
On February 18, the Discord server of the OkCat_NFT project was stolen, and the attacker released false news.
No.29
On February 18, the fake account RealFlokiInu released a phishing message.
No.30
On February 19, the fake account compusophy released a phishing message.
No.31
On February 20, the fake account API 3 D AO released a phishing message.
No.32
On February 20, the Discord server of the gitcoin project was compromised, and the attacker released false news.
No.33
On February 21, the fake account garbagefriends posted a phishing message.
No.34
On February 21, the fake account CyberBotsNFT released a phishing message.
No.35
On February 21, the Discord server of the fwenclub project was compromised, and the attacker released false news.
No.36
On February 22, the fRiENDSiES_Ai project was confirmed as a scam.
No.37
On February 22, the Discord server of the DaosaurNFT project was stolen, and the attacker released false news.
No.38
On February 22, the fake account STFX_IO released a phishing message.
No.39
On February 22, the fake account blur_io posted a phishing message.
No.40
On February 23, the Discord server of the Level__Finance project was stolen, and the attacker released false news.
No.41
On February 24, the Discord server of the CryptoRubic project was stolen, and the attacker posted false news.
No.42
On February 24, the fake account arbitrum posted a phishing message.
No.43
On February 25, the Discord server of the MurAll_art project was compromised, and the attacker posted false news.
No.44
On February 25, the fake account lBlur_io posted a phishing message.
No.45
On February 25, the Discord server of the EldritchOrdr project was compromised, and the attacker posted false news.
No.46
secondary title
1.4 Others
No.1
1.4 Others
https://www.oklink.com/zh-cn/bsc/address/ 0 x 62 e 8 e 3036964 e 9 cfa 21 e 970 e 8257 b 27 f 487175 d 8
No.2
On February 7, the private key of the LianGoProtocol project of the BSC chain was leaked, the currency price fell by more than 97%, and the amount lost exceeded 1.6 million US dollars. Contract address:
https://www.oklink.com/zh-cn/bsc/address/ 0 x c 91 f 7096 ff 24 b 8 caee 44 f 7 c 0 c 94 b 00 b 70 cec 682 a
No.3
On February 12, the private key of the BSC chain MMT project was leaked, the currency price fell by more than 79%, and the amount lost exceeded 62,000 US dollars. Contract address:
No.4
first level title
2. Safety summary
2. Safety summary





