






SushiSwap MISO Platform Hacked, Over $3 Million in ETH Stolen


This article comes fromDecrypt, original author: Andrew Asmakov
Odaily Translator | Nian Yin Si Tang
This article comes from
, original author: Andrew Asmakov
Odaily Translator | Nian Yin Si TangAccording to reports, SushiSwap's Launchpad platform MISO was attacked, and hackers stole 864.8 ETH, worth more than $3 million at current prices.SushisSwap is one of the largest decentralized exchanges (DEX) in the world and a competitor of Uniswap. According to CoinCecko data, as of press time, SushisSwap has traded more than $495 million in the past 24 hours.
as the project
As stated on the official website
, MISO is "a set of open source smart contracts designed to simplify the process of listing new projects on the SushisSwap exchange."
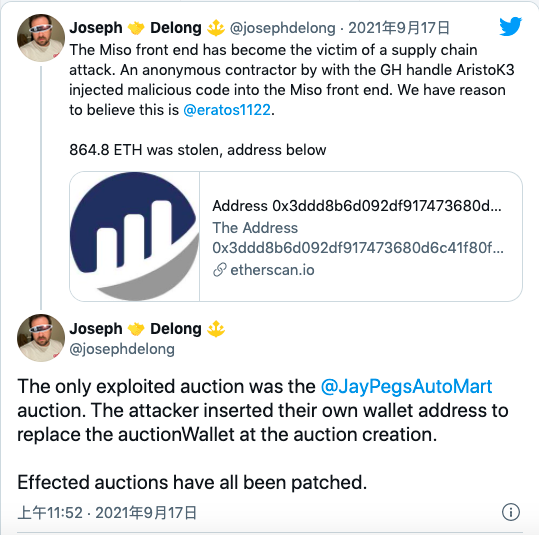
According to Joseph Delong, chief technology officer of SushiSwap, MISO was hit by a so-called supply chain attack. An anonymous contractor injected malicious code into the front end of the MISO platform under Handler AristoK3 of GitHub, and replaced the wallet address of the auction with his own wallet address.
Note: According to Baidu Baike, supply chain attacks are an emerging threat to software developers and suppliers. The goal is to distribute malware by infecting legitimate applications to gain access to source code, build processes, or update mechanisms.
Affected this time is the DONA token of the car-themed NFT project Jay Pegs Auto Mart. This vulnerability has been fixed now.According to data from the Ethereum blockchain browser Etherscan, the attack took place at 12:04 pm U.S. Eastern Time on Thursday (that is, 0:04 on September 17, Beijing time), and the company has identified the hacker address disclosed by Delong as involving MISO. The address of the attack.This is actually not the first time that MISO has encountered similar problems, but the last time it was spared because of "the help of noble people".
author disclosureTweetBitDAO previously conducted a Dutch auction on the SushiSwap MISO platform with security vulnerabilities. Several white hat hackers teamed up to save 109,000 ETH (about 350 million U.S. dollars) from the crowdfunding pool. Joseph Delong, chief technology officer of SushiSwap, then released a vulnerability analysis, confirming the vulnerability reported by samczsun and the white hat rescue operation, and the $350 million worth of ETH in the ETH crowdfunding pool on the MISO platform is now safe.
According to samczsun, this may be the largest white hat rescue operation. This white hat rescue operation led to the early termination of the ETH fund pool of BitDAO's Dutch auction on the MISO platform, and participants can receive BIT tokens in advance and trade them on SushiSwap. Paradigm research team members, Immunefi team members and SushiSwap development team participated in this action. Ten days later, DelongTweetThe auction at that time was successfully concluded, and in the process
$365 million raised
. It is worth mentioning that MISO asked the BitDAO team to manually close the token auction to eliminate potential threats.
secondary title
Is the hacker identity locked?
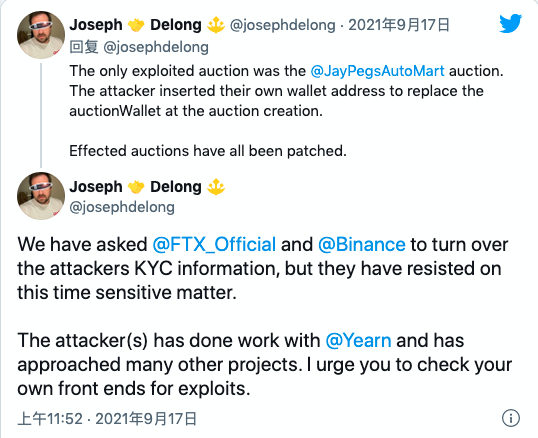
SushiSwap claims to have reason to believe the hacker is Twitter user @eratos1122, who "has worked with Yearn.Finance and had exposure to many other projects."
"I recommend that you test your user interface to catch bugs early on," Delong said.
renew:
He also said he would instruct the company's lawyer, Stephen Palley, to report the case to the FBI if the stolen funds were not returned by 8 a.m. ET on Friday.





